Need an MSP?
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs


Modern Security Access Systems: Complete Guide for Business Implementation
Is your business still relying on physical keys that can be lost, copied, or stolen? Are you struggling to track who accesses your facilities and when? Can you instantly revoke access when an employee leaves? If these questions keep you …
Is your business still relying on physical keys that can be lost, copied, or stolen? Are you struggling to track who accesses your facilities and when? Can you instantly revoke access when an employee leaves? If these questions keep you …
Read full post on networkright.com
MSPdb™ News
How to Choose the Right IT Consulting Company
To choose the right IT consulting company, start by defining your IT needs, goals, and project requirements, then determine the IT consulting services and engagement model you need. Research and shortlist suitable companies, evaluate each provider’s technical and industry expertise, and assess the proposed consulting team’s experience and capability. Next, review project delivery, communication, and... Source
To choose the right IT consulting company, start by defining your IT needs, goals, and project requirements, then determine the IT consulting services and engagement model you need. Research and shortlist suitable companies, evaluate each provider’s technical and industry expertise, and assess the proposed consulting team’s experience and capability. Next, review project delivery, communication, and... Source
Read full post on cloudavize.com
Unlocking Scalable Growth: The Financial Case for Professional IT Consulting Services
Quick answer: Professional IT consulting helps growing businesses make smarter tech decisions without the painful trial and error. The right consultant keeps your systems secure, your infrastructure ready to scale, and your team focused on real work. For most businesses, that investment pays for itself fast through less downtime, fewer security nightmares, and a tech
Quick answer: Professional IT consulting helps growing businesses make smarter tech decisions without the painful trial and error. The right consultant keeps your systems secure, your infrastructure ready to scale, and your team focused on real work. For most businesses, that investment pays for itself fast through less downtime, fewer security nightmares, and a tech
Read full post on totalit.com
How Smart Businesses Measure Real Output Without Spying on Employees
Tracking every single click might sound like an easy way to make sure your team is actually working, but it backfires fast. Invasive surveillance ruins company culture, kills creativity, and drives your best talent straight to the exit. Real leadership is about building a system that measures real progress without destroying trust.
Tracking every single click might sound like an easy way to make sure your team is actually working, but it backfires fast. Invasive surveillance ruins company culture, kills creativity, and drives your best talent straight to the exit. Real leadership is about building a system that measures real progress without destroying trust.
Read full post on coretechllc.com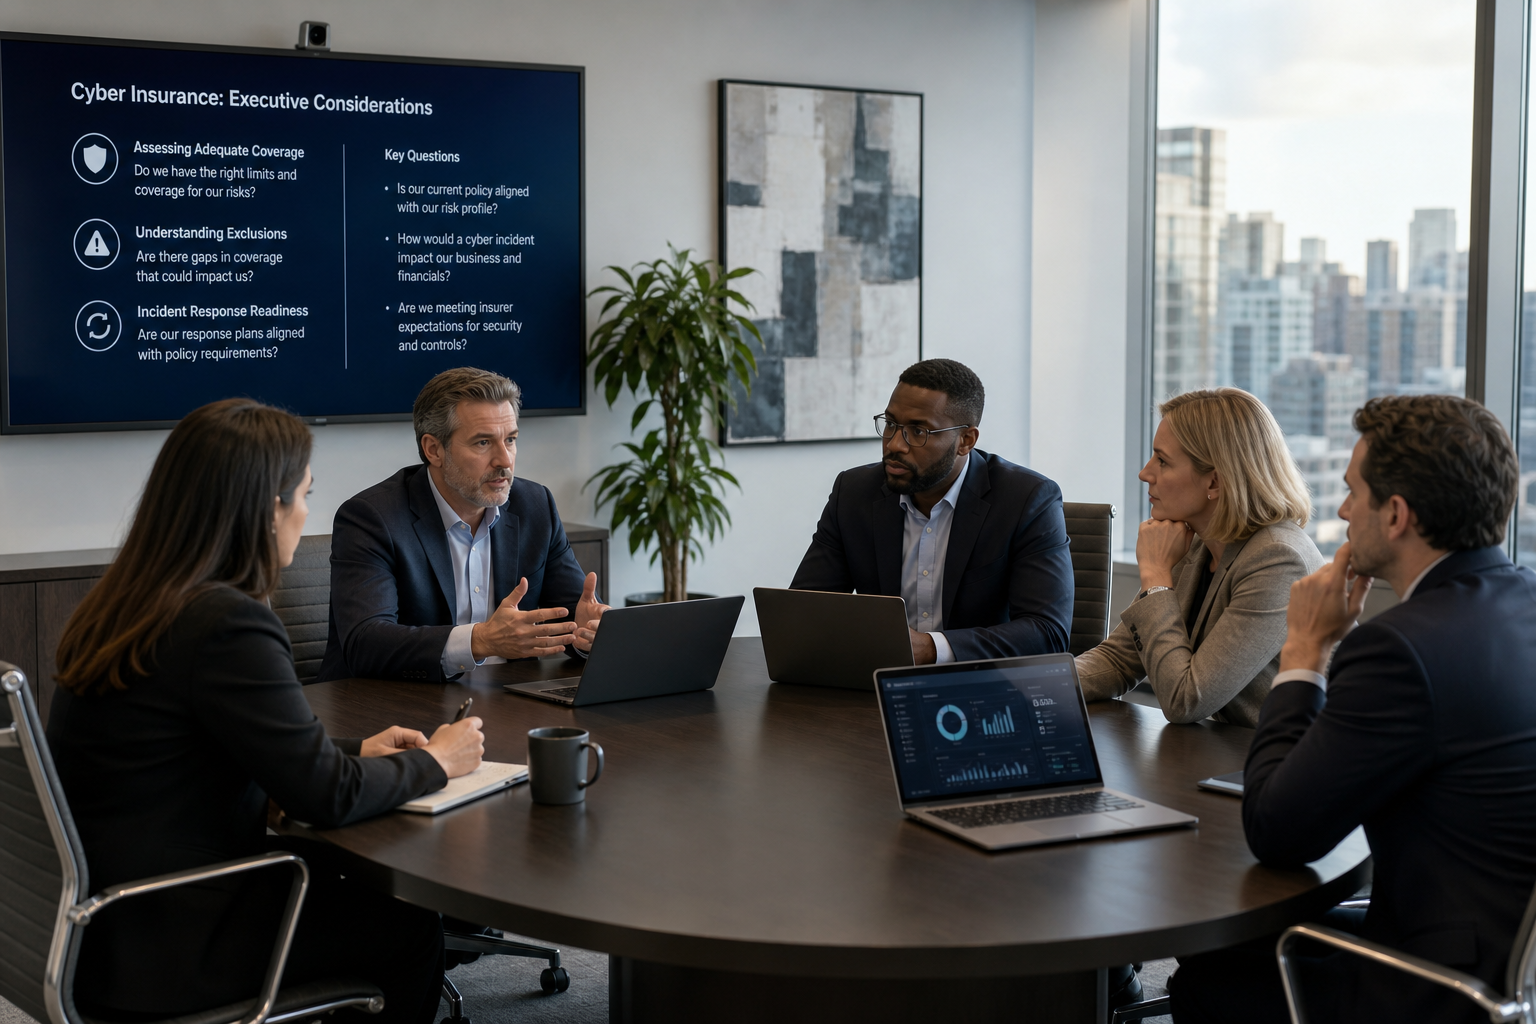
Five Questions Every Executive Should Bring to a Cyber Insurance Discussion
Five Questions Every Executive Should Bring to a Cyber Insurance Discussion Cyber insurance conversations are no longer limited to annual policy renewals. As cyber threats grow and insurance requirements evolve, executive leaders need a deeper understanding of how organizational decisions affect insurability, resilience, and business continuity. Unfortunately, many leaders enter cyber insurance discussions without knowing what questions they should ask. The result is often missed opportunities, misunderstood risks, and unexpected challenges during underwriting or claims reviews. To h
Five Questions Every Executive Should Bring to a Cyber Insurance Discussion Cyber insurance conversations are no longer limited to annual policy renewals. As cyber threats grow and insurance requirements evolve, executive leaders need a deeper understanding of how organizational decisions affect insurability, resilience, and business continuity. Unfortunately, many leaders enter cyber insurance discussions without knowing what questions they should ask. The result is often missed opportunities, misunderstood risks, and unexpected challenges during underwriting or claims reviews. To help leaders prepare, here are five important questions every executive should bring to the conversation. Question #1: How Would an Insurer Evaluate Our Organization Today? Most organizations have an internal perspective of their cybersecurity program. Insurance carriers bring an external perspective. Their evaluation often focuses on: Security controls Documentation Governance Operational maturity Organizational risk Understanding how an insurer views the organization may reveal risks leadership has not previously considered. Question #2: Can We Demonstrate Our Security Controls? Having a control and proving a control exists are very different things. Executives should ask: Is MFA fully deployed? Is vulnerability management documented? Is employee training tracked? Are security policies current? Proof matters. Documentation often becomes just as important as implementation. Question #3: What Are Our Most Significant Underwriting Risks? Every organization has areas for improvement. Identifying underwriting concerns early allows organizations to make strategic improvements before renewal discussions begin. Examples may include: Legacy technology Weak identity management Limited security awareness programs Incomplete documentation Proactive organizations generally have more options. Question #4: Could a Denied Claim Impact Business Continuity? Executives frequently focus on obtaining coverage but may spend less time understanding coverage assumptions and requirements. A denied or disputed claim can create significant financial challenges. Organizations should understand: Coverage limitations Security obligations Documentation expectations Renewal requirements This knowledge helps reduce unpleasant surprises during a crisis. Question #5: What Should We Prioritize During the Next 12 Months? Cybersecurity improvements can feel overwhelming. The most successful organizations focus on strategic priorities rather than attempting to address everything simultaneously. Leaders should identify: High-impact improvements Highest-risk exposures Governance enhancements Documentation needs Insurance readiness initiatives These efforts often produce both security and business benefits. What Executives Will Learn During the Webinar The upcoming OXEN webinar is designed specifically to help organizational leaders better understand: Today's cyber insurance landscape Why claims become complicated How insurers assess risk What cybersecurity controls matter most Practical steps for improving readiness This is not a highly technical discussion. It is a business-focused conversation designed for executive decision-makers. Final Registration Opportunity Organizations that wait until renewal season often find themselves reacting under pressure. Organizations that prepare early gain more flexibility, stronger security, and improved confidence. Register Today Join OXEN Technology and The Agency Insurance to gain practical guidance that can help strengthen both cybersecurity maturity and insurability.
Read full post on oxen.tech
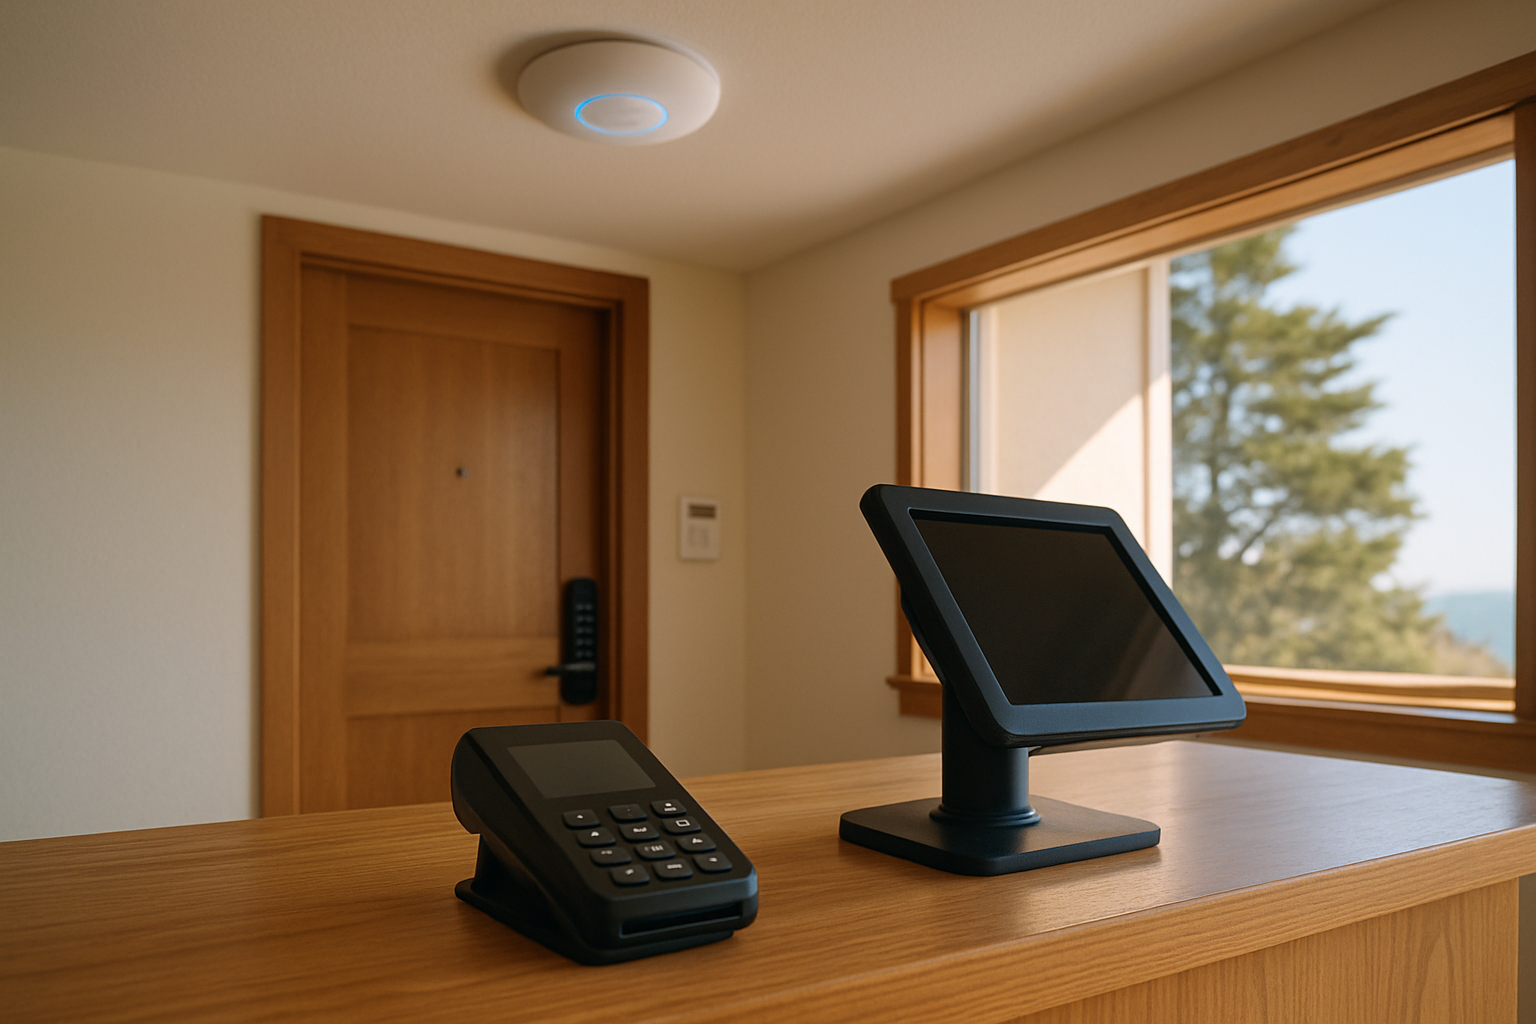
Guest WiFi, Card Readers, and Smart Locks: Who Shares Your Network?
Direct Answer: Guest WiFi segmentation puts visitors in their own network lane, separated by VLANs and firewall rules, so a guest device cannot reach your card reader, printer, cameras, or office computers. A small inn on the Monterey Peninsula reached out to us with a problem that sounded simple. Their wireless had stopped behaving, the
Direct Answer: Guest WiFi segmentation puts visitors in their own network lane, separated by VLANs and firewall rules, so a guest device cannot reach your card reader, printer, cameras, or office computers. A small inn on the Monterey Peninsula reached out to us with a problem that sounded simple. Their wireless had stopped behaving, the
Read full post on adaptiveis.net
Your Team Is Already Using AI. Here's Why Shadow AI is a Leadership Problem
Avoid OCR Penalties: $143M, HIPAA Security Rule for U.S. Practices
A practical U.S. compliance atlas that maps HHS and NIST guidance to SMB actions. Get OCR ready: documented risk analysis, NIST mappings, and 6 month scans.
A practical U.S. compliance atlas that maps HHS and NIST guidance to SMB actions. Get OCR ready: documented risk analysis, NIST mappings, and 6 month scans.
Read full post on mytekrescue.com
7 Steps in a Small Business Disaster Recovery Guide
This small business disaster recovery guide helps California leaders protect data, restore systems quickly, and keep teams productive after disruption.
This small business disaster recovery guide helps California leaders protect data, restore systems quickly, and keep teams productive after disruption.
Read full post on rj-pro.net

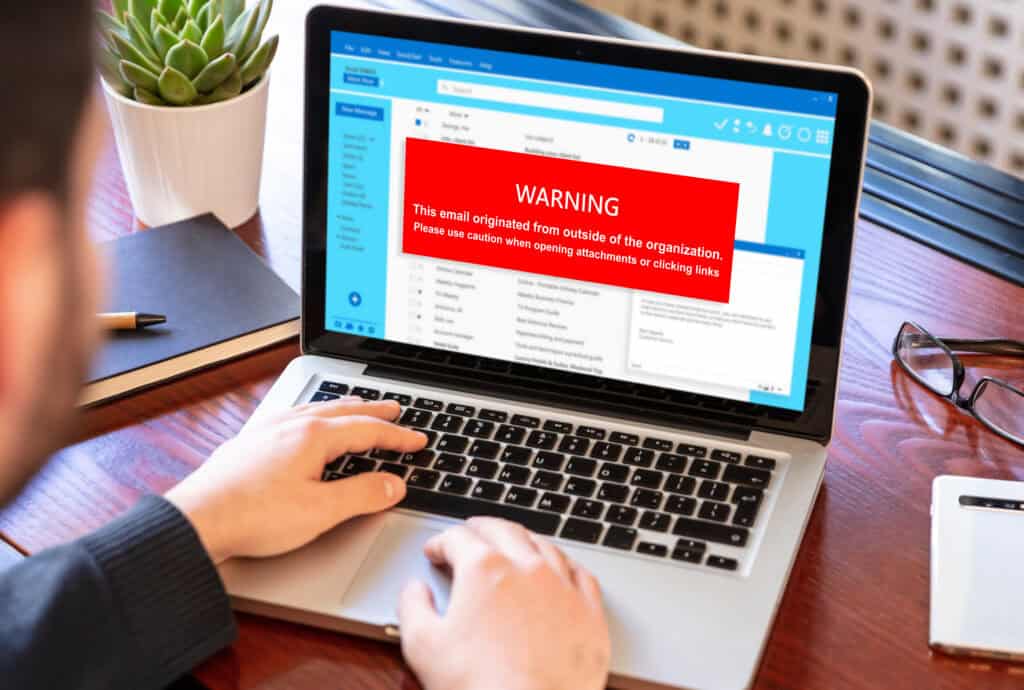
Easy Phishing Simulations Create False Confidence
Executive Summary: Why Easy Phishing Tests Miss Real Risk A client had been sending phishing simulations for years. The metrics looked good and the test emails were being identified. But real phishing emails were still getting clicks, even from the leadership team. Virtuas introduced a custom phishing simulation for the client, one based on a
Executive Summary: Why Easy Phishing Tests Miss Real Risk A client had been sending phishing simulations for years. The metrics looked good and the test emails were being identified. But real phishing emails were still getting clicks, even from the leadership team. Virtuas introduced a custom phishing simulation for the client, one based on a
Read full post on virtuas.com
Managed IT Services for Schools: A Scope Checklist for School Leaders
Define what your school, IT provider and outside vendors each handle. Use the scope worksheet to compare responsibilities, coverage, exclusions and evidence.
Define what your school, IT provider and outside vendors each handle. Use the scope worksheet to compare responsibilities, coverage, exclusions and evidence.
Read full post on ctmsit.com
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All