Compliance updates for CMMC, HIPAA, PCI DSS, SOC 2, and NIST-driven security programs.
MSPdb™ News
CMMC Readiness San Diego: Access Control and Audit Evidence Assessors Actually Check
CMMC readiness San Diego defense contractors need: access control, MFA, and audit logs with evidence an assessor can trace before Level 2.
CMMC readiness San Diego defense contractors need: access control, MFA, and audit logs with evidence an assessor can trace before Level 2.
Read full post on fitsolutions.biz
FTC & Data Privacy Compliance: What Small-to-Midsize Businesses Must Audit Today
Find out essential FTC data privacy standards for small to midsize businesses. Audit your systems and secure sensitive client data today.
Find out essential FTC data privacy standards for small to midsize businesses. Audit your systems and secure sensitive client data today.
Read full post on mytekrescue.com
CMMC Compliance for Defense Subcontractors: What Your Cloud Tools Must Prove
CMMC compliance for defense subcontractors in San Diego: what cloud tools must prove on FedRAMP equivalency, CUI, and shared responsibility.
CMMC compliance for defense subcontractors in San Diego: what cloud tools must prove on FedRAMP equivalency, CUI, and shared responsibility.
Read full post on fitsolutions.biz
AI HIPAA Compliance: What Medical Practices Need to Know
Doctors have embraced AI faster than almost anyone expected. An American Medical Association survey found that 81% of physicians now use AI tools professionally, more than double the rate in 2023. They use it for visit notes, chart summaries, patient portal replies and discharge instructions. Every one of those tasks involves protected health information. That's
Doctors have embraced AI faster than almost anyone expected. An American Medical Association survey found that 81% of physicians now use AI tools professionally, more than double the rate in 2023. They use it for visit notes, chart summaries, patient portal replies and discharge instructions. Every one of those tasks involves protected health information. That's
Read full post on agjsystems.com
Is Microsoft 365 HIPAA Compliant? PHI Setup Checklist
Yes, Microsoft 365 can support a HIPAA-aligned medical practice when the right agreement and settings are in place. This guide shows how to confirm Microsoft's Business Associate Agreement (BAA), what to configure in each app, and what to heck before patient records move.
Yes, Microsoft 365 can support a HIPAA-aligned medical practice when the right agreement and settings are in place. This guide shows how to confirm Microsoft's Business Associate Agreement (BAA), what to configure in each app, and what to heck before patient records move.
Read full post on kairosit.com
How to Evaluate IT Support Vendor Security Capabilities for Regulatory Compliance
When you sign a multi-year contract with an IT support vendor, you’re not just buying helpdesk tickets and network monitoring. You’re handing them administrative access to your financial data, customer records, regulated workloads, and business continuity infrastructure. If that vendor suffers a breach or fails an audit, your organization owns the regulatory consequences. Yet most... <p>
When you sign a multi-year contract with an IT support vendor, you’re not just buying helpdesk tickets and network monitoring. You’re handing them administrative access to your financial data, customer records, regulated workloads, and business continuity infrastructure. If that vendor suffers a breach or fails an audit, your organization owns the regulatory consequences. Yet most... <p>
Read full post on xitx.com
SOC 2 vs ISO 27001 for small businesses: How to Compare
SOC 2 vs ISO 27001 for small businesses: compare outcomes, scope, evidence, and upkeep, then choose an assurance path that fits customer needs.
SOC 2 vs ISO 27001 for small businesses: compare outcomes, scope, evidence, and upkeep, then choose an assurance path that fits customer needs.
Read full post on igtech365.com
CMMC Compliance IT Support: What Manufacturers Actually Need From a Provider
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2:first-child,.blog-post-container>h3:first-child{margin-top:0 !important;}.blog-post-container p{margin-bottom:1.25em !important;}.blog-post-container ul,.blog-post-container ol{margin:0 0 1.6em 1.4em !important;padding:0 !important;}.blog-post-container li{margin-bottom:0.55em !important;}.blog-post-container blockquote{margin:1.8em 0 !important;padding:1.2em 1.6em !important;border-left:4px solid #ccc !important;background:#222222 !important;}.blog-post-container .table-of-contents{background:#1a1f2e !important;border:1px solid #2a3040;padding:1.2em 1.5em;border-radius:8px;margin:1.5em 0;}.blog-post-container .table-of-contents h4{margin-top:0 !important;margin-bottom:0.8em !important;color:#e0e0e0 !important;font-size:1.1em;}.blog-post-container .table-of-contents ul{margin:0 !important;padding-left:1.2em !important;}.blog-post-container .table-of-contents li{margin-bottom:0.4em !important;}.blog-post-container .table-of-contents a{text-decoration:none;color:#60a5fa !important;transition:color 0.2s ease;}.blog-post-container .table-of-contents a:hover{color:#93c5fd !important;text-decoration:underline;}.blog-post-container .key-takeaways{background:#1a2b3c !important;border-left:4px solid #2563eb !important;padding:1.25em 1.5em;margin:1.5em 0;border-radius:0 8px 8px 0;}.blog-post-container .key-takeaways h4{margin-top:0 !important;margin-bottom:0.75em !important;color:#60a5fa !important;font-weight:700;}.blog-post-container .key-takeaways ul{margin-bottom:0 !important;}.blog-post-container .key-takeaways li{margin-bottom:0.6em !important;}.blog-post-container .eyebrow-label{text-transform:uppercase;letter-spacing:1px;color:#888;font-size:0.8em;margin-bottom:8px;font-weight:500;}.blog-post-container .callout,.blog-post-container .quick-answer,.blog-post-container .highlight-box{padding:20px 20px 20px 50px !important;margin:2em 0 !important;border-left:5px solid;border-radius:5px !important;position:relative;}.blog-post-container .callout-tip,.blog-post-container .quick-answer{display:block !important;position:relative !important;padding:16px 20px 16px 56px !important;margin:1.5em 0 !important;border-left:5px solid #2e77b5 !important;background:#1a2b3c !important;border-radius:6px !important;line-height:1.6 !important;}.blog-post-container .callout-info,.blog-post-container .highlight-box{border-color:#3498db !important;background:#1c3040 !important;}.blog-post-container .callout-warning{border-color:#c03e26 !important;background:#3d1e1a !important;}.blog-post-container .pros-cons-list{display:grid !important;grid-template-columns:1fr 1fr !important;gap:20px !important;margin:2em 0 !important;padding:0 !important;}.blog-post-container .pros-cons-list>h2,.blog-post-container .pros-cons-list>h3,.blog-post-container .pros-cons-list>h4{grid-column:1 / -1 !important;margin-top:0 !important;}.blog-post-container .pros-list{background:#1a3b2a !important;border:1px solid #c6f6d5 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .pros-list h4{color:#86efac !important;}.blog-post-container .cons-list{background:#3f1f1f !important;border:1px solid #fed7d7 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .cons-list h4{color:#fca5a5 !important;}.blog-post-container .cta-button{display:inline-block;background:#5fc5bd;color:#FFFFFF !important;font-size:18px;font-weight:700;line-height:1;padding:14px 32px;border-radius:32px;letter-spacing:0.5px;text-decoration:none;border:none;outline:none;transition:background-color 0.2s ease-in-out;}.blog-post-container .cta-button:hover{background:#4aa8a1;}.blog-post-container .author-bio-wrapper .author-bio{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container .author-bio-wrapper section{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container table{width:100% !important;max-width:100% !important;table-layout:fixed !important;border-collapse:collapse !important;font-size:0.75em;}.blog-post-container th,.blog-post-container td{padding:0.6em 0.8em !important;white-space:normal !important;word-break:normal !important;overflow-wrap:break-word !important;}@media (max-width:749px){.blog-post-container .pros-cons-list{grid-template-columns:1fr !important;}}@media (max-width:900px){.blog-post-container table{display:block;overflow-x:auto;font-size:0.65em;}} cmmc compliance it support
Read full post on andromeda.tech
Private AI Document Processing for Small Business: Extract Invoice Data Without Third-Party Risk
Small businesses process hundreds of invoices monthly. Most still use humans to type vendor names, amounts, and dates into accounting systems. The AI hype machine promises instant automation, but every mainstream tool sends your financial documents to someone else’s server. That’s a non-starter if you care about confidentiality, client trust, or regulatory exposure. Private AI... <p>
Small businesses process hundreds of invoices monthly. Most still use humans to type vendor names, amounts, and dates into accounting systems. The AI hype machine promises instant automation, but every mainstream tool sends your financial documents to someone else’s server. That’s a non-starter if you care about confidentiality, client trust, or regulatory exposure. Private AI... <p>
Read full post on xitx.com
CMMC Compliance Checklist for Manufacturers: A Practical, Phased Path from Scoping to SPRS
HIPAA Compliant IT Services for Senior Living: How to Be Audit-Ready at Every Facility
HIPAA compliant IT services for senior living and skilled nursing: risk analysis, access controls, and backups that hold up in surveys and audits.
HIPAA compliant IT services for senior living and skilled nursing: risk analysis, access controls, and backups that hold up in surveys and audits.
Read full post on fitsolutions.biz
Cyber insurance compliance doesn’t end when your policy is approved
Your cyber insurance application was approved. The paperwork is filed, your premiums are paid, and your business is covered for another year. But six months later, is your IT environment still the same one you described to your insurer? Maybe you’ve hired three new employees, introduced a cloud platform, changed how your team accesses company...
Your cyber insurance application was approved. The paperwork is filed, your premiums are paid, and your business is covered for another year. But six months later, is your IT environment still the same one you described to your insurer? Maybe you’ve hired three new employees, introduced a cloud platform, changed how your team accesses company...
Read full post on daxtech.ca
Data Retention Policy: What to Keep, How Long, and How
Build a data retention policy your small business can follow: retention periods for HIPAA, IRS and SEC records, secure destruction steps, and a simple schedule.
Build a data retention policy your small business can follow: retention periods for HIPAA, IRS and SEC records, secure destruction steps, and a simple schedule.
Read full post on mytekrescue.com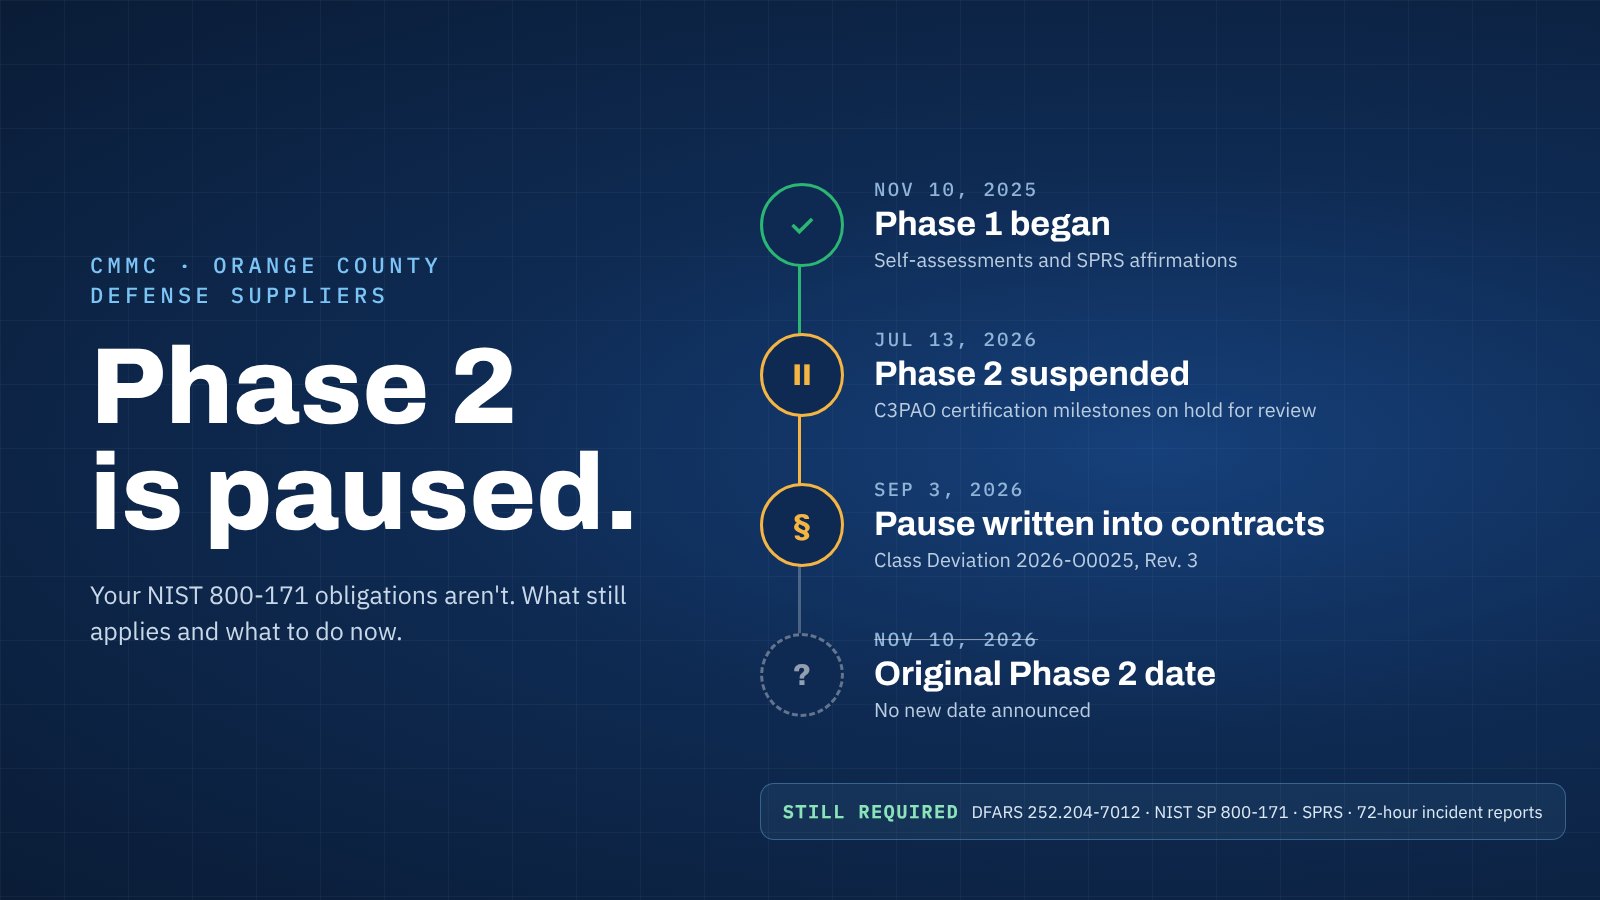
CMMC Phase 2 Is Paused. Here’s What Orange County Defense Contractors Should Do Now
CMMC Phase 2 is paused, but DFARS 7012, NIST 800-171 and SPRS still apply. A plain-English plan for Orange County defense suppliers.
CMMC Phase 2 is paused, but DFARS 7012, NIST 800-171 and SPRS still apply. A plain-English plan for Orange County defense suppliers.
Read full post on calitgroup.com
What Are PCI Compliance Requirements?
Learn what PCI compliance requirements cover, how to map payment data, choose validation, and organize practical safeguards before an assessment.
Learn what PCI compliance requirements cover, how to map payment data, choose validation, and organize practical safeguards before an assessment.
Read full post on igtech365.com
Cybersecurity Compliance Requirements: A Manufacturing Guide to Frameworks, Controls, and Audit Readiness
How a CMMC Enclave Keeps Compliance From Taking Over the Whole Shop
Level 2 doesn't have to mean rebuilding the whole shop. See how scoping a CMMC enclave keeps the 110 practices where they belong.
Level 2 doesn't have to mean rebuilding the whole shop. See how scoping a CMMC enclave keeps the 110 practices where they belong.
Read full post on cnwr.com
Healthcare Ransomware Defense: The Controls Your Practice Should Have Documented
Your cyber insurance renewal, your HIPAA risk assessment, and your daily schedule all depend on one question. If ransomware reached your systems this week, could your practice keep operating, and could you show which controls were in place?
Your cyber insurance renewal, your HIPAA risk assessment, and your daily schedule all depend on one question. If ransomware reached your systems this week, could your practice keep operating, and could you show which controls were in place?
Read full post on kairosit.com
NIST 800-171 Compliance: How to Scope CUI and Build an Enclave That Holds Up
NIST 800-171 compliance starts with scoping CUI correctly. Learn how to build a defensible enclave, close POA&M gaps, and stay assessment-ready.
NIST 800-171 compliance starts with scoping CUI correctly. Learn how to build a defensible enclave, close POA&M gaps, and stay assessment-ready.
Read full post on fitsolutions.biz
Why Your Compliance Audit Takes Weeks Instead of Days
For many organizations, audits do not fail. They just take far longer than they should. A request list comes in, and people start tracking down documentation. Evidence gets pulled from different systems. Policies are reviewed, sometimes rewritten on the fly. Then multiple teams get pulled in to piece everything together under a tight timeline. What should be a straightforward validation ends up taking weeks. There is a lot of coordination, a lot of back and forth, and usually more effort than anyone planned for. The audit itself usually is not the issue. It is everything that happens before it
For many organizations, audits do not fail. They just take far longer than they should. A request list comes in, and people start tracking down documentation. Evidence gets pulled from different systems. Policies are reviewed, sometimes rewritten on the fly. Then multiple teams get pulled in to piece everything together under a tight timeline. What should be a straightforward validation ends up taking weeks. There is a lot of coordination, a lot of back and forth, and usually more effort than anyone planned for. The audit itself usually is not the issue. It is everything that happens before it.
Read full post on synergyits.com
SOC 2 vs. HIPAA: What Each One Requires and Which You Need
SOC 2 is a voluntary audit report. HIPAA is federal law. Learn how they differ, where they overlap and which one your small business actually needs.
SOC 2 is a voluntary audit report. HIPAA is federal law. Learn how they differ, where they overlap and which one your small business actually needs.
Read full post on mytekrescue.com
CMMC Managed Compliance: What Every Defense Contractor Needs to Know
PHI Encryption for Small Practices: 6 Steps From HHS and NIST
HIPAA treats PHI encryption as addressable, not optional. See six practical steps for small U.S. healthcare practices, from risk analysis to key management.
HIPAA treats PHI encryption as addressable, not optional. See six practical steps for small U.S. healthcare practices, from risk analysis to key management.
Read full post on mytekrescue.com
IT Compliance Checklist For Small Businesses
An IT compliance checklist gives small businesses a systematic process to identify regulatory requirements, implement security controls, document policies and procedures, and maintain audit evidence that verifies how the organization protects systems and regulated data. The checklist should cover applicable compliance frameworks, identity and access management, data protection, endpoint security, backup and disaster recovery, incident... Source
An IT compliance checklist gives small businesses a systematic process to identify regulatory requirements, implement security controls, document policies and procedures, and maintain audit evidence that verifies how the organization protects systems and regulated data. The checklist should cover applicable compliance frameworks, identity and access management, data protection, endpoint security, backup and disaster recovery, incident... Source
Read full post on cloudavize.com
GLBA Compliance IT Cost in Texas: What Financial Firms Pay in 2026
GLBA compliance IT cost in Texas runs about $175 to $250 per user a month ... Learn More
GLBA compliance IT cost in Texas runs about $175 to $250 per user a month ... Learn More
Read full post on uprite.com
US Compliance Teams: Make AI for Healthcare Compliance Audit Ready
Practical checklist for US healthcare compliance teams to inventory AI, meet HIPAA, NIST, FDA, ONC, and FTC rules, and be audit ready.
Practical checklist for US healthcare compliance teams to inventory AI, meet HIPAA, NIST, FDA, ONC, and FTC rules, and be audit ready.
Read full post on mytekrescue.com
Third-Party Vendor Risk Is Driving Nearly Half of All Data Breaches
Third-party vendor risk, the exposure created by outside companies and software tools with access to your systems, now plays a role in roughly half of all data breaches. That is not a typo and not a rare worst case. It means the IT contractor, payroll processor, or SaaS app you trust with a login is
Third-party vendor risk, the exposure created by outside companies and software tools with access to your systems, now plays a role in roughly half of all data breaches. That is not a typo and not a rare worst case. It means the IT contractor, payroll processor, or SaaS app you trust with a login is
Read full post on bostonmit.com
What Executives Should Expect From a Business-Focused Microsoft 365 Risk Assessment
What Executives Should Expect From a Business-Focused Microsoft 365 Risk Assessment Most Assessments Miss the Executive Audience Risk assessments are commonly viewed as technical exercises.
What Executives Should Expect From a Business-Focused Microsoft 365 Risk Assessment Most Assessments Miss the Executive Audience Risk assessments are commonly viewed as technical exercises.
Read full post on oxen.tech
Enforceable AI Policy for Employees: Few Pages, NIST and EEOC Aligned
Get an HR-first AI policy for employees: a few pages, NIST and EEOC aligned checklist that enforces disclosure, human review, vendor controls, and...
Get an HR-first AI policy for employees: a few pages, NIST and EEOC aligned checklist that enforces disclosure, human review, vendor controls, and...
Read full post on mytekrescue.com
An MSP’s Role in IT Compliance Audit Preparation
The audit notice arrives, and now someone is digging through old email threads, scrambling to figure out who still has a login to the accounting system. The patch reports are somewhere, but where? Unfortunately, the incident response plan is living mostly in a former employee’s head. Sound familiar? Compliance audits rarely catch businesses off guard
The audit notice arrives, and now someone is digging through old email threads, scrambling to figure out who still has a login to the accounting system. The patch reports are somewhere, but where? Unfortunately, the incident response plan is living mostly in a former employee’s head. Sound familiar? Compliance audits rarely catch businesses off guard
Read full post on lgnetworksinc.com
Failed to load more articles
You're all caught up!
Check back later for more compliance news.
MSPdb™ News
CMMC Readiness San Diego: Access Control and Audit Evidence Assessors Actually Check
CMMC readiness San Diego defense contractors need: access control, MFA, and audit logs with evidence an assessor can trace before Level 2.
CMMC readiness San Diego defense contractors need: access control, MFA, and audit logs with evidence an assessor can trace before Level 2.
Read full post on fitsolutions.biz
FTC & Data Privacy Compliance: What Small-to-Midsize Businesses Must Audit Today
Find out essential FTC data privacy standards for small to midsize businesses. Audit your systems and secure sensitive client data today.
Find out essential FTC data privacy standards for small to midsize businesses. Audit your systems and secure sensitive client data today.
Read full post on mytekrescue.com
CMMC Compliance for Defense Subcontractors: What Your Cloud Tools Must Prove
CMMC compliance for defense subcontractors in San Diego: what cloud tools must prove on FedRAMP equivalency, CUI, and shared responsibility.
CMMC compliance for defense subcontractors in San Diego: what cloud tools must prove on FedRAMP equivalency, CUI, and shared responsibility.
Read full post on fitsolutions.biz
AI HIPAA Compliance: What Medical Practices Need to Know
Doctors have embraced AI faster than almost anyone expected. An American Medical Association survey found that 81% of physicians now use AI tools professionally, more than double the rate in 2023. They use it for visit notes, chart summaries, patient portal replies and discharge instructions. Every one of those tasks involves protected health information. That's
Doctors have embraced AI faster than almost anyone expected. An American Medical Association survey found that 81% of physicians now use AI tools professionally, more than double the rate in 2023. They use it for visit notes, chart summaries, patient portal replies and discharge instructions. Every one of those tasks involves protected health information. That's
Read full post on agjsystems.com
Is Microsoft 365 HIPAA Compliant? PHI Setup Checklist
Yes, Microsoft 365 can support a HIPAA-aligned medical practice when the right agreement and settings are in place. This guide shows how to confirm Microsoft's Business Associate Agreement (BAA), what to configure in each app, and what to heck before patient records move.
Yes, Microsoft 365 can support a HIPAA-aligned medical practice when the right agreement and settings are in place. This guide shows how to confirm Microsoft's Business Associate Agreement (BAA), what to configure in each app, and what to heck before patient records move.
Read full post on kairosit.com
How to Evaluate IT Support Vendor Security Capabilities for Regulatory Compliance
When you sign a multi-year contract with an IT support vendor, you’re not just buying helpdesk tickets and network monitoring. You’re handing them administrative access to your financial data, customer records, regulated workloads, and business continuity infrastructure. If that vendor suffers a breach or fails an audit, your organization owns the regulatory consequences. Yet most... <p>
When you sign a multi-year contract with an IT support vendor, you’re not just buying helpdesk tickets and network monitoring. You’re handing them administrative access to your financial data, customer records, regulated workloads, and business continuity infrastructure. If that vendor suffers a breach or fails an audit, your organization owns the regulatory consequences. Yet most... <p>
Read full post on xitx.com
SOC 2 vs ISO 27001 for small businesses: How to Compare
SOC 2 vs ISO 27001 for small businesses: compare outcomes, scope, evidence, and upkeep, then choose an assurance path that fits customer needs.
SOC 2 vs ISO 27001 for small businesses: compare outcomes, scope, evidence, and upkeep, then choose an assurance path that fits customer needs.
Read full post on igtech365.com
CMMC Compliance IT Support: What Manufacturers Actually Need From a Provider
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2:first-child,.blog-post-container>h3:first-child{margin-top:0 !important;}.blog-post-container p{margin-bottom:1.25em !important;}.blog-post-container ul,.blog-post-container ol{margin:0 0 1.6em 1.4em !important;padding:0 !important;}.blog-post-container li{margin-bottom:0.55em !important;}.blog-post-container blockquote{margin:1.8em 0 !important;padding:1.2em 1.6em !important;border-left:4px solid #ccc !important;background:#222222 !important;}.blog-post-container .table-of-contents{background:#1a1f2e !important;border:1px solid #2a3040;padding:1.2em 1.5em;border-radius:8px;margin:1.5em 0;}.blog-post-container .table-of-contents h4{margin-top:0 !important;margin-bottom:0.8em !important;color:#e0e0e0 !important;font-size:1.1em;}.blog-post-container .table-of-contents ul{margin:0 !important;padding-left:1.2em !important;}.blog-post-container .table-of-contents li{margin-bottom:0.4em !important;}.blog-post-container .table-of-contents a{text-decoration:none;color:#60a5fa !important;transition:color 0.2s ease;}.blog-post-container .table-of-contents a:hover{color:#93c5fd !important;text-decoration:underline;}.blog-post-container .key-takeaways{background:#1a2b3c !important;border-left:4px solid #2563eb !important;padding:1.25em 1.5em;margin:1.5em 0;border-radius:0 8px 8px 0;}.blog-post-container .key-takeaways h4{margin-top:0 !important;margin-bottom:0.75em !important;color:#60a5fa !important;font-weight:700;}.blog-post-container .key-takeaways ul{margin-bottom:0 !important;}.blog-post-container .key-takeaways li{margin-bottom:0.6em !important;}.blog-post-container .eyebrow-label{text-transform:uppercase;letter-spacing:1px;color:#888;font-size:0.8em;margin-bottom:8px;font-weight:500;}.blog-post-container .callout,.blog-post-container .quick-answer,.blog-post-container .highlight-box{padding:20px 20px 20px 50px !important;margin:2em 0 !important;border-left:5px solid;border-radius:5px !important;position:relative;}.blog-post-container .callout-tip,.blog-post-container .quick-answer{display:block !important;position:relative !important;padding:16px 20px 16px 56px !important;margin:1.5em 0 !important;border-left:5px solid #2e77b5 !important;background:#1a2b3c !important;border-radius:6px !important;line-height:1.6 !important;}.blog-post-container .callout-info,.blog-post-container .highlight-box{border-color:#3498db !important;background:#1c3040 !important;}.blog-post-container .callout-warning{border-color:#c03e26 !important;background:#3d1e1a !important;}.blog-post-container .pros-cons-list{display:grid !important;grid-template-columns:1fr 1fr !important;gap:20px !important;margin:2em 0 !important;padding:0 !important;}.blog-post-container .pros-cons-list>h2,.blog-post-container .pros-cons-list>h3,.blog-post-container .pros-cons-list>h4{grid-column:1 / -1 !important;margin-top:0 !important;}.blog-post-container .pros-list{background:#1a3b2a !important;border:1px solid #c6f6d5 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .pros-list h4{color:#86efac !important;}.blog-post-container .cons-list{background:#3f1f1f !important;border:1px solid #fed7d7 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .cons-list h4{color:#fca5a5 !important;}.blog-post-container .cta-button{display:inline-block;background:#5fc5bd;color:#FFFFFF !important;font-size:18px;font-weight:700;line-height:1;padding:14px 32px;border-radius:32px;letter-spacing:0.5px;text-decoration:none;border:none;outline:none;transition:background-color 0.2s ease-in-out;}.blog-post-container .cta-button:hover{background:#4aa8a1;}.blog-post-container .author-bio-wrapper .author-bio{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container .author-bio-wrapper section{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container table{width:100% !important;max-width:100% !important;table-layout:fixed !important;border-collapse:collapse !important;font-size:0.75em;}.blog-post-container th,.blog-post-container td{padding:0.6em 0.8em !important;white-space:normal !important;word-break:normal !important;overflow-wrap:break-word !important;}@media (max-width:749px){.blog-post-container .pros-cons-list{grid-template-columns:1fr !important;}}@media (max-width:900px){.blog-post-container table{display:block;overflow-x:auto;font-size:0.65em;}} cmmc compliance it support
Read full post on andromeda.tech
Private AI Document Processing for Small Business: Extract Invoice Data Without Third-Party Risk
Small businesses process hundreds of invoices monthly. Most still use humans to type vendor names, amounts, and dates into accounting systems. The AI hype machine promises instant automation, but every mainstream tool sends your financial documents to someone else’s server. That’s a non-starter if you care about confidentiality, client trust, or regulatory exposure. Private AI... <p>
Small businesses process hundreds of invoices monthly. Most still use humans to type vendor names, amounts, and dates into accounting systems. The AI hype machine promises instant automation, but every mainstream tool sends your financial documents to someone else’s server. That’s a non-starter if you care about confidentiality, client trust, or regulatory exposure. Private AI... <p>
Read full post on xitx.com
CMMC Compliance Checklist for Manufacturers: A Practical, Phased Path from Scoping to SPRS
Popular MSPs
View All
Stay Updated
Get the latest it compliance advice for growing companies delivered to your inbox.