Cybersecurity
Latest cybersecurity news, ransomware alerts, and threat intelligence for growing companies.
MSPdb™ News
EDR Versus Antivirus Software for Businesses
EDR versus antivirus software affects how quickly your business can detect, contain, and recover from cyber threats. Learn which protection fits best.
EDR versus antivirus software affects how quickly your business can detect, contain, and recover from cyber threats. Learn which protection fits best.
Read full post on priscanova.com
Microsoft is preparing for a cyberthreat that hasn’t happened yet
Post-quantum security sounds technical, but it comes down to preparing early for a change that may be years away. Here's what Microsoft's move means for a business like yours.
Post-quantum security sounds technical, but it comes down to preparing early for a change that may be years away. Here's what Microsoft's move means for a business like yours.
Read full post on skysailtechnologies.com
How Managed IT Providers Protect Businesses From Ransomware
Ransomware has become one of the most damaging cybersecurity threats facing businesses today. A single successful attack can lock critical files, interrupt operations, expose sensitive data, and create significant financial losses. Many organizations assume ransomware only affects large enterprises. However, small and medium-sized businesses are increasingly targeted because attackers often identify them as easier targets
Ransomware has become one of the most damaging cybersecurity threats facing businesses today. A single successful attack can lock critical files, interrupt operations, expose sensitive data, and create significant financial losses. Many organizations assume ransomware only affects large enterprises. However, small and medium-sized businesses are increasingly targeted because attackers often identify them as easier targets
Read full post on desertitsolutions.com
NAS Ransomware Attacks: Why Backup Devices Are the Primary Target
Network-attached storage devices have become the single most valuable target in modern ransomware campaigns. When threat actors compromise your backup repository directly, they eliminate your primary recovery path before encrypting production systems. This attack pattern represents a fundamental shift in ransomware tactics—what security professionals have been warning about since 2021 is now the dominant method.... <p>
Network-attached storage devices have become the single most valuable target in modern ransomware campaigns. When threat actors compromise your backup repository directly, they eliminate your primary recovery path before encrypting production systems. This attack pattern represents a fundamental shift in ransomware tactics—what security professionals have been warning about since 2021 is now the dominant method.... <p>
Read full post on xitx.com
Incident Response: A Practical Guide for Small Businesses
Learn how to recognize, contain, and recover from a business security incident with clear roles, practical steps, and a plan for communicating well.
Learn how to recognize, contain, and recover from a business security incident with clear roles, practical steps, and a plan for communicating well.
Read full post on igtech365.com
Create a Practical Guide for IAM
IAM helps businesses control who can access systems and data. Learn how to assess needs, set access rules, and improve identity management step by step.
IAM helps businesses control who can access systems and data. Learn how to assess needs, set access rules, and improve identity management step by step.
Read full post on igtech365.com
Ransomware Protection San Diego: Test Your Backup Restore Before You Need It
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Read full post on fitsolutions.biz
Incident Response Retainer Questions: 7 Critical Asks Before You Need It
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Read full post on xitx.com
From Vulnerability Scanning to CTEM
From Vulnerability Scanning to CTEM: Proactive Cybersecurity in Action As cyber threats continue to evolve, organizations face a critical challenge: understanding not just where vulnerabilities exist, but how those vulnerabilities translate into real business risk.
From Vulnerability Scanning to CTEM: Proactive Cybersecurity in Action As cyber threats continue to evolve, organizations face a critical challenge: understanding not just where vulnerabilities exist, but how those vulnerabilities translate into real business risk.
Read full post on oxen.tech
MDR Cost in Houston: Per-Endpoint Pricing in 2026
MDR in Houston costs about $10 to $25 per endpoint per month in 2026, our ... Learn More
MDR in Houston costs about $10 to $25 per endpoint per month in 2026, our ... Learn More
Read full post on uprite.com
An Employee Entered Their Password on a Phishing Site: What Chicago Businesses Should Do Right Now
An employee typed a password into a phishing page. Here is what to do in the first hour, what to check next, who to tell, and how CTI Technology helps Chicago-area businesses.
An employee typed a password into a phishing page. Here is what to do in the first hour, what to check next, who to tell, and how CTI Technology helps Chicago-area businesses.
Read full post on ctinc.com

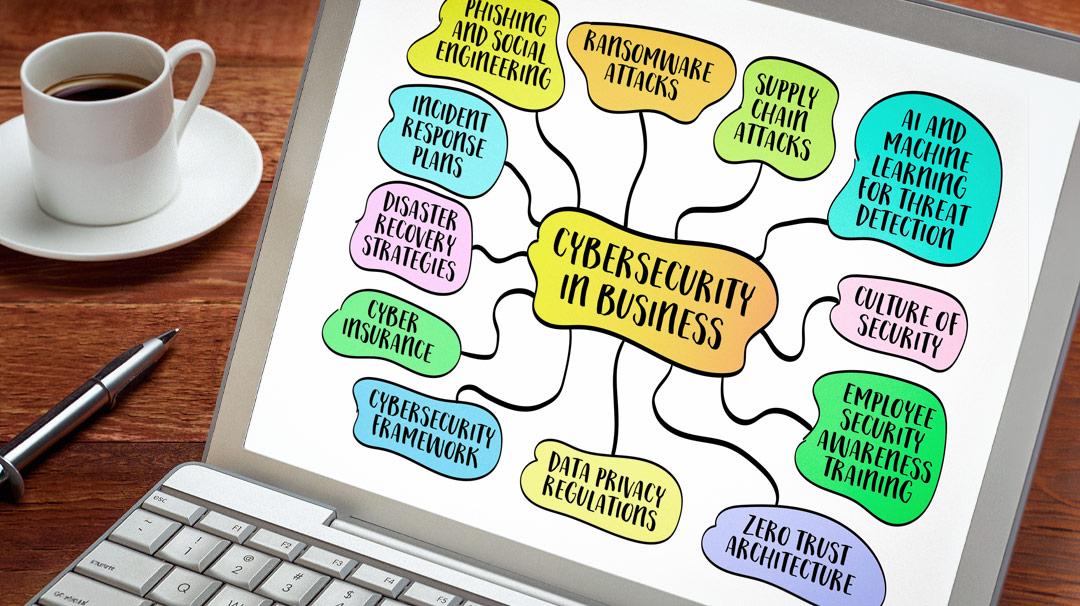
Cybersecurity Isn’t an IT Problem. It’s a Business Problem.
Most cyberattacks begin as the result of a seemingly benign action. Someone clicks a link in an email. An employee reuses a password. A customer sends sensitive information to the wrong person. Someone gives a colleague access to a file they don’t actually need. None of these actions seem especially dangerous in the moment, but
Most cyberattacks begin as the result of a seemingly benign action. Someone clicks a link in an email. An employee reuses a password. A customer sends sensitive information to the wrong person. Someone gives a colleague access to a file they don’t actually need. None of these actions seem especially dangerous in the moment, but
Read full post on infinitelyvirtual.com
Infostealer Malware: How Stolen Browser Credentials Can Expose a Business
What Is Infostealer Malware and How Does It Work? Infostealer malware is malicious software that steals sensitive information from an infected device, including saved passwords, browser cookies, and authentication tokens. Attackers may use or sell that information to access business accounts. Some stolen sessions can be reused without a fresh login, depending on the service’s
What Is Infostealer Malware and How Does It Work? Infostealer malware is malicious software that steals sensitive information from an infected device, including saved passwords, browser cookies, and authentication tokens. Attackers may use or sell that information to access business accounts. Some stolen sessions can be reused without a fresh login, depending on the service’s
Read full post on bestructured.com
Stress-test your incident response plan with a tabletop exercise and no downtime
For small and medium-sized businesses (SMBs), knowing who makes key decisions during a cyberattack is essential. A cybersecurity tabletop exercise helps teams identify responsibilities, test response procedures, and clarify escalation paths before an actual breach occurs. Through guided discussions rather than live system testing, businesses can improve their incident readiness without disrupting daily operations. Why
For small and medium-sized businesses (SMBs), knowing who makes key decisions during a cyberattack is essential. A cybersecurity tabletop exercise helps teams identify responsibilities, test response procedures, and clarify escalation paths before an actual breach occurs. Through guided discussions rather than live system testing, businesses can improve their incident readiness without disrupting daily operations. Why
Read full post on advancedtechinc.com
Create a practical guide for incident response services
Learn what incident response services do, what to expect during a security incident, and how to evaluate a provider before your business needs one.
Learn what incident response services do, what to expect during a security incident, and how to evaluate a provider before your business needs one.
Read full post on igtech365.com
5 Best Cybersecurity Companies in Aurora, Ontario (2026)
Five cybersecurity providers serving Aurora, compared on security integration, verified reviews, service depth, and Aurora proximity.
Five cybersecurity providers serving Aurora, compared on security integration, verified reviews, service depth, and Aurora proximity.
Read full post on act360.ca
Cybersecurity Month Is Over. The Work Isn’t.
Cybersecurity Awareness Month may have ended, but cyber threats certainly didn’t. And today, one thing is making the security landscape move even faster: AI. AI hasn’t completely changed how cyberattacks work. In many cases, attackers are still using the same tactics they always have: phishing, stolen passwords, fake login pages, deploying ransomware, and exploiting systems that haven’t been properly secured. What AI is changing is the speed and scale at which those attacks can happen. Attackers can use AI to create more convincing phishing emails, rapidly customize mes
Cybersecurity Awareness Month may have ended, but cyber threats certainly didn’t. And today, one thing is making the security landscape move even faster: AI. AI hasn’t completely changed how cyberattacks work. In many cases, attackers are still using the same tactics they always have: phishing, stolen passwords, fake login pages, deploying ransomware, and exploiting systems that haven’t been properly secured. What AI is changing is the speed and scale at which those attacks can happen. Attackers can use AI to create more convincing phishing emails, rapidly customize messages, impersonate people and organizations, and automate parts of an attack that once required more time and effort. The reality is that businesses need to take cybersecurity more seriously than ever. AI is giving attackers the ability to move faster, create more convincing attacks and operate at a greater scale. Those threats are going to continue to evolve and become harder to recognize and stop. That doesn’t mean businesses need to panic. It means they need to collaborate with their IT and cybersecurity providers, take recommendations seriously, and follow through on the protections being recommended. Here are five areas every business should be working on with their IT provider today: 5 things to work on with your IT provider 1. Make sure MFA is protecting more than just email Multi-factor authentication should be enabled anywhere a compromised password could provide meaningful access to your business. That includes Microsoft 365, remote access tools, administrative accounts and, importantly, your company VPN. 2. Review who has administrator access Employees shouldn’t routinely work from accounts that have administrator privileges. Your IT provider should regularly review who has elevated access and remove permissions that are no longer necessary. 3. Keep computers, servers, firewalls and software patched Attackers actively look for known vulnerabilities. Make sure operating systems, applications, firewalls and other critical infrastructure are being routinely updated, not just when something breaks. 4. Prepare your employees for better phishing attacks AI makes it easier to create emails that look polished, personal and legitimate. Security awareness training and phishing simulations are increasingly important because employees need to recognize more than just obvious spelling mistakes and suspicious-looking emails. 5. Make sure your backups are actually recoverable and tested Having a backup isn’t the same as having a recovery plan. Ask your IT provider where your backups are stored, how they’re protected from ransomware, how often they’re tested, and how long it would realistically take to restore your business after an incident. Cybersecurity doesn’t need to be complicated The headlines around AI and cybersecurity can make the problem feel overwhelming. It doesn’t have to be. Good cybersecurity still starts with doing the basics extremely well: protect identities, limit access, patch systems, educate people and maintain recoverable backups. Cybersecurity Awareness Month may be over. The work shouldn’t be. Contact Us today to start the conversation.
Read full post on ceeva.com
RDP Ransomware Attacks: Why Perimeter Access Logs Are the First Target
RDP ransomware attacks keep climbing, and the reason has nothing to do with sophisticated exploits. Most small and mid-sized businesses don’t monitor or review their perimeter access logs. For attackers, those logs are a roadmap. They show which remote desktop protocol endpoints are exposed, which credentials are being tested, and where monitoring gaps exist. When... <p>
RDP ransomware attacks keep climbing, and the reason has nothing to do with sophisticated exploits. Most small and mid-sized businesses don’t monitor or review their perimeter access logs. For attackers, those logs are a roadmap. They show which remote desktop protocol endpoints are exposed, which credentials are being tested, and where monitoring gaps exist. When... <p>
Read full post on xitx.com
What Is Managed Detection and Response (MDR) and Do You Need It?
Most small businesses have some kind of security software. Far fewer have anyone watching what it reports at 2 a.m. on a Sunday. That gap, between a tool that raises an alert and a person who acts on it, is exactly what managed detection and response is designed to close. This guide explains what MDR
Most small businesses have some kind of security software. Far fewer have anyone watching what it reports at 2 a.m. on a Sunday. That gap, between a tool that raises an alert and a person who acts on it, is exactly what managed detection and response is designed to close. This guide explains what MDR
Read full post on irongatemsp.com
SOC 2 vs ISO 27001 for small businesses: How to Compare
SOC 2 vs ISO 27001 for small businesses: compare outcomes, scope, evidence, and upkeep, then choose an assurance path that fits customer needs.
SOC 2 vs ISO 27001 for small businesses: compare outcomes, scope, evidence, and upkeep, then choose an assurance path that fits customer needs.
Read full post on igtech365.com
Stress-test your incident response plan with a tabletop exercise and no downtime
For small and medium-sized businesses (SMBs), knowing who makes key decisions during a cyberattack is essential. A cybersecurity tabletop exercise helps teams identify responsibilities, test response procedures, and clarify escalation
For small and medium-sized businesses (SMBs), knowing who makes key decisions during a cyberattack is essential. A cybersecurity tabletop exercise helps teams identify responsibilities, test response procedures, and clarify escalation
Read full post on orchestratetech.com
Stress-test your incident response plan with a tabletop exercise and no downtime
For small and medium-sized businesses (SMBs), knowing who makes key decisions during a cyberattack is essential. A cybersecurity tabletop exercise helps teams identify responsibilities, test response procedures, and clarify escalation paths before an actual breach occurs. Through guided discussions rather than live system testing, businesses can improve their incident readiness without disrupting daily operations. Why
For small and medium-sized businesses (SMBs), knowing who makes key decisions during a cyberattack is essential. A cybersecurity tabletop exercise helps teams identify responsibilities, test response procedures, and clarify escalation paths before an actual breach occurs. Through guided discussions rather than live system testing, businesses can improve their incident readiness without disrupting daily operations. Why
Read full post on egistech.com
How to Build a Cyber Incident Response Plan for a Small Business
A small business needs a clear response process before a cyber incident disrupts operations. Build a cyber incident response plan for your small...
A small business needs a clear response process before a cyber incident disrupts operations. Build a cyber incident response plan for your small...
Read full post on reisinformatica.com
The PHP Vulnerability Scare: What It Is and Why It Matters
We’ve all seen the countless headlines over the past couple of weeks about the new PHP vulnerability, and some of us even found that sites we rely on were taken …
We’ve all seen the countless headlines over the past couple of weeks about the new PHP vulnerability, and some of us even found that sites we rely on were taken …
Read full post on mirazon.com
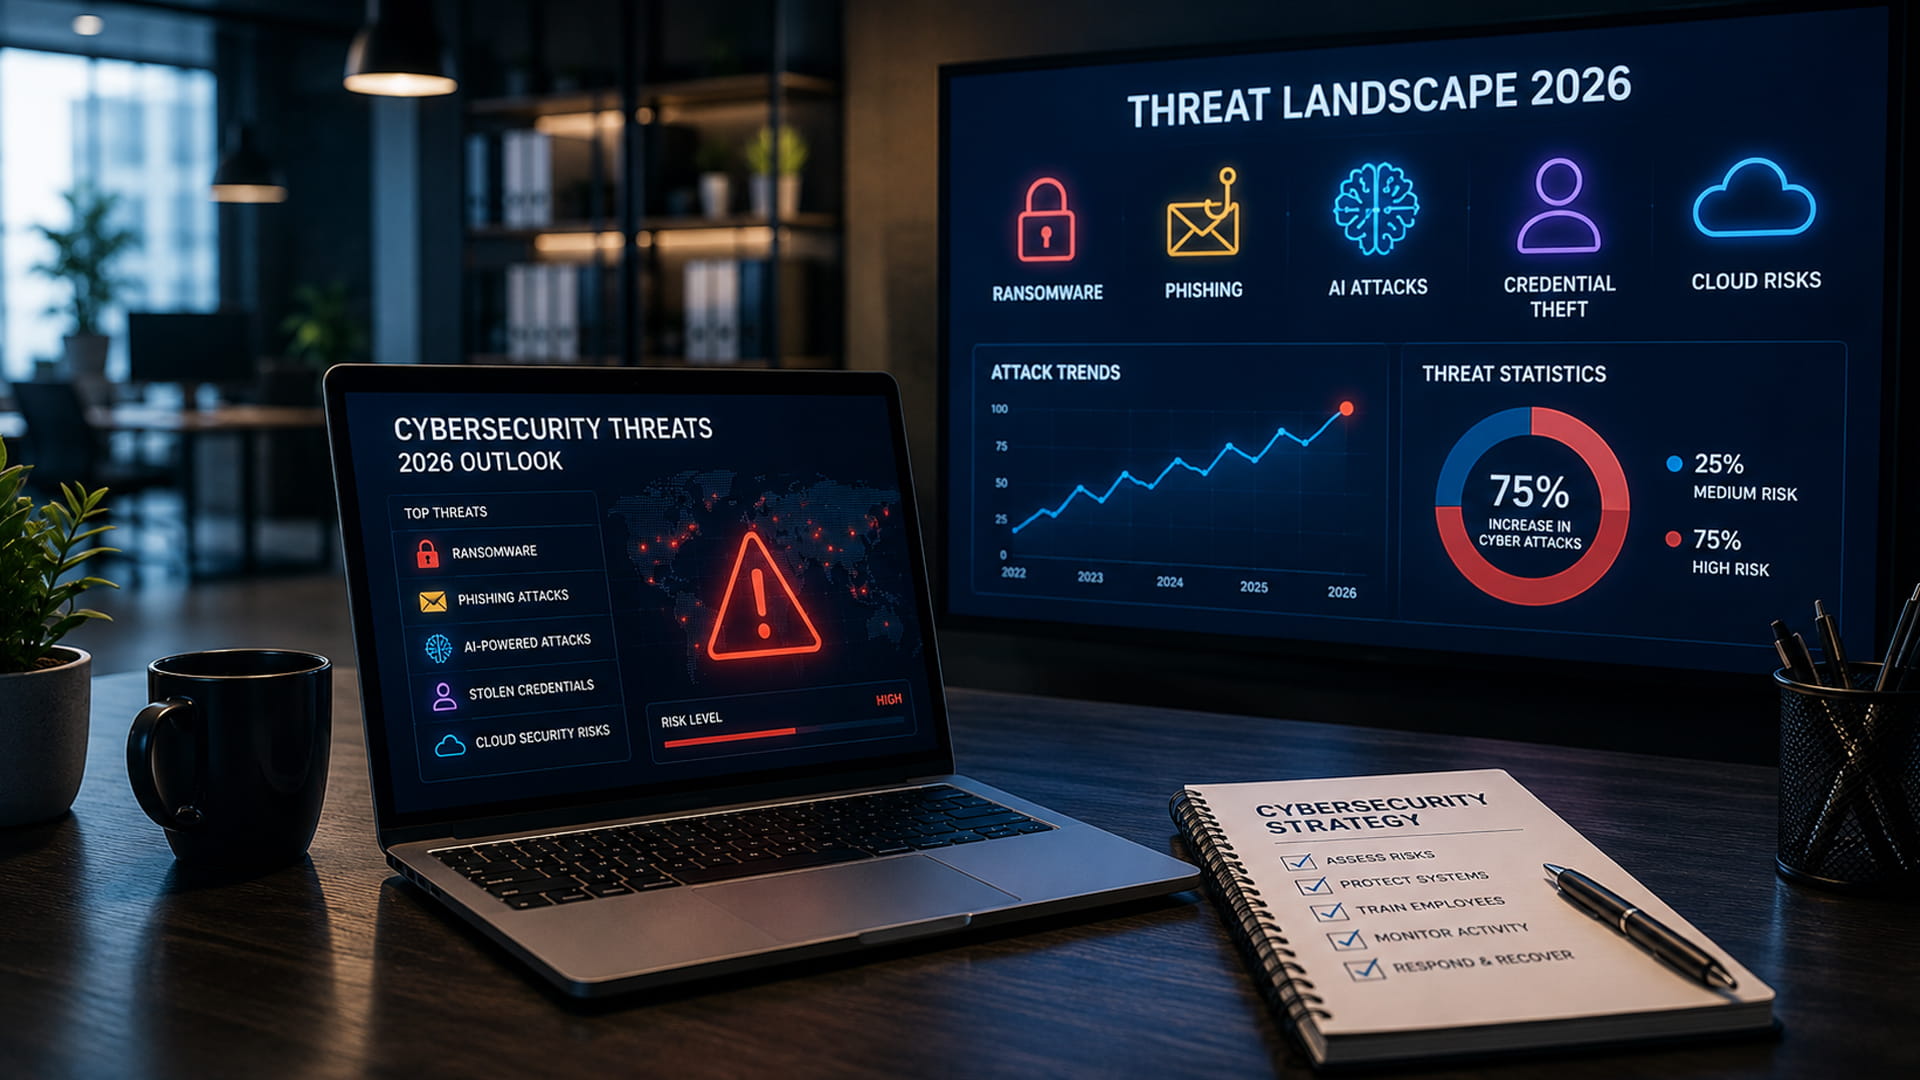
Top Cybersecurity Threats Businesses Should Prepare For in 2026
Cybersecurity threats are becoming more advanced, targeted, and difficult for businesses to manage without proper protection. Organizations of all sizes now face risks from ransomware, phishing, artificial intelligence-powered attacks, data breaches, and compromised accounts. In 2026, businesses cannot rely on basic security tools alone. Attackers are constantly improving their methods, while companies are becoming more
Cybersecurity threats are becoming more advanced, targeted, and difficult for businesses to manage without proper protection. Organizations of all sizes now face risks from ransomware, phishing, artificial intelligence-powered attacks, data breaches, and compromised accounts. In 2026, businesses cannot rely on basic security tools alone. Attackers are constantly improving their methods, while companies are becoming more
Read full post on desertitsolutions.com
Securing Your Remote Staff: Endpoint Protections, MFA Protocols, and VPN Strategies to Protect Your Company’s Data
Quick Answer: Protecting remote employees requires three core layers: endpoint protection to secure devices, multi-factor authentication (MFA) to verify identities, and VPNs to encrypt data in transit. Together, these tools close the gaps that remote work creates, keeping company data safe no matter where your team logs in from. Remote work has changed the way
Quick Answer: Protecting remote employees requires three core layers: endpoint protection to secure devices, multi-factor authentication (MFA) to verify identities, and VPNs to encrypt data in transit. Together, these tools close the gaps that remote work creates, keeping company data safe no matter where your team logs in from. Remote work has changed the way
Read full post on totalit.com
What Is Managed Detection and Response (MDR) and Why Businesses Need It
Introduction Cyber threats are becoming more advanced, and traditional security tools are no longer enough to protect businesses. Many organizations use antivirus software and firewalls,...
Introduction Cyber threats are becoming more advanced, and traditional security tools are no longer enough to protect businesses. Many organizations use antivirus software and firewalls,...
Read full post on themillergroup.com
Why Businesses Need Cybersecurity Protection
Why businesses need cybersecurity: protect operations, data, revenue, and customer trust with practical controls and local accountability when it matters.
Why businesses need cybersecurity: protect operations, data, revenue, and customer trust with practical controls and local accountability when it matters.
Read full post on priscanova.com
Multi-Factor Authentication: What It Is and Why It Stops Most Attacks
If you’ve ever typed your password and then approved a prompt on your phone, you’ve used multi-factor authentication. It’s one of the simplest security measures a business can adopt, and one of the most effective, yet many small businesses still haven’t turned it on everywhere it matters. This guide answers the basic question of what
If you’ve ever typed your password and then approved a prompt on your phone, you’ve used multi-factor authentication. It’s one of the simplest security measures a business can adopt, and one of the most effective, yet many small businesses still haven’t turned it on everywhere it matters. This guide answers the basic question of what
Read full post on irongatemsp.com
Cybersecurity Services San Diego: Build an Incident Response Plan Your Insurer Will Actually Accept
Cybersecurity services San Diego businesses can rely on after an incident: response plan, MFA, backups, and proof insurers require to pay.
Cybersecurity services San Diego businesses can rely on after an incident: response plan, MFA, backups, and proof insurers require to pay.
Read full post on fitsolutions.biz
Failed to load more articles
You're all caught up!
Check back later for more cybersecurity news.
MSPdb™ News
EDR Versus Antivirus Software for Businesses
EDR versus antivirus software affects how quickly your business can detect, contain, and recover from cyber threats. Learn which protection fits best.
EDR versus antivirus software affects how quickly your business can detect, contain, and recover from cyber threats. Learn which protection fits best.
Read full post on priscanova.com
Microsoft is preparing for a cyberthreat that hasn’t happened yet
Post-quantum security sounds technical, but it comes down to preparing early for a change that may be years away. Here's what Microsoft's move means for a business like yours.
Post-quantum security sounds technical, but it comes down to preparing early for a change that may be years away. Here's what Microsoft's move means for a business like yours.
Read full post on skysailtechnologies.com
How Managed IT Providers Protect Businesses From Ransomware
Ransomware has become one of the most damaging cybersecurity threats facing businesses today. A single successful attack can lock critical files, interrupt operations, expose sensitive data, and create significant financial losses. Many organizations assume ransomware only affects large enterprises. However, small and medium-sized businesses are increasingly targeted because attackers often identify them as easier targets
Ransomware has become one of the most damaging cybersecurity threats facing businesses today. A single successful attack can lock critical files, interrupt operations, expose sensitive data, and create significant financial losses. Many organizations assume ransomware only affects large enterprises. However, small and medium-sized businesses are increasingly targeted because attackers often identify them as easier targets
Read full post on desertitsolutions.com
NAS Ransomware Attacks: Why Backup Devices Are the Primary Target
Network-attached storage devices have become the single most valuable target in modern ransomware campaigns. When threat actors compromise your backup repository directly, they eliminate your primary recovery path before encrypting production systems. This attack pattern represents a fundamental shift in ransomware tactics—what security professionals have been warning about since 2021 is now the dominant method.... <p>
Network-attached storage devices have become the single most valuable target in modern ransomware campaigns. When threat actors compromise your backup repository directly, they eliminate your primary recovery path before encrypting production systems. This attack pattern represents a fundamental shift in ransomware tactics—what security professionals have been warning about since 2021 is now the dominant method.... <p>
Read full post on xitx.com
Incident Response: A Practical Guide for Small Businesses
Learn how to recognize, contain, and recover from a business security incident with clear roles, practical steps, and a plan for communicating well.
Learn how to recognize, contain, and recover from a business security incident with clear roles, practical steps, and a plan for communicating well.
Read full post on igtech365.com
Create a Practical Guide for IAM
IAM helps businesses control who can access systems and data. Learn how to assess needs, set access rules, and improve identity management step by step.
IAM helps businesses control who can access systems and data. Learn how to assess needs, set access rules, and improve identity management step by step.
Read full post on igtech365.com
Ransomware Protection San Diego: Test Your Backup Restore Before You Need It
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Read full post on fitsolutions.biz
Incident Response Retainer Questions: 7 Critical Asks Before You Need It
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Read full post on xitx.com
From Vulnerability Scanning to CTEM
From Vulnerability Scanning to CTEM: Proactive Cybersecurity in Action As cyber threats continue to evolve, organizations face a critical challenge: understanding not just where vulnerabilities exist, but how those vulnerabilities translate into real business risk.
From Vulnerability Scanning to CTEM: Proactive Cybersecurity in Action As cyber threats continue to evolve, organizations face a critical challenge: understanding not just where vulnerabilities exist, but how those vulnerabilities translate into real business risk.
Read full post on oxen.tech
MDR Cost in Houston: Per-Endpoint Pricing in 2026
MDR in Houston costs about $10 to $25 per endpoint per month in 2026, our ... Learn More
MDR in Houston costs about $10 to $25 per endpoint per month in 2026, our ... Learn More
Read full post on uprite.com
Popular MSPs
View All
Stay Updated
Get the latest cybersecurity advice for growing companies delivered to your inbox.