IT's all about results.
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
Bell Techlogix Named to CRN’s MSP 500 List in Elite 150 Category for 2026
Contact: Katie McCarthy Bell Techlogix kmccarthy@belltechlogix.com Bell Techlogix Named to CRN’s MSP 500 List in Elite 150 Category for 2026 Indianapolis, IN, March 9, 2026 — Bell Techlogix, an Indianapolis-based
Contact: Katie McCarthy Bell Techlogix kmccarthy@belltechlogix.com Bell Techlogix Named to CRN’s MSP 500 List in Elite 150 Category for 2026 Indianapolis, IN, March 9, 2026 — Bell Techlogix, an Indianapolis-based
Read full post on belltechlogix.comMSPdb™ News
The IT Setup Every Cameron Park Financial Office Needs Before Tax Season
For financial offices in Cameron Park, tax season is the busiest and most profitable stretch of the year. It’s also when technology problems cost the most. A slow computer, a tax software install that fails, or one phishing email opened at the wrong moment can put a full day of client work on hold when
For financial offices in Cameron Park, tax season is the busiest and most profitable stretch of the year. It’s also when technology problems cost the most. A slow computer, a tax software install that fails, or one phishing email opened at the wrong moment can put a full day of client work on hold when
Read full post on rj-pro.net
Top 10 Cybersecurity Threats Facing Texas Businesses
Cybersecurity threats are becoming an increasingly important concern for businesses across Texas. As companies rely more on cloud applications, connected networks, remote access, digital payments, email, and online systems, cybercriminals have more opportunities to target business data and infrastructure. From Houston to Dallas, Austin, San Antonio, and other Texas communities, organizations need a practical approach
Cybersecurity threats are becoming an increasingly important concern for businesses across Texas. As companies rely more on cloud applications, connected networks, remote access, digital payments, email, and online systems, cybercriminals have more opportunities to target business data and infrastructure. From Houston to Dallas, Austin, San Antonio, and other Texas communities, organizations need a practical approach
Read full post on cobait.com
Best Managed IT Services Columbus: Eliminating IT Drag in Industrial Operations
The Five Security Controls Insurance Carriers Now Expect to See
The Five Security Controls Insurance Carriers Now Expect to See For years, obtaining cyber insurance was often a straightforward process. Organizations completed an application, answered basic questions about their technology environment, and received coverage. Today, that process looks very different. Cyber insurance providers have experienced substantial losses from ransomware attacks, business email compromise, data breaches, and operational disruptions. In response, insurers have transformed underwriting practices to focus more heavily on cybersecurity maturity, risk management, and de
The Five Security Controls Insurance Carriers Now Expect to See For years, obtaining cyber insurance was often a straightforward process. Organizations completed an application, answered basic questions about their technology environment, and received coverage. Today, that process looks very different. Cyber insurance providers have experienced substantial losses from ransomware attacks, business email compromise, data breaches, and operational disruptions. In response, insurers have transformed underwriting practices to focus more heavily on cybersecurity maturity, risk management, and demonstrable security controls. Executives are increasingly discovering that cyber insurance eligibility is no longer determined solely by company size, industry, or claims history. It is determined by an organization's ability to demonstrate that key cybersecurity safeguards are in place and actively maintained. For business leaders, understanding these expectations has become an important component of risk management and strategic planning. Cyber Insurance Has Evolved Beyond a Questionnaire Insurance carriers no longer view cybersecurity as a technical issue delegated exclusively to the IT department. Instead, cybersecurity has become a measurable business risk that directly influences insurability, premiums, coverage limits, and claim outcomes. Organizations seeking coverage today may be asked detailed questions regarding: Security policies Identity management Endpoint protection Vulnerability management Employee security awareness Incident response preparedness Backup and disaster recovery capabilities Many insurers also reserve the right to validate responses provided on applications. As a result, organizations must be prepared to demonstrate that stated controls are operating effectively across the business. The following five controls are among the most frequently evaluated during the underwriting process. Control #1: Multi-Factor Authentication (MFA) If there is one security control that has transformed cyber insurance underwriting more than any other, it is Multi-Factor Authentication. Insurance carriers increasingly expect MFA to protect: Email systems Remote access solutions Cloud applications Administrative accounts Financial systems Cybercriminals continue to exploit stolen passwords through phishing attacks, password spraying, credential stuffing, and social engineering. MFA significantly reduces the likelihood that a compromised password alone can lead to unauthorized access. From an underwriting perspective, MFA represents a strong indicator that an organization takes identity protection seriously. Executives should ask: Is MFA enabled across all critical systems? Are privileged accounts protected? Are exceptions documented and minimized? Organizations unable to answer these questions may face increased scrutiny during insurance reviews. Control #2: Endpoint Protection and Monitoring Traditional antivirus solutions are no longer considered sufficient against modern threats. Insurers increasingly want confidence that organizations can: Detect suspicious activity Respond quickly to threats Prevent malware execution Protect remote and hybrid workers Modern endpoint security solutions provide visibility into device activity, helping organizations identify and contain threats before they spread across the environment. This control has become particularly important as organizations continue to support remote work and cloud-based operations. Executives should view endpoint protection as both a security investment and a business continuity investment. Control #3: Vulnerability Management One of the most common concerns among insurers is whether organizations consistently identify and address vulnerabilities. Threat actors routinely exploit known weaknesses that organizations failed to patch or remediate. A mature vulnerability management program helps organizations: Identify security gaps Prioritize remediation efforts Reduce attack surfaces Demonstrate proactive risk management Insurers want evidence that organizations regularly evaluate their environments and address discovered risks. The presence of vulnerabilities does not automatically create underwriting concerns. The absence of a process to manage vulnerabilities often does. Control #4: Security Awareness Training Technology alone cannot defend an organization from every threat. Employees remain one of the most common entry points for cyber incidents. Phishing attacks, fraudulent invoices, credential theft, and social engineering campaigns continue to target employees at every level of the organization. Insurers increasingly expect organizations to provide ongoing security awareness education that helps employees: Recognize phishing attempts Report suspicious activity Follow security policies Protect sensitive information For executives, security awareness should not be viewed as a compliance exercise. It is a measurable risk-reduction strategy that helps protect the entire organization. Organizations that invest in employee education often reduce both cybersecurity risk and insurance-related concerns. Control #5: Incident Response Preparedness One of the first questions organizations ask during a cyber incident is: "What do we do now?" Organizations that have already answered that question often recover faster and experience less disruption. An incident response plan helps define: Roles and responsibilities Escalation procedures Communication protocols Recovery activities Decision-making authority Insurers increasingly view incident response planning as evidence of organizational preparedness. An organization may still experience a security incident despite strong controls. What often matters most is how effectively it responds once an incident occurs. Prepared organizations generally demonstrate greater resilience and reduced business impact. Why These Controls Matter to Executive Leadership These five controls are not simply technology initiatives. They represent business safeguards that influence: Financial stability Insurance eligibility Customer confidence Operational resilience Regulatory exposure Strategic risk management Cyber insurers have become increasingly sophisticated in evaluating cybersecurity risk. Executive teams that proactively understand insurer expectations are better positioned to make informed investments and strengthen organizational resilience. Learn What Insurers Are Looking for Today Understanding insurance requirements before your next renewal or claim can help your organization avoid surprises and strengthen its position. Join OXEN Technology and The Agency Insurance for an executive webinar designed to help business leaders understand the evolving relationship between cyber insurance and cybersecurity. Attendees will learn what insurers expect, how organizations can improve cyber insurance readiness, and what steps leaders should prioritize moving forward. Register Today The organizations that are most successful with cyber insurance are often the ones that prepare long before an application is submitted. Reserve your seat and gain insight into the security controls, governance practices, and risk management strategies that matter most to insurers today.
Read full post on oxen.tech
Reduce Three Week Dwell with Endpoint Detection and Response for SMBs
Operations first EDR playbook for SMB security teams. Tune agents, map NIST and MITRE standards, set 90 day retention, and use tekRESCUE practitioner...
Operations first EDR playbook for SMB security teams. Tune agents, map NIST and MITRE standards, set 90 day retention, and use tekRESCUE practitioner...
Read full post on mytekrescue.com
How to Budget IT Costs Without Costly Surprises
Learn how to budget IT costs with a practical plan for support, security, hardware, cloud services, and business continuity without unwelcome surprises.
Learn how to budget IT costs with a practical plan for support, security, hardware, cloud services, and business continuity without unwelcome surprises.
Read full post on priscanova.com

Co-Managed IT: How It Works and When It's Worth It
Co-managed IT pairs your in-house IT team with an MSP for 24/7 coverage, security, and overflow help. See how it works, what it costs, and when to skip it.
Co-managed IT pairs your in-house IT team with an MSP for 24/7 coverage, security, and overflow help. See how it works, what it costs, and when to skip it.
Read full post on nsocit.com
How Businesses in Jackson Can Build a More Secure and Reliable IT Environment
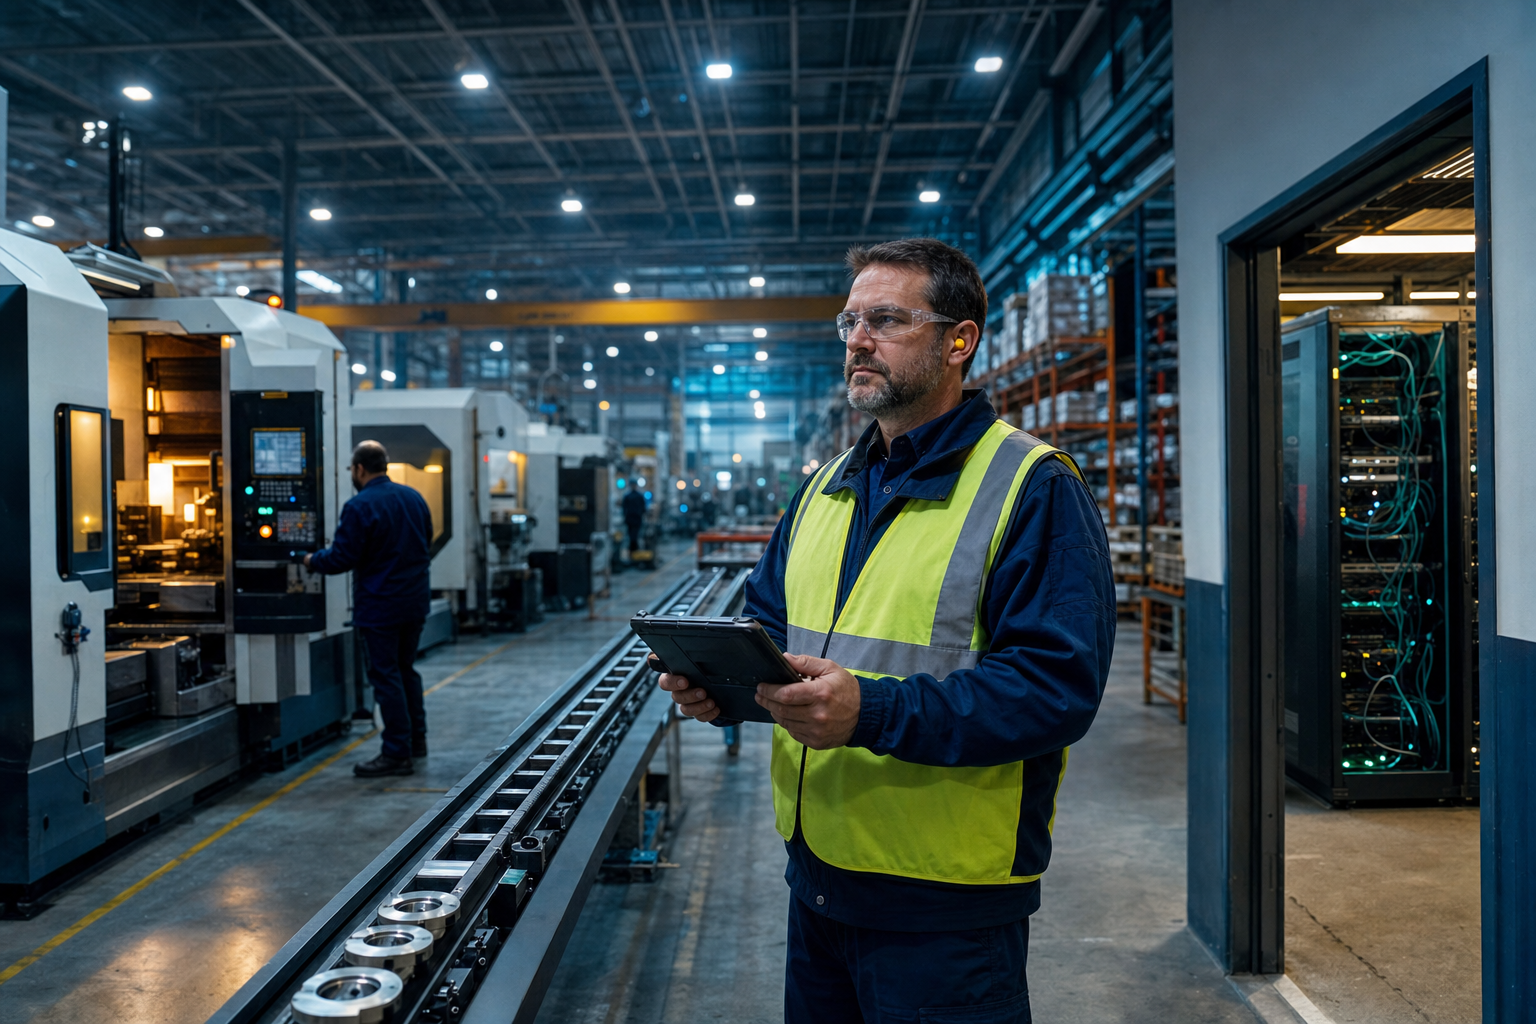
Managed IT Services Cleveland Ohio: The Manufacturer's Guide to Eliminating IT Drag™ and Downtime

On-Premise to Cloud Migration Checklist: 10 Steps
Use this on-premise to cloud migration checklist to plan assessment, compliance, backups, sequencing, testing, cutover, and optimization for SMBs.
Use this on-premise to cloud migration checklist to plan assessment, compliance, backups, sequencing, testing, cutover, and optimization for SMBs.
Read full post on cloudorbis.com
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All