Don't stress, we got IT.
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
When Trusted Technology Becomes a Security Risk
We use the internet every day without giving much thought to what keeps our communications secure. We visit websites, sign into business applications, exchange sensitive data, and trust the lock icon in our browsers. Behind these everyday actions is an interconnected system of software, encryption, digital certificates, and trust. Recent security events involving critical PHP vulnerabilities and a certificate authority incident involving eMudhra serve as timely reminders of what can happen when weaknesses emerge within these foundational technologies. The incidents are unrelated, but the
We use the internet every day without giving much thought to what keeps our communications secure. We visit websites, sign into business applications, exchange sensitive data, and trust the lock icon in our browsers. Behind these everyday actions is an interconnected system of software, encryption, digital certificates, and trust. Recent security events involving critical PHP vulnerabilities and a certificate authority incident involving eMudhra serve as timely reminders of what can happen when weaknesses emerge within these foundational technologies. The incidents are unrelated, but they reinforce the same message: Cybersecurity isn’t only about stopping an attacker from getting in. It’s about continuously understanding, monitoring, and protecting the layers of technology your organization depends on. PHP2Shell: A Threat to Web Infrastructure On October 21, emergency patches were issued for two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both carrying a CVSS 4.0 score of 9.2. The vulnerabilities can enable unauthenticated remote code execution, potentially allowing an attacker to execute commands on a vulnerable web server without first authenticating. The risk is particularly significant because the vulnerabilities exist at the PHP runtime level. Potentially affected environments include PHP installations handling web requests through PHP-FPM, Apache mod_php, php-cgi, FrankenPHP, and LiteSpeed. Patched releases include PHP 8.2.35, 8.3.36, 8.4.27, and 8.5.12. Organizations running PHP 8.1 or earlier warrant additional attention because those branches are no longer receiving normal upstream security releases. For businesses, however, the challenge goes beyond knowing a patch exists. The bigger question is whether you know where PHP exists in your environment. PHP may be supporting an e-commerce site, customer portal, legacy application, container, or appliance without being immediately visible to the teams responsible for security. That makes accurate asset inventory and continuous vulnerability management just as important as the patch itself. When the Technology That Creates Trust Becomes the Threat A separate security incident involving certificate authority eMudhra highlights another type of foundational risk. TLS certificates help establish encrypted connections and verify that users are connecting to the intended service. Certificate authorities sit at the center of that trust model. Private keys associated with eight eMudhra intermediate certificate authorities were found to have been generated using severely inadequate cryptographic values. Six were associated with TLS certificates and two with code signing. The weakness meant the corresponding private keys could effectively be recovered using information contained in the public certificates, potentially allowing an attacker to generate fraudulent certificates that appeared to have been signed by a trusted certificate authority. The affected certificates were subsequently retracted or distrusted, but the incident highlights a broader challenge. Systems that do not benefit from modern browser-based revocation mechanisms, including some containers, Linux systems, embedded devices, IoT environments, developer tools, and applications using independent trust stores, may require additional remediation. Importantly, there is currently no public indication that the affected eMudhra keys were maliciously exploited. Two Vulnerabilities, One Message At first glance, a PHP vulnerability and a cryptographic weakness involving a certificate authority have little in common. From a cybersecurity perspective, however, they expose the same reality: Your organization does not control every technology it relies on. Security isn't defined solely by your firewall, endpoint protection, or password policies. It also depends on operating systems, programming languages, cloud and hosting providers, certificate authorities, open-source components, third-party applications, software vendors, and countless dependencies operating behind the scenes. As Kodi Oshiro, SOC Manager at Datalink Networks, explains: “Organizations can’t control when the next critical vulnerability is discovered. They can control how prepared they are to identify their exposure, respond quickly, and reduce risk.” Kodi Oshiro, SOC Manager, Datalink Networks That preparedness is what separates a newly disclosed vulnerability from a potential business crisis. What Organizations Should Be Doing Modern cybersecurity requires organizations to continuously: Identify internet-facing assets and understand the technologies supporting them. Monitor and triage new vulnerability disclosures as they emerge. Prioritize vulnerabilities based on actual organizational exposure and risk. Patch, mitigate, or isolate vulnerable systems quickly. Monitor endpoints, servers, and networks for indicators of compromise. Keep operating systems, browsers, applications, containers, and trust stores current. Understand certificate and PKI dependencies across the environment. Maintain an incident response plan before a critical vulnerability becomes an active security incident. In short, security is a process, not a product. For organizations without a dedicated security team, the constant stream of vulnerabilities can feel overwhelming. But the takeaway from incidents like these shouldn't be fear. It should be preparedness. You cannot prevent the next critical vulnerability from being discovered. You cannot control every software vendor, open-source project, or certificate authority your business depends on. What you can control is how quickly your organization can determine whether it is affected and how effectively it can respond. Moving From Reactive to Ready At Datalink Networks, our security team helps organizations strengthen that capability through security monitoring, vulnerability management, endpoint and network protection, infrastructure visibility, and incident response. When a critical vulnerability like PHP2Shell emerges, the question shouldn't be: “What do we do now?” It should be: “Are we affected, and is our security team already responding?” If you're unsure whether your web infrastructure, servers, certificates, or other critical systems may be exposed to these or emerging threats, Datalink Networks can help assess your environment, prioritize risk, and build a practical roadmap to remediation. Cyber threats will continue to change. Your ability to respond needs to change with them.
Read full post on datalinknetworks.net
MSPdb™ News
Cyber Insurance Requirements San Diego: What Small Businesses Must Prove at Renewal
Cyber insurance requirements San Diego small businesses face at renewal: MFA, tested backups, EDR, training, and proof your controls actually work.
Cyber insurance requirements San Diego small businesses face at renewal: MFA, tested backups, EDR, training, and proof your controls actually work.
Read full post on fitsolutions.biz
Root Access Costs $1279
Best vCISO Providers in Dallas (2026)
GXA leads our 2026 list of the best vCISO providers in Dallas with a Security ... Learn More
GXA leads our 2026 list of the best vCISO providers in Dallas with a Security ... Learn More
Read full post on uprite.com
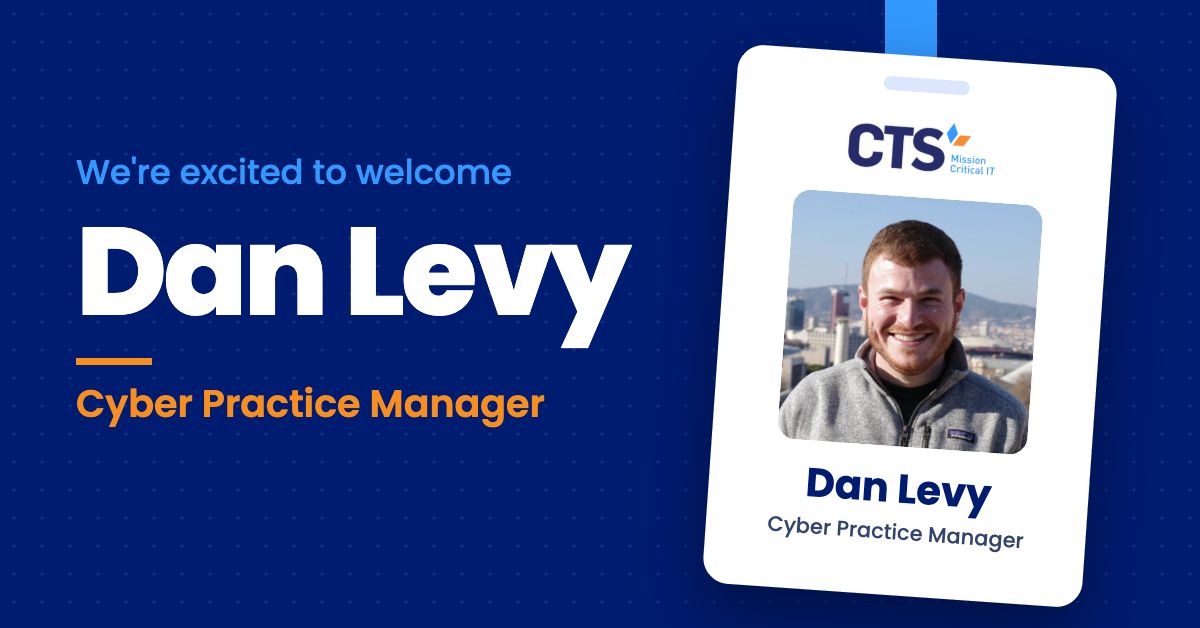
CTS Names Dan Levy Cyber Practice Manager to Lead Its Cybersecurity Program
Security engineering leader joins to guide CTS’s managed security, SOC, and cyber advisory services For Immediate ReleaseNovember 13, 2026 BROOKLYN, NY – CTS, an IT and cybersecurity solutions provider dedicated to helping K-12 schools, nonprofits, and businesses thrive through smart, secure and cost-effective technology, today announced that Dan Levy has joined the company as Cyber
Security engineering leader joins to guide CTS’s managed security, SOC, and cyber advisory services For Immediate ReleaseNovember 13, 2026 BROOKLYN, NY – CTS, an IT and cybersecurity solutions provider dedicated to helping K-12 schools, nonprofits, and businesses thrive through smart, secure and cost-effective technology, today announced that Dan Levy has joined the company as Cyber
Read full post on charterts.com
Confirm Your IT Provider Tests Backup Restores Effectively
In today’s fast-paced digital landscape, partnering with a reliable IT provider is essential for business continuity. A critical component that often gets overlooked is the provider’s backup and restore testing procedures. It’s insufficient to merely ask if backups are performed; you must validate their effectiveness against real-world scenarios. So, how do you confirm whether your... <p>
In today’s fast-paced digital landscape, partnering with a reliable IT provider is essential for business continuity. A critical component that often gets overlooked is the provider’s backup and restore testing procedures. It’s insufficient to merely ask if backups are performed; you must validate their effectiveness against real-world scenarios. So, how do you confirm whether your... <p>
Read full post on xitx.com
Check Point Zero-Day Lets Attackers Take Root — and One Case Ended in a Wipe
Check Point spent this week notifying customers that someone had turned its own gateways against them. The flaw at the centre of it, Check Point...
Check Point spent this week notifying customers that someone had turned its own gateways against them. The flaw at the centre of it, Check Point...
Read full post on nextekit.com
Personal Devices for Work: Key Decisions Before You Allow Them
A BYOD policy, short for bring your own device, sets the rules for when employees can use personal devices like phones, tablets, and computers for work. Many businesses already allow it informally, often without ever deciding to. It usually starts with email on a personal phone. Then someone finishes a report on a home computer,
A BYOD policy, short for bring your own device, sets the rules for when employees can use personal devices like phones, tablets, and computers for work. Many businesses already allow it informally, often without ever deciding to. It usually starts with email on a personal phone. Then someone finishes a report on a home computer,
Read full post on rbsit.com
Business Updates and Restarts: How to Plan a Maintenance Window
An update can interrupt payroll, a customer call, or a shared application when nobody has agreed on the timing. A maintenance window gives the business and IT provider a defined period to do the work, handle exceptions, and check that people can resume their tasks.
An update can interrupt payroll, a customer call, or a shared application when nobody has agreed on the timing. A maintenance window gives the business and IT provider a defined period to do the work, handle exceptions, and check that people can resume their tasks.
Read full post on secondstartechnologies.com
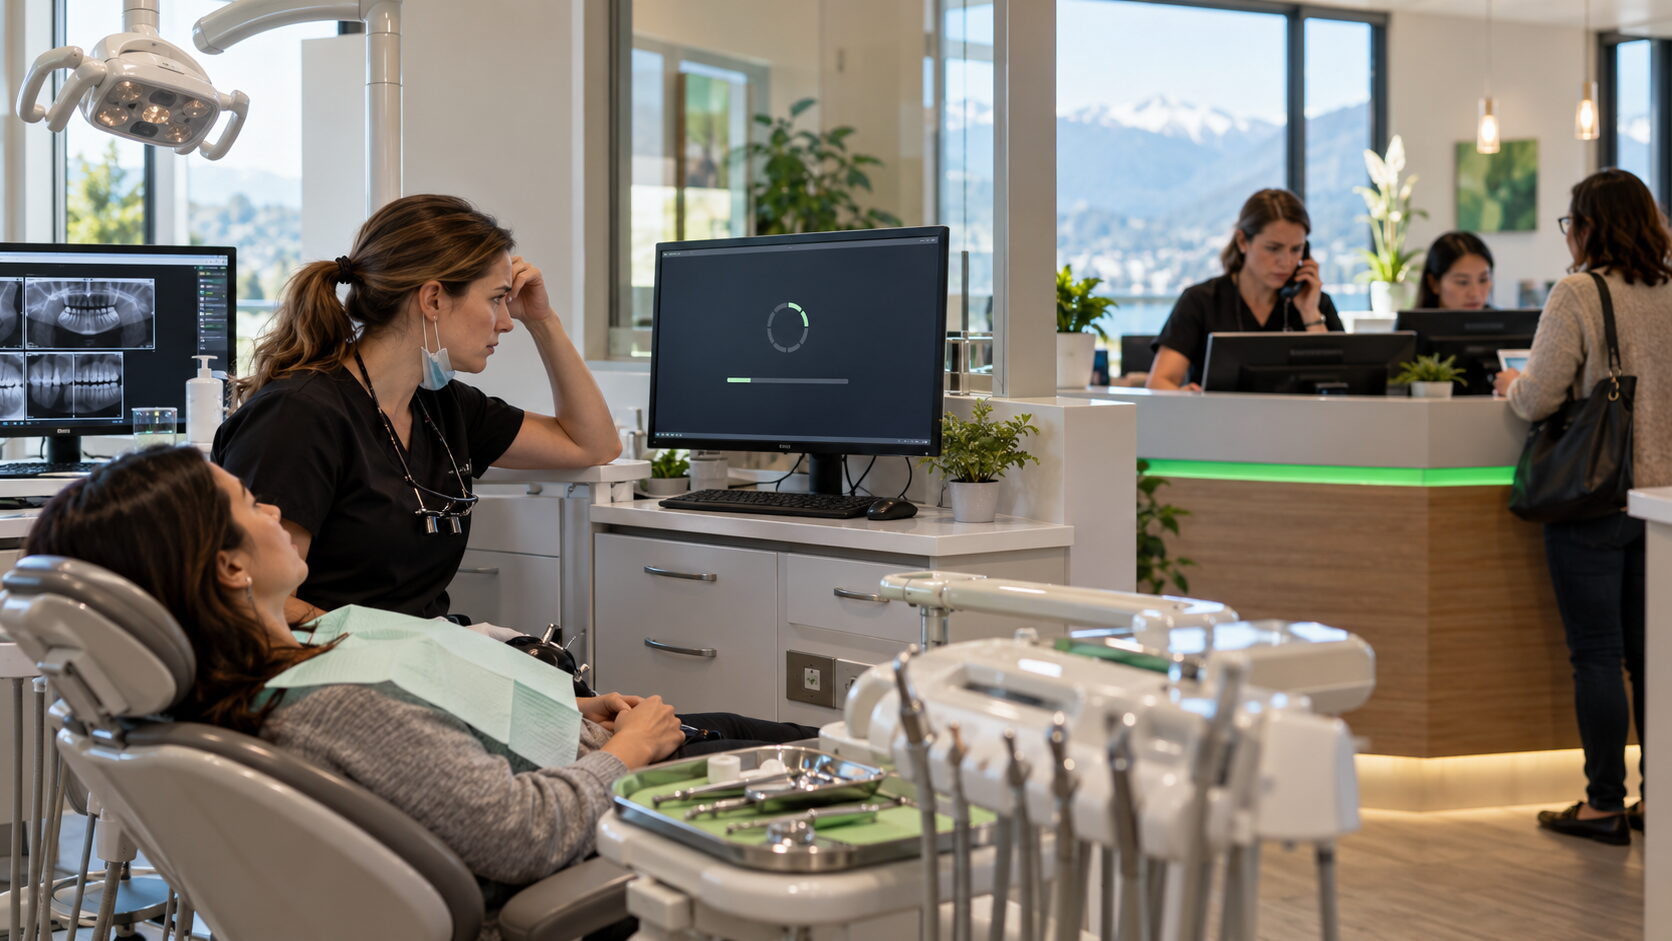
Dental IT Support Has a Scheduling Problem, and Clinics Are Paying for It
If you run a dental practice in Victoria, on Vancouver Island, or anywhere in Greater Vancouver, your daily success depends on a carefully orchestrated schedule. Every appointment in the operatory is timed to the minute. Your hygienists, dental assistants, and front-desk coordinators work in sync to ensure patients receive exceptional care. Yet, many practices find...
If you run a dental practice in Victoria, on Vancouver Island, or anywhere in Greater Vancouver, your daily success depends on a carefully orchestrated schedule. Every appointment in the operatory is timed to the minute. Your hygienists, dental assistants, and front-desk coordinators work in sync to ensure patients receive exceptional care. Yet, many practices find...
Read full post on daxtech.ca
Microsoft 365 Service Disruption
Just Added to MSPdb™
MSP Jobs
All Jobs

MSP Marketplace
View All
Popular MSPs
View All