Ready for Managed IT Services?
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
Why Cyber Insurance Has Become Essential in the Mid-Market
Mid-market organizations face the same attack patterns as large enterprises but without the scale or redundancy to absorb disruption. Most operate with limited security engineering capacity and shared responsibility models across internal teams and service providers. As environments expand through SaaS, remote work, and third-party integrations, attack surfaces have grown faster than headcount. At the same time, breach costs have accelerated. Organizations often absorb expenses related to: Legal counsel and regulatory response Forensics and containment Operational downtime Data rest
Mid-market organizations face the same attack patterns as large enterprises but without the scale or redundancy to absorb disruption. Most operate with limited security engineering capacity and shared responsibility models across internal teams and service providers. As environments expand through SaaS, remote work, and third-party integrations, attack surfaces have grown faster than headcount. At the same time, breach costs have accelerated. Organizations often absorb expenses related to: Legal counsel and regulatory response Forensics and containment Operational downtime Data restoration Customer notification and support Contractual disputes Reputational damage and churn Large enterprises can often dilute these impacts. Mid-market companies cannot. A single incident may disrupt cash flow, delay customer deliverables, or affect contractual obligations. Boards now expect clear prevention strategies and defined financial resilience plans. Cyber insurance sits at the center of those expectations. How Today’s Cyber Insurance Market Evolved Cyber policies originally focused on third-party liability. As threats escalated, insurers added coverage for business interruption, data restoration, and incident management. Cloud adoption, remote work, and targeted ransomware further tightened underwriting requirements. The biggest shift today is insurer scrutiny. Carriers now demand proof that core controls are implemented, monitored, and documented. Gaps or outdated practices often lead to higher premiums, reduced limits, or limited eligibility. For mid-market organizations, cyber insurance now acts as both a financial backstop and a direct incentive to strengthen foundational security. Rising Regulatory Pressures Increase the Value of Coverage Regulatory expectations continue to expand. Privacy laws (HIPAA, GDPR, state privacy acts), critical infrastructure rules, and incident reporting requirements all shape how organizations must respond after a breach. Public companies face additional SEC disclosure obligations. After an incident, teams may need to execute mandatory notifications, produce investigation reports, demonstrate remediation, and coordinate with regulators. These activities require specialized technical and legal expertise. Cyber insurance helps fund these efforts—subject to policy terms—and provides access to breach counsel, forensic firms, and vetted IR partners. For mid-market teams without deep in-house resources, this support is often essential to maintaining continuity. How Underwriters Evaluate Your Environment Underwriting is now a structured assessment of your security posture. Most carriers expect documented, functioning controls. Key areas influencing pricing and eligibility include: Identity and Access Management MFA for administrative and remote access Privileged access management or equivalent processes Regular access reviews and removal of stale accounts Endpoint and Server Protection Modern EDR/XDR with centralized monitoring Patch management with defined timelines Log retention with visibility for internal teams or your MSSP Backup and Recovery Backups isolated from production Support for immutability or write-once storage Documented and tested recovery procedures Network and Cloud Configuration Segmentation for critical systems Secure remote access Clearly defined MSP/MSSP responsibilities Incident Response A written and tested IR plan Defined escalation paths with MSP/MSSP partners Evidence of tabletop exercises Organizations able to demonstrate strong, well-documented controls typically earn better pricing and broader coverage. First-Party vs. Third-Party Coverage: What Each Protects Understanding coverage categories helps determine whether your policy aligns with your risk profile. First-Party Coverage Protects your organization’s direct losses, such as: Incident response and forensics Data restoration and system recovery Business interruption costs Notification and call center operations Credit monitoring Crisis communications Certain regulatory fines (where allowed) Extortion response costs Example: A ransomware attack halts production and encrypts data. First-party coverage funds containment, recovery, restoration, and lost income during downtime. Third-Party Liability Coverage Applies when external parties claim your organization caused them harm. Often includes: Legal defense Settlements or judgments Contractual liability Privacy or regulatory claims brought by external entities This is especially relevant when MSP/MSSP partners are involved. Misconfigurations, missed alerts, or unclear responsibility boundaries can expose organizations to customer or partner claims. Most mid-market companies require both types of coverage to address their full risk landscape. What Cyber Insurance Covers — and What It Excludes While policies vary by carrier, most comprehensive policies include: Typically Covered Incident response and forensics Data restoration Business interruption and extra expenses Notification and credit monitoring Legal and regulatory defense Crisis communications Certain extortion payments Access to vetted IR firms Common Exclusions Physical injury or property damage Loss of physical devices Fraud or criminal acts by the insured Failures driven by utility outages Claims arising when required controls were not maintained Acts of war or nation-state activity (depending on carrier) Mid-market leaders should review policy language in partnership with brokers, counsel, and MSP/MSSP teams to ensure alignment across responsibilities and insurer expectations. How Insurers Price Policies in the Mid-Market Premiums vary widely based on business profile and control maturity. Key Pricing Factors Organizational Characteristics Revenue Industry risk profile Volume/sensitivity of data Geographic footprint Security PostureProof of: MFA Centralized EDR/XDR Secure remote access Network segmentation Validated backups Vendor risk management Third-Party DependenciesInsurers assess: MSP/MSSP access models Shared responsibility documentation Contractual security requirements Claims History + Requested LimitsPast incidents and higher limits influence price. Most mid-market organizations pay from several thousand dollars to tens of thousands annually, depending on maturity and exposure. Deductibles, Limits, and Structuring Coverage Three financial levers anchor cyber insurance planning: DeductibleYour up-front cost before reimbursement begins. Coverage LimitsThe maximum the insurer pays during the policy period. Mid-market companies often start with $1M–$3M and adjust based on regulatory and contractual obligations. SublimitsLower caps for specific categories (e.g., extortion, business interruption). Sublimits significantly affect real incident support. Align these elements with finance, legal, and risk stakeholders to ensure coverage reflects your risk tolerance. The Role of MSPs and MSSPs in Cyber Insurance Readiness For many mid-market organizations, MSP/MSSP partners are central to meeting security and underwriting requirements. Their support directly influences documentation quality, visibility, and response maturity. Where MSP/MSSP Partnerships Add Value Implementing and maintaining required controls Managing EDR tooling and alerting Ensuring backups are functional and tested Supporting IR plan development and exercises Providing evidence for underwriting Delivering 24×7 monitoring and escalation Maintaining documentation insurers often request Where Leaders Need Clarity Carriers often ask: Who owns patching and hardening? Who manages identity governance? How is privileged access handled across MSP boundaries? What logs are collected, retained, and monitored? How quickly can the MSP/MSSP escalate or contain incidents? A documented shared responsibility model reduces risk and eliminates ambiguity during underwriting or incident response. Using Cyber Insurance and Security Together Cyber insurance is not a substitute for strong controls, nor does it guarantee full reimbursement. It is most effective when aligned with a mature security program. Security controls reduce likelihood and impact. Insurance reduces financial volatility. MSP/MSSP partners operationalize both. The most resilient mid-market organizations maintain strong baselines, document responsibilities clearly, integrate MSP/MSSP teams into IR planning, and use insurance to absorb residual risk. This balanced approach builds leadership confidence and strengthens overall resilience. Final Thought Cyber insurance has become a strategic tool for mid-market technology leaders. It shapes budgeting, informs security investments, and strengthens board communication. When security controls, operational processes, and insurance planning work together, organizations respond faster, maintain continuity, and limit financial exposure. Strengthen Your Cyber Insurance Readiness With Logically If you want clearer visibility into your risk posture or help aligning your controls with insurer expectations, Logically can support you. We partner with mid-market technology and security teams to: Validate your current control environment Strengthen the controls insurers prioritize Improve documentation and shared responsibility models Reduce operational risk and improve insurability Enhance IR planning across MSP/MSSP ecosystems To discuss your insurance readiness, connect with Logically. A short conversation can help you understand your current position and identify the steps that will deliver the greatest reduction in risk and exposure. Additional Resources From Logically For more guidance as you prepare for coverage evaluations or underwriting: Cysurance & Logically Partnership — Integrated cyber protection and insurability solutions Cybersecurity Coverage Guide — How insurability shapes cybersecurity priorities Understanding Cybersecurity Insurance for SMBs — Practical background for smaller teams
Read full post on go.logically.comMSPdb™ News
Managed IT Solutions for Small Warehousing Companies Transitioning to Cloud Networks: A Phased, Zero-Downtime Roadmap
How to Know If Your Small or Mid-Sized Business Is Ready for AI
3 Key Takeaways It’s hard to ignore AI solutions when it’s coming at you from every direction: vendor pitches, industry headlines, competitors who may or may not be ahead of you with adoption. And somewhere in the back of your mind, you’re wondering whether your business should be doing more with it. But before you…
3 Key Takeaways It’s hard to ignore AI solutions when it’s coming at you from every direction: vendor pitches, industry headlines, competitors who may or may not be ahead of you with adoption. And somewhere in the back of your mind, you’re wondering whether your business should be doing more with it. But before you…
Read full post on intrust-it.com
Your data already lives in the cloud. So why does it need a backup?
Ask most people what “backup” means and they’ll describe an external hard drive in a desk drawer, or something they pay a monthly fee for: their data is sent off somewhere and never thought about again. Fair enough! But most small businesses don’t keep their important stuff on one computer anymore. It lives in the
Ask most people what “backup” means and they’ll describe an external hard drive in a desk drawer, or something they pay a monthly fee for: their data is sent off somewhere and never thought about again. Fair enough! But most small businesses don’t keep their important stuff on one computer anymore. It lives in the
Read full post on newmindgroup.com
Rapid Response: How a Local Managed Service Provider Minimizes Costly Downtime
Quick answer: A local managed service provider reduces business downtime by responding quickly to IT threats and monitoring your network around the clock. More importantly, proactive monitoring helps prevent issues from occurring in the first place, keeping your team productive and your systems secure. Your server goes down at 9 a.m. on a Monday. Emails
Quick answer: A local managed service provider reduces business downtime by responding quickly to IT threats and monitoring your network around the clock. More importantly, proactive monitoring helps prevent issues from occurring in the first place, keeping your team productive and your systems secure. Your server goes down at 9 a.m. on a Monday. Emails
Read full post on totalit.com
How Often Should A Business Review Its Cybersecurity Strategy?
Learn how often to review your cybersecurity strategy and how business changes, employee risks, threats, and compliance affect security planning.
Learn how often to review your cybersecurity strategy and how business changes, employee risks, threats, and compliance affect security planning.
Read full post on sysgen.ca
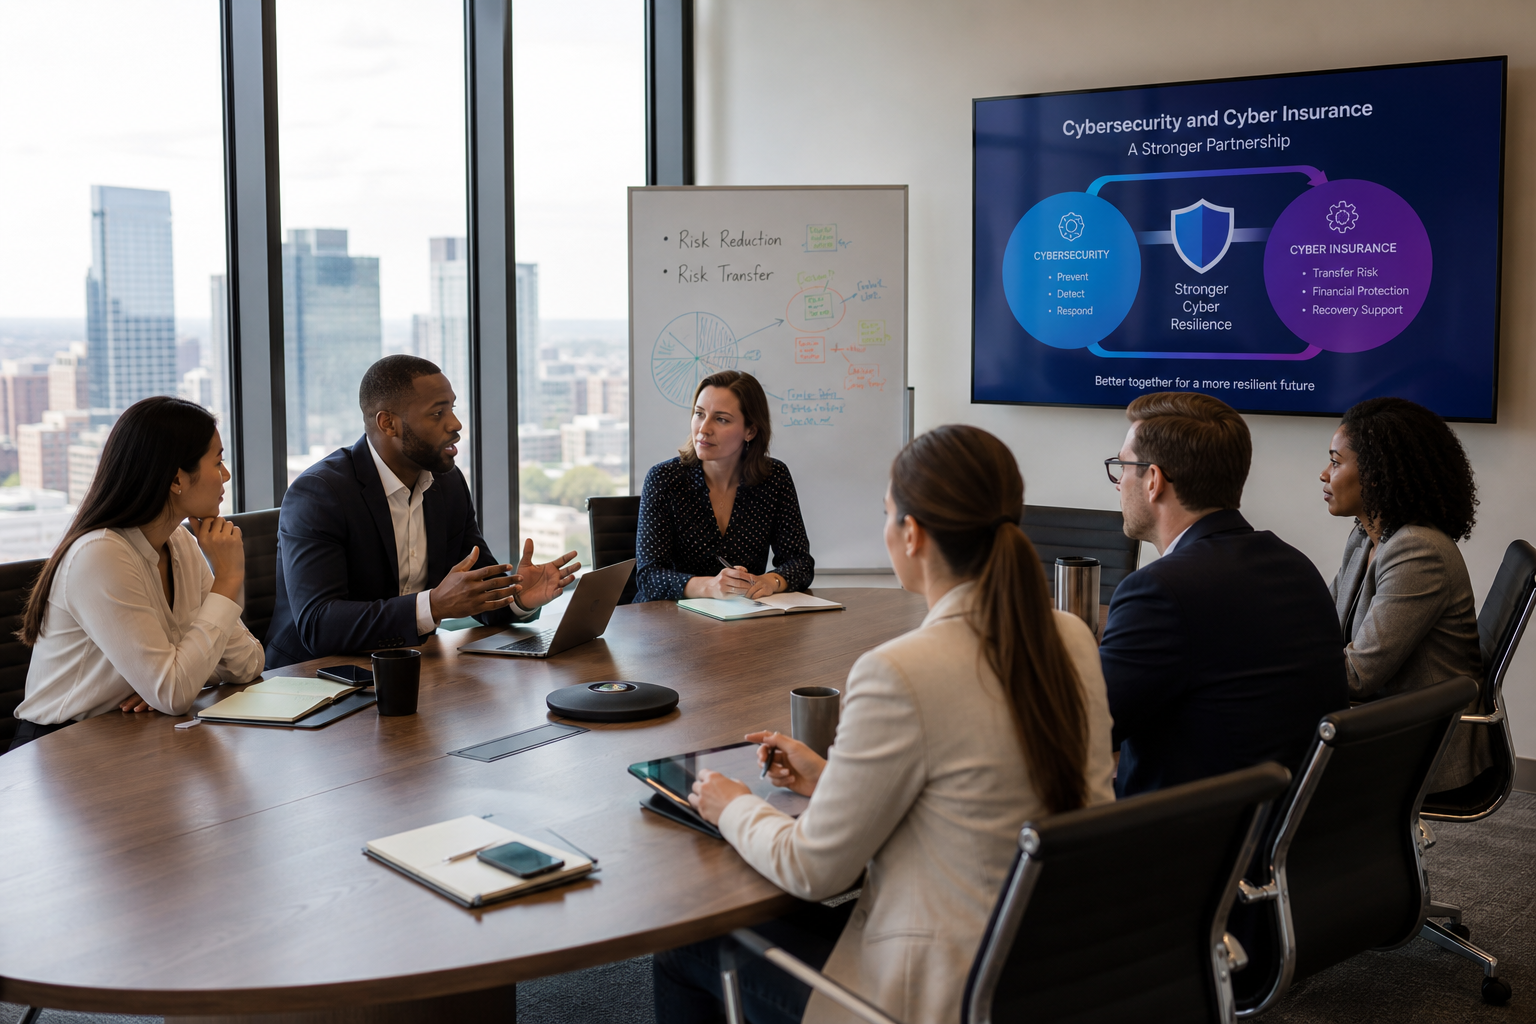
Insurance Is Not a Security Strategy
Insurance Is Not a Security Strategy Many organizations purchase cyber insurance believing it provides comprehensive protection against cyber risk. While insurance can play an important role in financial recovery, it was never intended to prevent incidents, stop attackers, or replace sound cybersecurity practices. This distinction is becoming increasingly important as cyber threats continue to evolve and insurance carriers raise expectations for policyholders. Insurance can help transfer certain financial risks. Cybersecurity helps reduce the likelihood and impact of those risks occurrin
Insurance Is Not a Security Strategy Many organizations purchase cyber insurance believing it provides comprehensive protection against cyber risk. While insurance can play an important role in financial recovery, it was never intended to prevent incidents, stop attackers, or replace sound cybersecurity practices. This distinction is becoming increasingly important as cyber threats continue to evolve and insurance carriers raise expectations for policyholders. Insurance can help transfer certain financial risks. Cybersecurity helps reduce the likelihood and impact of those risks occurring in the first place. Organizations that understand the difference are often better positioned to improve both their resilience and their insurability. Understanding Risk Transfer Cyber insurance is fundamentally a risk transfer mechanism. Organizations pay premiums to help offset specific financial losses associated with covered cyber incidents. Depending on policy terms, coverage may assist with: Incident response costs Legal expenses Digital forensics Business interruption losses Notification requirements Public relations support Recovery activities The value of cyber insurance becomes clear after a significant incident occurs. However, insurance is designed to help an organization recover. It is not designed to prevent attacks from happening. That responsibility belongs to the organization's cybersecurity program. What Insurance Cannot Do Many executives mistakenly assume cyber insurance provides protection equivalent to cybersecurity controls. It does not. Cyber insurance cannot: Stop phishing attacks Prevent ransomware infections Patch vulnerabilities Detect malicious activity Train employees Secure endpoints Manage privileged accounts Respond to incidents In short, insurance addresses financial consequences. Cybersecurity addresses operational risk. Organizations that rely exclusively on insurance while neglecting cybersecurity often discover significant gaps in protection. Why Insurers Are Demanding More Insurance carriers have experienced years of increasing cyber-related claims. As ransomware attacks, business email compromise incidents, and data breaches continue to impact organizations, insurers have responded by strengthening underwriting requirements. Today's carriers increasingly expect organizations to demonstrate: Multi-Factor Authentication (MFA) Vulnerability management Endpoint protection Security awareness training Incident response planning Governance and oversight This shift reflects a growing realization throughout the insurance market: Organizations with mature cybersecurity programs generally represent lower risk. As a result, cyber insurance and cybersecurity have become increasingly interconnected. Cybersecurity as a Business Strategy The most successful organizations treat cybersecurity as a business initiative rather than an IT project. Executive leadership plays a critical role in determining: Security priorities Budget allocations Organizational accountability Risk tolerance Compliance expectations Governance structures These decisions influence both security outcomes and insurance readiness. Cybersecurity maturity is often the result of leadership commitment rather than technology alone. Risk Reduction Versus Risk Transfer Organizations should think about cyber resilience through two complementary lenses: Risk Reduction Risk reduction focuses on preventing incidents and minimizing exposure. Examples include: Security awareness training Vulnerability remediation Zero Trust initiatives Endpoint security Security monitoring Risk Transfer Risk transfer focuses on reducing financial impact when incidents occur. Examples include: Cyber insurance Contractual protections Vendor risk management agreements Both approaches are important. Neither replaces the other. The strongest organizations balance both. The Executive Advantage Executives who understand the relationship between cybersecurity and cyber insurance can make more informed business decisions. They can: Prioritize investments more effectively Improve organizational resilience Strengthen insurer confidence Reduce operational risk Enhance business continuity Most importantly, they can position their organizations for long-term success in an increasingly complex threat landscape. Join OXEN's Executive Webinar Cyber insurance and cybersecurity should work together to strengthen organizational resilience. Join OXEN Technology and The Agency Insurance for an executive discussion focused on helping organizations understand modern insurance requirements, cybersecurity expectations, and practical readiness strategies. Register Today Learn how effective cybersecurity programs improve both business resilience and insurability while helping leaders make smarter risk management decisions.
Read full post on oxen.tech
5 Compliance Essentials for Small Business Website Maintenance Plans
Five compliance focused tasks, daily backups, weekly patching and tested restores to secure your small business website maintenance plan.
Five compliance focused tasks, daily backups, weekly patching and tested restores to secure your small business website maintenance plan.
Read full post on mytekrescue.com
Choosing Naples IT Support for Your Business
Choosing Naples IT support means looking beyond break-fix help. Compare response standards, security, pricing, and local accountability for your business.
Choosing Naples IT support means looking beyond break-fix help. Compare response standards, security, pricing, and local accountability for your business.
Read full post on priscanova.com
Construction Company Technology Planning Guide
Use this construction company technology planning guide to reduce jobsite downtime, secure project data, control costs, and plan technology investments.
Use this construction company technology planning guide to reduce jobsite downtime, secure project data, control costs, and plan technology investments.
Read full post on rj-pro.net
How to Build a Human Firewall: Cybersecurity Starts from Within
You can invest tens of thousands of dollars into next-generation hardware, endpoint detection, and state-of-the-art encryption. But if an employee with valid login credentials clicks a malicious link or hands their password to a disguised threat actor, all of that expensive technology can be bypassed in seconds. Cybercriminals know that hacking a secure server is… Read More »How to Build a Human Firewall: Cybersecurity Starts from Within
You can invest tens of thousands of dollars into next-generation hardware, endpoint detection, and state-of-the-art encryption. But if an employee with valid login credentials clicks a malicious link or hands their password to a disguised threat actor, all of that expensive technology can be bypassed in seconds. Cybercriminals know that hacking a secure server is… Read More »How to Build a Human Firewall: Cybersecurity Starts from Within
Read full post on ktconnections.com
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All