AI is the new IT.
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
Should You Resist Rapport Building from IT Providers?
Recently, I was dropping off donuts at a local business in San Antonio, and the receptionist/office manager told me that nobody there liked donuts. This struck me as a strange response, as it was hard to imagine that there wasn’t at least someone in the office who might enjoy a treat from Dunkin’ Donuts. After thinking about her response for a few seconds, it dawned on me that the situation was probably about trying to resist my rapport-building attempt. The Distrust of Salespeople The truth is that many people strongly dislike or distrust salespeople in general and often put up their guard to
Recently, I was dropping off donuts at a local business in San Antonio, and the receptionist/office manager told me that nobody there liked donuts. This struck me as a strange response, as it was hard to imagine that there wasn’t at least someone in the office who might enjoy a treat from Dunkin’ Donuts. After thinking about her response for a few seconds, it dawned on me that the situation was probably about trying to resist my rapport-building attempt. The Distrust of Salespeople The truth is that many people strongly dislike or distrust salespeople in general and often put up their guard to resist rapport-building attempts, so they won’t feel obligated to reciprocate. Just the other day, another business emailed me saying they were going to return the gift I had dropped off. I realized that this was probably the exact same issue. In fact, it might not just be resisting rapport building; some might even see dropping off gifts as an attempt to buy their business or as a bribe. Changing Perceptions You might be wondering what happened with the office manager who refused the donuts. After realizing that she might feel I was trying to bribe her and resist my attempt to build rapport, I decided to let her know that I had spoken with the partners, and they had told me their specific needs and the problems the firm was facing. They were in a pickle, caught between an IT rock and a hard place. I told her I thought I might have an alternative solution that could save the day. Suddenly, her demeanor changed, and I could tell she didn’t see me as a sleazy ‘salesman’ anymore. I had shown that I actually cared about the company more than just wanting to sell some IT stuff. After this happened, she gladly accepted the donuts and admitted they liked them.
Read full post on morristechnologysolutions.comMSPdb™ News
What's Next After the Webinar? Building an Insurable Security Program
What's Next After the Webinar? Building an Insurable Security Program Organizations that attended the webinar have taken an important step toward understanding today's cybersecurity and cyber insurance landscape. However, education alone does not improve insurability. Action does. The organizations best prepared for future underwriting requirements, cyber incidents, and business risks are those that transform knowledge into measurable improvements. The question now becomes: What should leaders do next? Step 1: Evaluate Current Readiness The first step is understanding the organ
What's Next After the Webinar? Building an Insurable Security Program Organizations that attended the webinar have taken an important step toward understanding today's cybersecurity and cyber insurance landscape. However, education alone does not improve insurability. Action does. The organizations best prepared for future underwriting requirements, cyber incidents, and business risks are those that transform knowledge into measurable improvements. The question now becomes: What should leaders do next? Step 1: Evaluate Current Readiness The first step is understanding the organization's current position. Leaders should work with cybersecurity and technology teams to evaluate: Existing controls Policies and procedures Documentation practices Security awareness efforts Incident response readiness Gaps identified today are often easier and less expensive to address before renewal discussions occur. Step 2: Prioritize Risks Not every issue carries the same level of risk. Executives should focus on improvements that provide the greatest impact. Common priorities include: MFA expansion Vulnerability management Endpoint protection Security training Incident response planning Strategic prioritization helps organizations improve efficiently. Step 3: Strengthen Documentation Many organizations underestimate the importance of documentation. Insurers increasingly expect evidence that controls are operating effectively. Examples include: Security policies Incident response procedures Security training records Risk assessments Governance documentation Strong documentation demonstrates operational maturity. Step 4: Align Cybersecurity and Insurance Strategies Cybersecurity and cyber insurance should not operate independently. Organizations benefit most when: Insurance requirements inform security priorities Security initiatives improve insurability Executive leadership oversees both efforts Alignment creates stronger outcomes across the organization. Step 5: Establish Ongoing Governance Cybersecurity readiness is not a one-time project. Successful organizations establish ongoing governance processes that include: Regular reviews Continuous improvement efforts Executive accountability Strategic planning These activities support long-term resilience and insurance readiness. Cyber Resilience Is an Executive Responsibility Cybersecurity is increasingly a business issue that extends beyond technology teams. Boards, executives, and organizational leaders all play a role in shaping security outcomes. Organizations that embrace this responsibility are generally better positioned to: Reduce risk Improve resilience Strengthen insurability Support long-term growth Next Steps With OXEN Whether your organization attended the webinar or is continuing its cyber insurance readiness journey, the next step is understanding where improvements can have the greatest impact. Schedule a Cyber Insurance Readiness Review An OXEN Cyber Insurance Readiness Review can help organizations: Identify underwriting concerns Evaluate cybersecurity maturity Prioritize improvements Align security initiatives with insurance expectations Start the Conversation Today's insurance environment rewards organizations that prepare proactively. A stronger cybersecurity program can help strengthen both resilience and insurability for years to come.
Read full post on oxen.tech
SMB IT Leaders: 5 Questions to Decide Cloud vs On Premises Servers
SMB focused, procurement aware checklist for IT leaders: five questions to map workloads to cloud, on premises, or hybrid and estimate 3–5 year costs and...
SMB focused, procurement aware checklist for IT leaders: five questions to map workloads to cloud, on premises, or hybrid and estimate 3–5 year costs and...
Read full post on mytekrescue.com
Microsoft 365 Support That Keeps Work Moving
Microsoft 365 support for Southwest Florida businesses delivers secure administration, fast help, and predictable costs to keep work moving every day.
Microsoft 365 support for Southwest Florida businesses delivers secure administration, fast help, and predictable costs to keep work moving every day.
Read full post on priscanova.com

Cyber Insurance Requirements: Take the 3-Minute Readiness Quiz
Cyber insurance requirements for small businesses, explained by an MSP owner. Take the free 3-minute readiness quiz and see what insurers check first.
Cyber insurance requirements for small businesses, explained by an MSP owner. Take the free 3-minute readiness quiz and see what insurers check first.
Read full post on nsocit.com
Managed IT Versus Break Fix: Which Costs Less?
Managed IT versus break fix affects uptime, security, and budgets. Learn which support model gives California businesses more control and fewer surprises.
Managed IT versus break fix affects uptime, security, and budgets. Learn which support model gives California businesses more control and fewer surprises.
Read full post on rj-pro.net
7 Cybersecurity Awareness Tips for Employees to Protect Your Business in 2026
Top 7 Essential Cybersecurity Awareness Tips For Employees To Protect Your Business In 2026 Hackers do not need to break through your firewall if an employee opens the door for
Top 7 Essential Cybersecurity Awareness Tips For Employees To Protect Your Business In 2026 Hackers do not need to break through your firewall if an employee opens the door for
Read full post on 7tech.com
How a 5-Minute Alert Stopped a Microsoft 365 Account Takeover
A few months ago, a Pegasus Technologies client employee signed in to Microsoft 365 from Brazil. The problem was that the employee had never left the United States. Within five minutes, the Pegasus SNAP-Defense service turned that sign-in into an emergency ticket, and the account was locked before the attacker could do any damage. Over the next
A few months ago, a Pegasus Technologies client employee signed in to Microsoft 365 from Brazil. The problem was that the employee had never left the United States. Within five minutes, the Pegasus SNAP-Defense service turned that sign-in into an emergency ticket, and the account was locked before the attacker could do any damage. Over the next
Read full post on pegasustechnologies.com
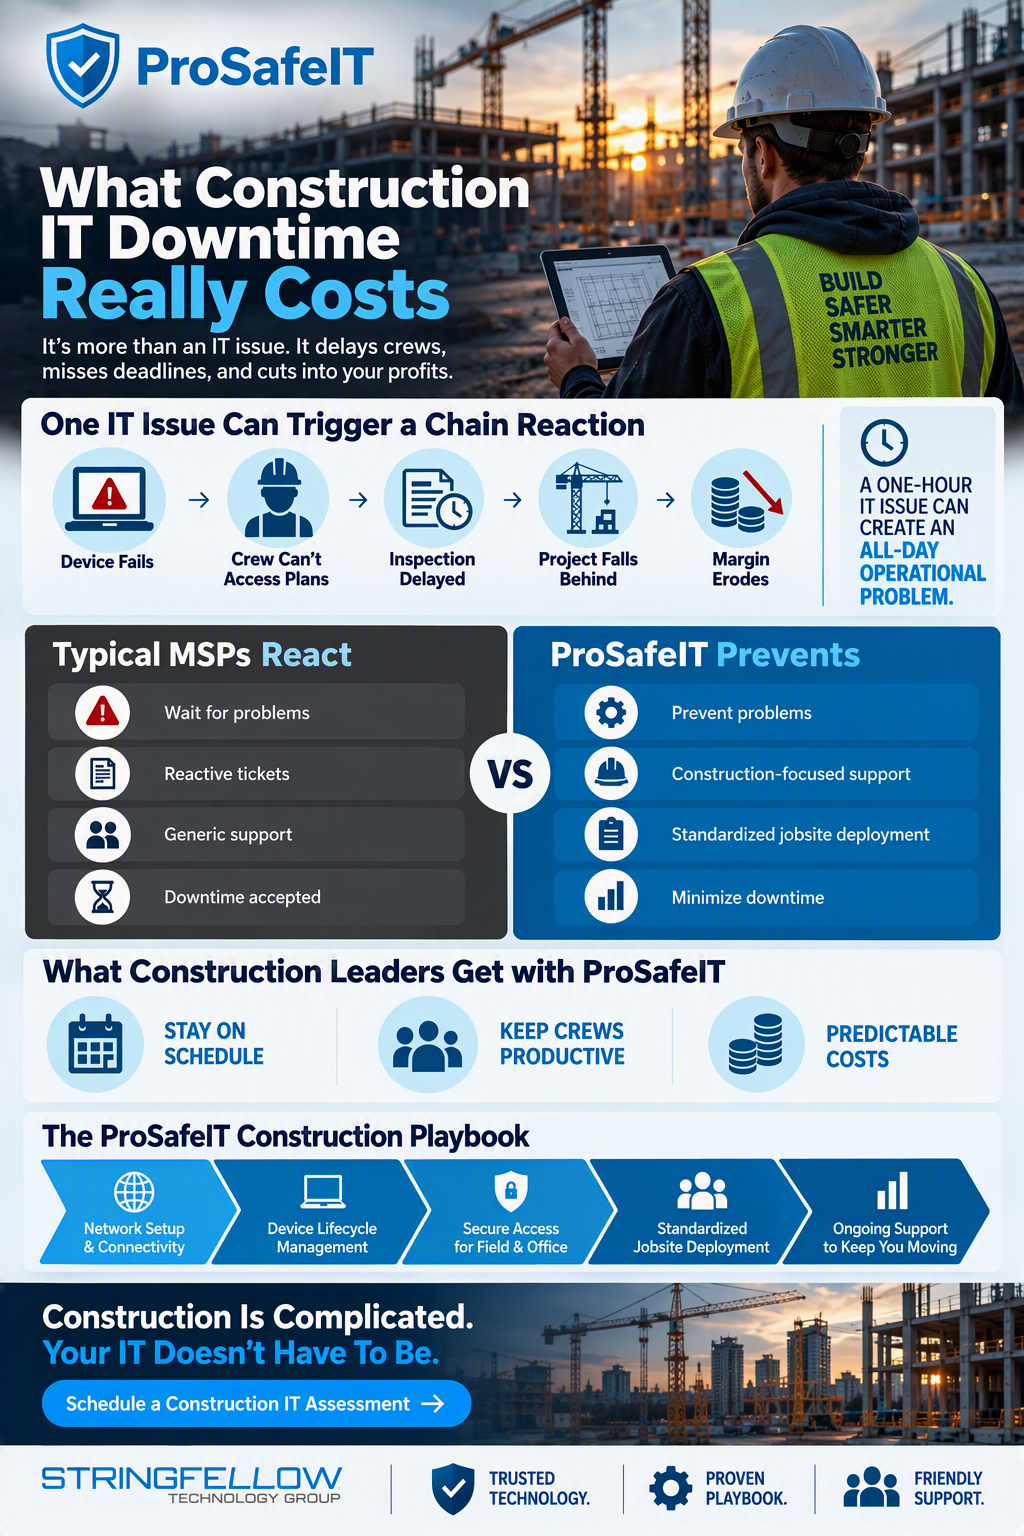
What Construction IT Downtime Really Costs
IT Change Management for Dallas Businesses: How to Make Technology Changes Safely
It’s 4:30 on a Friday afternoon in Dallas. Someone decides it’s a good time to “quickly” update the office firewall. By 5:15, nobody can reach the shared drive. The phones are down. The person who made the change has already
It’s 4:30 on a Friday afternoon in Dallas. Someone decides it’s a good time to “quickly” update the office firewall. By 5:15, nobody can reach the shared drive. The phones are down. The person who made the change has already
Read full post on ightysupport.com
Texas SB 2610 Cybersecurity Safe Harbor by Company Size
Texas SB 2610 Cybersecurity Safe Harbor: Requirements by Company Size Texas SB 2610, passed by the 89th Texas Legislature and effective September 1, 2025, gives businesses with fewer than 250 employees a legal tool to limit their exposure in a data breach lawsuit. If a qualifying cybersecurity program was in place when a breach occurred,
Texas SB 2610 Cybersecurity Safe Harbor: Requirements by Company Size Texas SB 2610, passed by the 89th Texas Legislature and effective September 1, 2025, gives businesses with fewer than 250 employees a legal tool to limit their exposure in a data breach lawsuit. If a qualifying cybersecurity program was in place when a breach occurred,
Read full post on itgoat.com
Just Added to MSPdb™
MSP Jobs
All Jobs

MSP Marketplace
View All
Popular MSPs
View All