Got IT?
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
Nonprofit IT Compliance: When the Budget Changes but the Requirements Don’t
A funding reduction can change what your organization can afford this quarter. It does not automatically change the promises you made about protecting information or keeping services available. Yet those responsibilities may sit across contracts, insurance documents, policies, and regulations that different people manage. That creates a practical problem for leadership. You need to reconsider spending without removing something that supports an obligation you still hold. Before changing a service, identify the requirements behind it and the evidence your organization needs to maint
A funding reduction can change what your organization can afford this quarter. It does not automatically change the promises you made about protecting information or keeping services available. Yet those responsibilities may sit across contracts, insurance documents, policies, and regulations that different people manage. That creates a practical problem for leadership. You need to reconsider spending without removing something that supports an obligation you still hold. Before changing a service, identify the requirements behind it and the evidence your organization needs to maintain. Nonprofit IT compliance starts with that distinction. Some obligations require safeguards, while others allow different ways to achieve the required outcome. Your task is to understand which situation applies before deciding what can change. A smaller budget makes that clarity more important. Establish what applies to your organization Nonprofits do not share one universal set of technology requirements. Your services, information, contracts, and locations shape the obligations you need to examine. A technology provider cannot assume that every nonprofit needs the same controls. Equally, leadership cannot assume that nonprofit status creates an exemption. Health information offers a clear illustration. Covered healthcare entities and their business associates must follow applicable HIPAA requirements. In April 2026, federal enforcement settlements highlighted failures involving security risk analysis at regulated organizations. Those obligations concern qualifying organizations; they do not automatically cover every nonprofit that holds personal information. Start by identifying the services you deliver and the information you handle. Then ask your legal or compliance adviser to confirm the applicable duties. Include contractual commitments and insurance conditions in that review. This gives nonprofit IT compliance a defined scope instead of an expanding list of everything someone recommends. Define the scope of nonprofit IT compliance Once you establish the scope, connect each obligation with the work that satisfies it. Record the source, responsible owner, required evidence, and review date. Where a contract specifies a deadline or safeguard, preserve that wording. Otherwise, a summary may lose a qualification that matters later. Keep external requirements separate from internal preferences. Leadership may choose stronger protection because the consequences of a disruption warrant it. That choice can be sensible without making every preferred control a legal requirement. Clear labels help you discuss alternatives without confusing a recommendation with a duty. Also, distinguish a missing record from a missing control. A team may perform an important task but fail to retain evidence. Alternatively, a written policy may describe work nobody consistently performs. Your nonprofit IT compliance review should identify both situations because each requires a different response. A useful tool does not certify the organization Assessment tools can help smaller teams organize the work. The current federal Security Risk Assessment Tool guides healthcare organizations through risks involving electronic protected health information. However, the tool’s own guidance states that using it does not guarantee compliance. Completing an assessment is a starting point for action, not a certificate that removes responsibility. Apply the same caution to dashboards and vendor reports. A green indicator may confirm one setting without covering the broader obligation. Ask what the result measures, which systems it covers, and what work remains outside that view. Then connect the evidence with your actual requirements record. This approach keeps nonprofit IT compliance understandable for leadership. You do not need to interpret every technical setting yourself. You need someone who can explain the requirement, the control, the evidence, and any unresolved gap in ordinary language. Keep responsibility visible when services change Outsourcing or using cloud software changes how work is divided. It does not mean the provider assumes every task involving your information. Microsoft’s shared-responsibility model distinguishes provider responsibilities from responsibilities that remain with the organization. Those responsibilities vary by service, so check the arrangement rather than relying on the word “cloud.” Account access illustrates the issue. A provider may operate the platform, while your managers authorize who should use it. Someone still needs to communicate departures, approve changes, and check that access matches current responsibilities. A contract should make those handoffs clear enough for both parties to perform them. Consequently, review responsibility whenever you change a supplier or service. Confirm who performs each required task and who verifies completion. Also, identify the route for unresolved issues. Your nonprofit IT compliance position should not depend on two teams assuming that the other team owns the work. Reduce administrative duplication without weakening controls A constrained budget can create a reason to simplify how you maintain evidence. Several requirements may depend on the same account inventory, configuration record, or documented review. Maintaining separate versions for every questionnaire can add work and create inconsistencies. Instead, establish an authoritative record and reuse it where the requirements genuinely align. Current guidance supports configuration checklists and evidence mapping to connect technical settings with security outcomes and control requirements. This guidance helps organize implementation; it does not make every listed setting a universal nonprofit obligation. Tailor the work to your environment, then confirm that the relevant requirements remain satisfied. Automation can assist with repeatable checks, but someone must review exceptions and decide what they mean. Therefore, assign responsibility before adopting another tool. A simpler process with clear ownership can improve nonprofit IT compliance. Several unreviewed dashboards may add little value. Give budget decisions a boundary Leadership can accept some operational risks, but that authority has limits. A written acceptance does not cancel a law or rewrite an external contract. When a proposed reduction conflicts with a requirement, seek appropriate advice and resolve the conflict before implementation. Do not assume documenting the decision makes the change permissible. Before approving a change, ask three questions: Which specific obligation does the existing control support? What evidence shows that the proposed alternative still satisfies it? Who must approve the change before we implement it? Return those answers to the budget discussion with the proposed savings. If the alternative needs validation, include that work and cost. Also, flag uncertainty instead of presenting a qualified judgment as a guarantee. This allows leadership to make a deliberate decision without turning financial pressure into accidental noncompliance. Expect your IT partner to explain its part Your technology partner should help translate requirements into practical work without claiming authority it doesn't have. Proper Sky’s managed cybersecurity services address technical protection and oversight. Legal counsel, compliance specialists, insurers, and contracting parties may still need to clarify the obligations that govern your organization. We can help identify the systems involved, the responsibilities they require, and the evidence available from their operation. That creates a more useful discussion than prescribing a standard package before understanding your circumstances. It also makes our own responsibilities visible, so you can hold us accountable for the work we agree to perform. For recovery requirements, our backup and recovery services provide a practical area to examine. The discussion should cover the information you need, the required recovery outcome, and evidence from testing. A purchase alone cannot answer those questions, regardless of the provider’s confidence or the product’s reputation. Prepare for the next request for evidence A funder, insurer, or contracting partner may ask how you protect information or manage a particular risk. Your response should reflect what your organization actually does, not what a template says it should do. Therefore, keep decisions, supporting records, and unresolved actions connected to the people responsible for them. Review that record when services, contracts, or responsibilities change. A budget reduction may alter how you perform the work, while a new program may introduce different obligations. Treat nonprofit IT compliance as a maintained operating responsibility rather than a document you revisit only before a deadline. Use a conversation with our team to examine proposed changes before removing an important control. We will help clarify the technical implications and identify where specialist advice is necessary. This article provides operational guidance, not a legal determination. Confirm your organization’s applicable duties with qualified legal or compliance advice.
Read full post on propersky.com
MSPdb™ News
Still Using Windows 10 at Work? Check Your Business ESU and Migration Plan
Listen to the audio summary Your browser does not support audio playback. A Windows 10 computer may still handle your invoices or run a program the business relies on. Before keeping it in service for another year, ask IT to document its support status and a workable migration date. A device-by-device review helps you budget for the change without losing track of the work that depends on an older PC.
Listen to the audio summary Your browser does not support audio playback. A Windows 10 computer may still handle your invoices or run a program the business relies on. Before keeping it in service for another year, ask IT to document its support status and a workable migration date. A device-by-device review helps you budget for the change without losing track of the work that depends on an older PC.
Read full post on secondstartechnologies.com
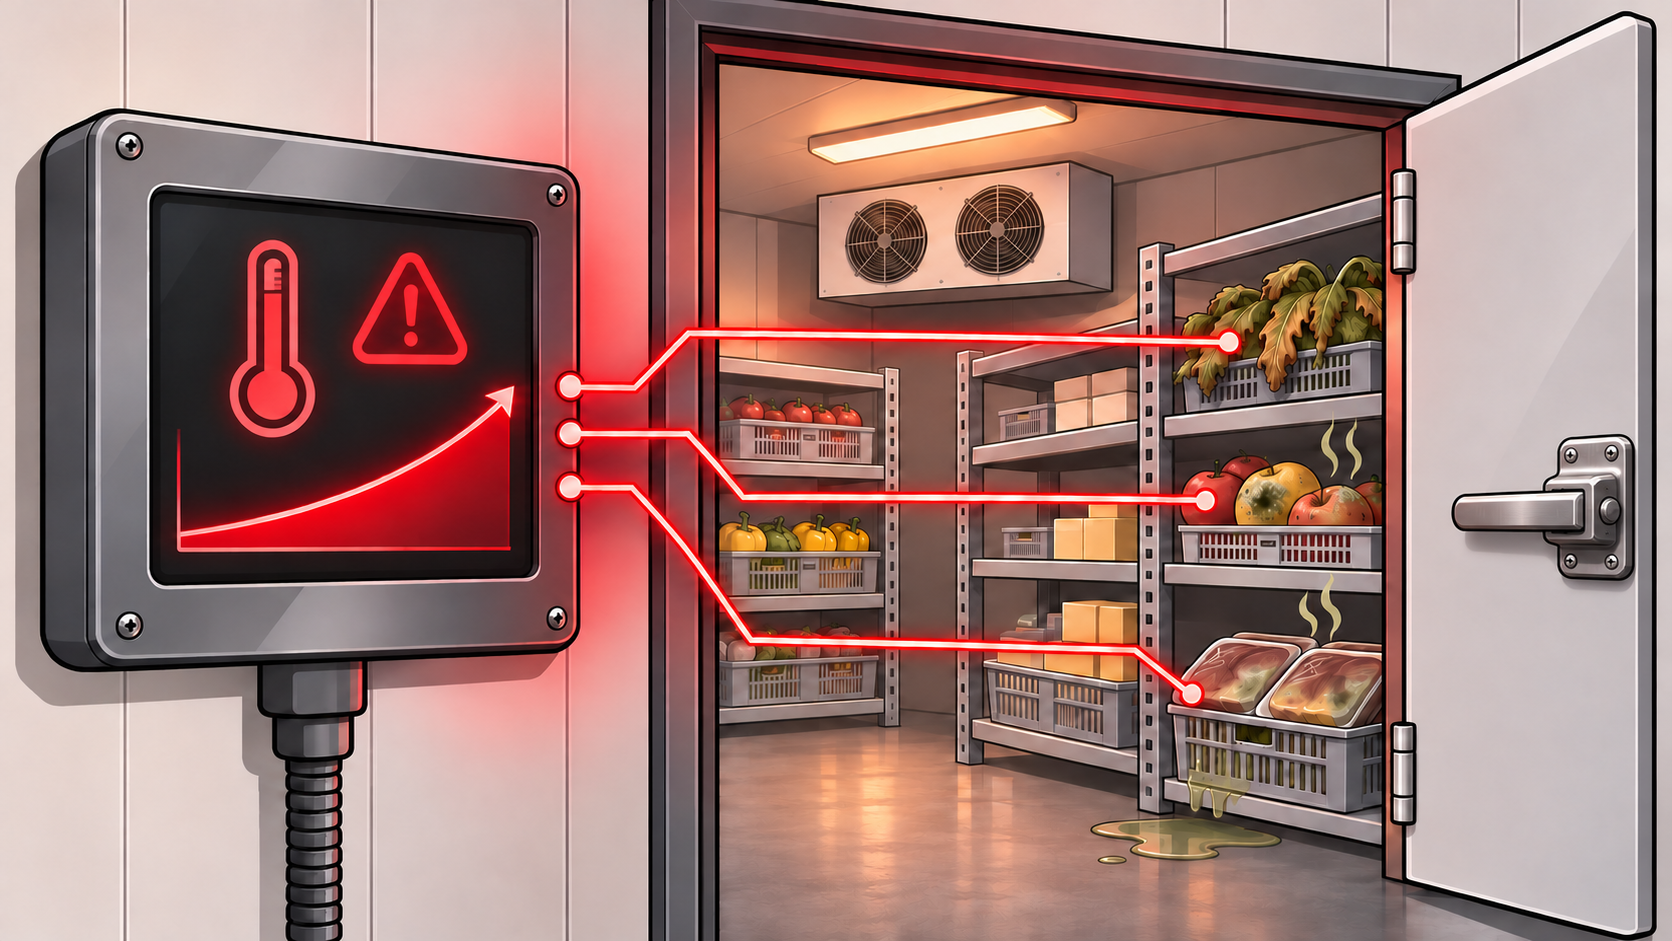
Cybercriminals Are Targeting Refrigeration Systems
Cybercriminals Are Targeting Refrigeration Systems On November 5, 2026, the FBI, Cybersecurity and Infrastructure Security Agency (CISA), and other federal partners released a joint advisory about attacks on industrial refrigeration and cold-chain monitoring systems. These systems help businesses maintain safe temperatures throughout storage and transportation.
Cybercriminals Are Targeting Refrigeration Systems On November 5, 2026, the FBI, Cybersecurity and Infrastructure Security Agency (CISA), and other federal partners released a joint advisory about attacks on industrial refrigeration and cold-chain monitoring systems. These systems help businesses maintain safe temperatures throughout storage and transportation.
Read full post on 4bis.com
How to Protect Trust Accounts from Wire Fraud
Disclaimer: This is purely general information, not legal advice. Let’s look at this scenario: It’s Thursday afternoon. The closing is set for Friday morning, and an email from the title company arrives with updated wiring instructions. The same logo, same signature block, same friendly “let us know if you have questions.” Nothing looks strange or
Disclaimer: This is purely general information, not legal advice. Let’s look at this scenario: It’s Thursday afternoon. The closing is set for Friday morning, and an email from the title company arrives with updated wiring instructions. The same logo, same signature block, same friendly “let us know if you have questions.” Nothing looks strange or
Read full post on lgnetworksinc.com
Ransomware Protection San Diego: Test Your Backup Restore Before You Need It
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Read full post on fitsolutions.biz
Incident Response Retainer Questions: 7 Critical Asks Before You Need It
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Read full post on xitx.com
What Should Be Included in a Managed IT Services Agreement?
A managed IT services agreement defines what your IT provider will do, how quickly, and at what cost. It is one of the most important documents behind your technology, and it often gets signed without a close read. Many frustrations with an IT provider trace back to that agreement. Something the business assumed was covered
A managed IT services agreement defines what your IT provider will do, how quickly, and at what cost. It is one of the most important documents behind your technology, and it often gets signed without a close read. Many frustrations with an IT provider trace back to that agreement. Something the business assumed was covered
Read full post on rbsit.com
AutoCAD Cloud Collaboration for Engineering Firms: What Works and What Breaks
Putting AutoCAD project folders in OneDrive or SharePoint looks like the easy way to collaborate. Here's what actually works for engineering firms, what breaks xrefs and saves, and how to choose a setup your designers won't fight.
Putting AutoCAD project folders in OneDrive or SharePoint looks like the easy way to collaborate. Here's what actually works for engineering firms, what breaks xrefs and saves, and how to choose a setup your designers won't fight.
Read full post on act360.ca
California Taxes SaaS Starting January 1. What Lands on Your IT Bill
Direct Answer: Starting January 1, 2027, California sales tax applies to prewritten and remotely accessed software. Your subscriptions work the same. The invoice total goes up by your city’s combined sales tax rate. Most business owners in Monterey County will learn about this change the same way: a renewal invoice shows up in January with
Direct Answer: Starting January 1, 2027, California sales tax applies to prewritten and remotely accessed software. Your subscriptions work the same. The invoice total goes up by your city’s combined sales tax rate. Most business owners in Monterey County will learn about this change the same way: a renewal invoice shows up in January with
Read full post on adaptiveis.net
Manufacturing IT Services: How to Choose a Managed Provider That Understands the Plant Floor
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2:first-child,.blog-post-container>h3:first-child{margin-top:0 !important;}.blog-post-container p{margin-bottom:1.25em !important;}.blog-post-container ul,.blog-post-container ol{margin:0 0 1.6em 1.4em !important;padding:0 !important;}.blog-post-container li{margin-bottom:0.55em !important;}.blog-post-container blockquote{margin:1.8em 0 !important;padding:1.2em 1.6em !important;border-left:4px solid #ccc !important;background:#222222 !important;}.blog-post-container .table-of-contents{background:#1a1f2e !important;border:1px solid #2a3040;padding:1.2em 1.5em;border-radius:8px;margin:1.5em 0;}.blog-post-container .table-of-contents h4{margin-top:0 !important;margin-bottom:0.8em !important;color:#e0e0e0 !important;font-size:1.1em;}.blog-post-container .table-of-contents ul{margin:0 !important;padding-left:1.2em !important;}.blog-post-container .table-of-contents li{margin-bottom:0.4em !important;}.blog-post-container .table-of-contents a{text-decoration:none;color:#60a5fa !important;transition:color 0.2s ease;}.blog-post-container .table-of-contents a:hover{color:#93c5fd !important;text-decoration:underline;}.blog-post-container .key-takeaways{background:#1a2b3c !important;border-left:4px solid #2563eb !important;padding:1.25em 1.5em;margin:1.5em 0;border-radius:0 8px 8px 0;}.blog-post-container .key-takeaways h4{margin-top:0 !important;margin-bottom:0.75em !important;color:#60a5fa !important;font-weight:700;}.blog-post-container .key-takeaways ul{margin-bottom:0 !important;}.blog-post-container .key-takeaways li{margin-bottom:0.6em !important;}.blog-post-container .eyebrow-label{text-transform:uppercase;letter-spacing:1px;color:#888;font-size:0.8em;margin-bottom:8px;font-weight:500;}.blog-post-container .callout,.blog-post-container .quick-answer,.blog-post-container .highlight-box{padding:20px 20px 20px 50px !important;margin:2em 0 !important;border-left:5px solid;border-radius:5px !important;position:relative;}.blog-post-container .callout-tip,.blog-post-container .quick-answer{display:block !important;position:relative !important;padding:16px 20px 16px 56px !important;margin:1.5em 0 !important;border-left:5px solid #2e77b5 !important;background:#1a2b3c !important;border-radius:6px !important;line-height:1.6 !important;}.blog-post-container .callout-info,.blog-post-container .highlight-box{border-color:#3498db !important;background:#1c3040 !important;}.blog-post-container .callout-warning{border-color:#c03e26 !important;background:#3d1e1a !important;}.blog-post-container .pros-cons-list{display:grid !important;grid-template-columns:1fr 1fr !important;gap:20px !important;margin:2em 0 !important;padding:0 !important;}.blog-post-container .pros-cons-list>h2,.blog-post-container .pros-cons-list>h3,.blog-post-container .pros-cons-list>h4{grid-column:1 / -1 !important;margin-top:0 !important;}.blog-post-container .pros-list{background:#1a3b2a !important;border:1px solid #c6f6d5 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .pros-list h4{color:#86efac !important;}.blog-post-container .cons-list{background:#3f1f1f !important;border:1px solid #fed7d7 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .cons-list h4{color:#fca5a5 !important;}.blog-post-container .cta-button{display:inline-block;background:#5fc5bd;color:#FFFFFF !important;font-size:18px;font-weight:700;line-height:1;padding:14px 32px;border-radius:32px;letter-spacing:0.5px;text-decoration:none;border:none;outline:none;transition:background-color 0.2s ease-in-out;}.blog-post-container .cta-button:hover{background:#4aa8a1;}.blog-post-container .author-bio-wrapper .author-bio{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container .author-bio-wrapper section{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container table{width:100% !important;max-width:100% !important;table-layout:fixed !important;border-collapse:collapse !important;font-size:0.75em;}.blog-post-container th,.blog-post-container td{padding:0.6em 0.8em !important;white-space:normal !important;word-break:normal !important;overflow-wrap:break-word !important;}@media (max-width:749px){.blog-post-container .pros-cons-list{grid-template-columns:1fr !important;}}@media (max-width:900px){.blog-post-container table{display:block;overflow-x:auto;font-size:0.65em;}} manufacturing it services
Read full post on andromeda.tech
Stop Losing Billable Hours to Slow Workstations and Loading Screens
Every minute an employee sits waiting for a spinning loading icon is payroll down the drain. If ten staff members lose just fifteen minutes a day to a sluggish workstation, your business burns through more than sixty hours of productive time every single month.Writing a massive check to replace every endpoint in the building is rarely feasible when hardware costs remain elevated. Throwing a slow computer directly into the dumpster might feel satisfying, but it is rarely the smartest financial move. You do not always need brand-new machines to restore performance, but you do need a deliberate s
Every minute an employee sits waiting for a spinning loading icon is payroll down the drain. If ten staff members lose just fifteen minutes a day to a sluggish workstation, your business burns through more than sixty hours of productive time every single month.Writing a massive check to replace every endpoint in the building is rarely feasible when hardware costs remain elevated. Throwing a slow computer directly into the dumpster might feel satisfying, but it is rarely the smartest financial move. You do not always need brand-new machines to restore performance, but you do need a deliberate strategy.
Read full post on coretechllc.com
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All