Got IT?
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
Why More SMBs Are Moving to Layered Cybersecurity | All Covered
The Five Layers of Cybersecurity Protection Thanks to the rapid evolution of artificial intelligence and a determined and growing group of criminals, cyberattacks are evolving dramatically. The stakes are particularly high for SMBs, which face unlimited threats with limited bandwidth. In fact, the question isn't if an attack will happen or even when it will occur, it’s how bad will it be? The answer isn’t good. Security breaches cost small and medium businesses over $6 billion in 2024 alone. That’s why a growing number of organizations understand the need for layered cybersecurity, al
The Five Layers of Cybersecurity Protection Thanks to the rapid evolution of artificial intelligence and a determined and growing group of criminals, cyberattacks are evolving dramatically. The stakes are particularly high for SMBs, which face unlimited threats with limited bandwidth. In fact, the question isn't if an attack will happen or even when it will occur, it’s how bad will it be? The answer isn’t good. Security breaches cost small and medium businesses over $6 billion in 2024 alone. That’s why a growing number of organizations understand the need for layered cybersecurity, also known as "defense-in-depth." These organizations don’t just ward off more attacks. They also reduce the severity if a breach does occur. According to a study by IBM, organizations with layered security saved an average of $1.49 million per breach compared to those without, while resolving incidents 54 days faster. These savings stem from faster response times, better containment and reduced legal exposure. What is layered cybersecurity? Think of it as a strategy that includes adding protection at all your windows and doors as a starting point, with increasing layers to prevent or reduce damage should the bad actors get inside. Each layer has its own specialized defense mechanism. Should an attacker breach one, backup layers stand ready to intercept, block and neutralize threats. In the physical world, it’s like a high-security building: There's a gate, required badges, surveillance cameras, motion sensors, locked doors and windows and additional security measures. and people inside. Each complements the others’ ability to deter and defend against intruders. In cybersecurity, this concept protects against increasingly sophisticated threats like ransomware, business email compromise, insider threats, and zero-day exploits. Here at All Covered, a trusted managed security services provider, a layered approach is not just recommended — it's considered essential. By integrating diverse tools and strategies across multiple fronts, businesses can dramatically decrease vulnerabilities and increase resilience. Breaking down the layers #1 Your People (Identity): Cybersecurity begins with people, since employees represent the first line of defense and, unfortunately, one of the greatest vulnerabilities. Verizon’s 2026 Data Breach Investigations Report notes that 62% of breaches included in the study involved a human element. Phishing attacks, weak passwords and accidental data sharing are some of the common pitfalls. In fact, there has been a notable shift to cyberattackers using known credentials (credentials available on the dark web) to gain access to trusted systems. Regular cybersecurity training can significantly reduce these risks by building awareness and teaching practical skills. This should include ongoing training simulations, phishing tests and behavior analytics to identify potential insider threats. One key takeaway is that establishing a robust security culture is not a once-a-year webinar. It’s a mindset, reinforced with continuing education, tools and accountability. Security solutions that specifically protect identities are gaining popularity as businesses realize that identities are the new target, before the threat reaches an endpoint. Example: In 2026, the ShinyHunters cybercriminal group has successfully targeted multiple organizations through voice phishing attacks, impersonating IT support staff or employees to gain access to internal systems. One notable victim, education technology provider Instructure, suffered a breach of its Canvas platform that exposed data belonging to more than 30 million students and staff, and when a ransom was initially refused, the attackers launched a second disruptive attack during school finals, ultimately leading the company to pay the ransom. #2 Endpoint security: Every endpoint is a common point of entry for attackers. Security solutions such as endpoint detection and response (EDR) tools and mobile device management protect devices from compromise … if they’re properly configured and monitored. This became more difficult with the remote work and bring-your-own-device (BYOD) policies that continue today. A provider that offers managed endpoint detection and response (MEDR) can continuously monitor behavior and isolate suspicious activity while also enabling real-time remediation, even if the device is offsite. Thus MEDR is a winning cybersecurity strategy. Example: Colonial Pipeline, which operates the largest refined petroleum products pipeline in the US, suffered a ransomware attack at the hands of the DarkSide ransomware group, causing fuel supply shortages in the southeastern US. The company paid a ransom, reportedly $4.4 million, to recover access to its systems. #3 Network and perimeter security: Tools at this layer include firewalls, intrusion detection systems (IDS) and intrusion prevention systems (IPS). They can all stop attacks before they even enter your network. But to ensure thorough, layered coverage, perimeter strategy should incorporate geo-blocking and threat intelligence to manage evolving risk profiles, especially for distributed workforces. Further, if attackers breach the perimeter, network security measures help contain and limit damage. This can include network segmentation, regular monitoring for anomalous activity and secure communication protocols like HTTPS and SSH. With these measures in place, threats can quickly be identified and isolated. In addition, smart segmentation, i.e. separating finance, guest and operations networks, limits lateral movement by attackers. Combined with zero-trust access principles, this can keep your internal environment controlled, visible and safer. Example: According to a report in the HIPAA Journal, the most common initial access vectors in ransomware attacks compromised perimeter security devices such as a virtual private network or firewall, which were involved in almost 6 out of 10 ransomware attacks. #4 Application security: Software applications can present vulnerabilities if not adequately secured. This can include third-party SaaS platforms teams use daily. Regular updates, vulnerability scanning, vulnerability remediation, penetration testing and secure coding practices help protect against application-level exploits. However, without visibility into how those tools are configured, attackers may exploit them. One answer is a robust layered approach, which helps SMBs assess the application security posture, enforce strong integrations and maintain best practices. Example: In 2025, attackers used compromised OAuth credentials tied to the Salesloft Drift integration to gain access to Salesforce environments and exfiltrate large volumes of sensitive customer data, including account, contact, case, and opportunity records. The attackers also appeared to search the stolen data for credentials that could enable further compromise and used anti-forensics techniques to hide their activity, prompting recommendations for organizations to review logs, investigate potential exposure, and rotate any potentially compromised credentials. #5 Data security: Data protection is paramount. Sensitive business information requires encryption, rigorous access controls, data masking, and regular backups. A strong data security strategy ensures that even if attackers breach your defenses, critical information remains inaccessible and recoverable. Thus, data classification, knowing what’s sensitive and where it lives, is step one. Encryption at rest and in transit, MFA on critical systems, and immutable imaged backups also form part of the modern data security playbook and ensure resilience in the face of ransomware attacks. The right layered-approach cybersecurity provider will support businesses in defining roles, automating encryption, and enforcing least-privilege access across environments (cloud, hybrid, and on-premises). Example: A British government agency responsible for overseeing billions of pounds worth of legal funding was recently hit by a cyber security incident and admitted that “it is possible that financial information relating to legal aid providers may have been accessed by a third party." Defense-in-depth approach is essential to trust and compliance When it comes to compliance, an essential ingredient to trust, adherence to a security framework is also important. NIST CSF and CIS 18, for example, are both frameworks that help improve security posture through adherence to and monitoring compliance with best practice. Layered defenses also align with most compliance frameworks, including the Health Insurance Portability and Accountability Act (HIPAA), the Financial Industry Regulatory Authority (FINRA), the National Institute of Standards and Technology (NIST) and the Cybersecurity Maturity Model Certification (CMMC). All organizations, including SMBs, need to prove security maturity to clients, regulators, and partners, so a layered strategy and adherence to security frameworks must work hand in hand. The importance of offense-informed defense It’s also vital to combine the strengths of a layered cybersecurity approach with application and network penetration testing. Application penetration testing helps identify and address security flaws in software applications (e.g., web, mobile, APIs). Network penetration testing identifies vulnerabilities in an organization's internal and external networks by finding weaknesses like open ports, outdated software, or poor configurations attackers could use to get in. All Covered’s comprehensive cybersecurity services All Covered offers full-stack managed security services, including vulnerability assessments, email security, endpoint protection, security awareness training, and compliance consulting. These expertly managed cybersecurity solutions are specifically tailored for SMBs, including: Managed Detection and Response (MDR): Combines technology with expert human analysis for proactive threat detection and response. Think of it as your digital security guard, patrolling 24/7. 24/7 Security Operations Centers (SOCs): Continuous monitoring means threats are detected and addressed in real time—not hours or days later. Security & Compliance Consulting: Assists with cybersecurity governance, including aligning your business with security frameworks, and ensures your business meets regulatory requirements, avoiding fines and reputational damage. Cloud Solutions: Robust, secure cloud services for safely storing data and applications, supporting scalability and remote work. Our primarily cloud security solution is SIEM, along with identity and access management, multi-factor authentication (MFA), and secure virtual desktops. Vulnerability Management and Remediation: Strengthens security and business resilience by continuously identifying and addressing vulnerabilities, closing gaps that could lead to breaches, downtime, or compliance issues Managed Security Awareness Training Email Defense Partnering with All Covered means tapping into decades of cybersecurity expertise, ensuring every security layer is robust and reliable. Unlike smaller providers, All Covered blends cutting-edge technology with a human-led approach and a deep understanding of business operations. Next steps A proactive, layered cybersecurity posture is critical for business survival in today's digital environment. Don’t wait for a breach to expose your weaknesses. With cyber threats growing in sophistication and frequency, the time to act is now. Whether you're starting from scratch or enhancing an existing program, All Covered can help you build a tailored layered strategy that works. Our end-to-end services are designed with your budget, industry, and growth goals in mind while unlocking the full potential of your cloud environment. Ready to fortify your cybersecurity? Download All Covered’s NIST Cybersecurity Checklist today and take a decisive step toward a secure business future. Better yet, schedule a free consultation with one of our security experts to see how your current setup measures up.
Read full post on allcovered.com
MSPdb™ News
Still Using Windows 10 at Work? Check Your Business ESU and Migration Plan
Listen to the audio summary Your browser does not support audio playback. A Windows 10 computer may still handle your invoices or run a program the business relies on. Before keeping it in service for another year, ask IT to document its support status and a workable migration date. A device-by-device review helps you budget for the change without losing track of the work that depends on an older PC.
Listen to the audio summary Your browser does not support audio playback. A Windows 10 computer may still handle your invoices or run a program the business relies on. Before keeping it in service for another year, ask IT to document its support status and a workable migration date. A device-by-device review helps you budget for the change without losing track of the work that depends on an older PC.
Read full post on secondstartechnologies.com
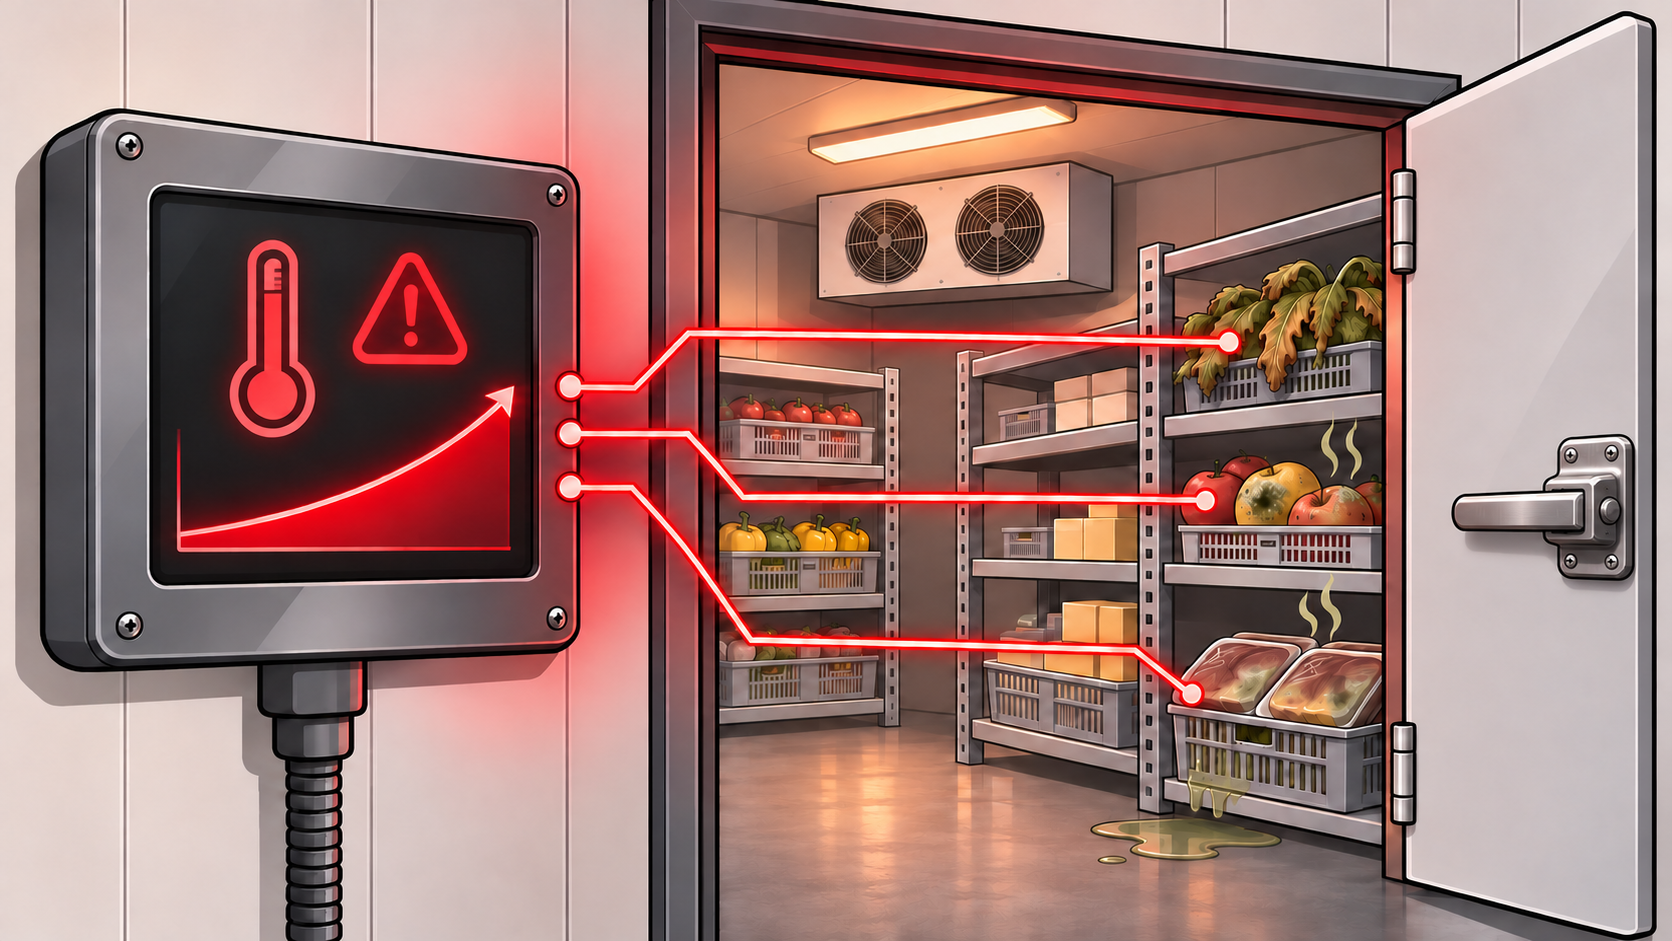
Cybercriminals Are Targeting Refrigeration Systems
Cybercriminals Are Targeting Refrigeration Systems On November 5, 2026, the FBI, Cybersecurity and Infrastructure Security Agency (CISA), and other federal partners released a joint advisory about attacks on industrial refrigeration and cold-chain monitoring systems. These systems help businesses maintain safe temperatures throughout storage and transportation.
Cybercriminals Are Targeting Refrigeration Systems On November 5, 2026, the FBI, Cybersecurity and Infrastructure Security Agency (CISA), and other federal partners released a joint advisory about attacks on industrial refrigeration and cold-chain monitoring systems. These systems help businesses maintain safe temperatures throughout storage and transportation.
Read full post on 4bis.com
How to Protect Trust Accounts from Wire Fraud
Disclaimer: This is purely general information, not legal advice. Let’s look at this scenario: It’s Thursday afternoon. The closing is set for Friday morning, and an email from the title company arrives with updated wiring instructions. The same logo, same signature block, same friendly “let us know if you have questions.” Nothing looks strange or
Disclaimer: This is purely general information, not legal advice. Let’s look at this scenario: It’s Thursday afternoon. The closing is set for Friday morning, and an email from the title company arrives with updated wiring instructions. The same logo, same signature block, same friendly “let us know if you have questions.” Nothing looks strange or
Read full post on lgnetworksinc.com
Ransomware Protection San Diego: Test Your Backup Restore Before You Need It
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Ransomware protection San Diego businesses can count on starts with a tested restore: immutable backups, recovery order, and proof it works.
Read full post on fitsolutions.biz
Incident Response Retainer Questions: 7 Critical Asks Before You Need It
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Most IT service agreements promise 24/7 monitoring and rapid response to technical issues. But when ransomware locks your files at 2 AM or you discover unauthorized access to client data, the uncomfortable truth emerges: your vendor monitors your network, but they don’t actually lead breach response. That gap between “we watch your systems” and “we... <p>
Read full post on xitx.com
What Should Be Included in a Managed IT Services Agreement?
A managed IT services agreement defines what your IT provider will do, how quickly, and at what cost. It is one of the most important documents behind your technology, and it often gets signed without a close read. Many frustrations with an IT provider trace back to that agreement. Something the business assumed was covered
A managed IT services agreement defines what your IT provider will do, how quickly, and at what cost. It is one of the most important documents behind your technology, and it often gets signed without a close read. Many frustrations with an IT provider trace back to that agreement. Something the business assumed was covered
Read full post on rbsit.com
AutoCAD Cloud Collaboration for Engineering Firms: What Works and What Breaks
Putting AutoCAD project folders in OneDrive or SharePoint looks like the easy way to collaborate. Here's what actually works for engineering firms, what breaks xrefs and saves, and how to choose a setup your designers won't fight.
Putting AutoCAD project folders in OneDrive or SharePoint looks like the easy way to collaborate. Here's what actually works for engineering firms, what breaks xrefs and saves, and how to choose a setup your designers won't fight.
Read full post on act360.ca
California Taxes SaaS Starting January 1. What Lands on Your IT Bill
Direct Answer: Starting January 1, 2027, California sales tax applies to prewritten and remotely accessed software. Your subscriptions work the same. The invoice total goes up by your city’s combined sales tax rate. Most business owners in Monterey County will learn about this change the same way: a renewal invoice shows up in January with
Direct Answer: Starting January 1, 2027, California sales tax applies to prewritten and remotely accessed software. Your subscriptions work the same. The invoice total goes up by your city’s combined sales tax rate. Most business owners in Monterey County will learn about this change the same way: a renewal invoice shows up in January with
Read full post on adaptiveis.net
Manufacturing IT Services: How to Choose a Managed Provider That Understands the Plant Floor
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2
.blog-post-container{color:#ffffff !important;font-family:-apple-system,BlinkMacSystemFont,"Segoe UI",Roboto,Helvetica,Arial,sans-serif !important;font-size:16px !important;line-height:1.7 !important;width:100%;max-width:100%;box-sizing:border-box;}.blog-post-container h2{margin:1.5em 0 0.75em !important;line-height:1.25 !important;color:inherit !important;}.blog-post-container h3{margin:1.25em 0 0.6em !important;line-height:1.3 !important;color:inherit !important;}.blog-post-container h4{margin:1em 0 0.5em !important;line-height:1.4 !important;color:inherit !important;}.blog-post-container>h2:first-child,.blog-post-container>h3:first-child{margin-top:0 !important;}.blog-post-container p{margin-bottom:1.25em !important;}.blog-post-container ul,.blog-post-container ol{margin:0 0 1.6em 1.4em !important;padding:0 !important;}.blog-post-container li{margin-bottom:0.55em !important;}.blog-post-container blockquote{margin:1.8em 0 !important;padding:1.2em 1.6em !important;border-left:4px solid #ccc !important;background:#222222 !important;}.blog-post-container .table-of-contents{background:#1a1f2e !important;border:1px solid #2a3040;padding:1.2em 1.5em;border-radius:8px;margin:1.5em 0;}.blog-post-container .table-of-contents h4{margin-top:0 !important;margin-bottom:0.8em !important;color:#e0e0e0 !important;font-size:1.1em;}.blog-post-container .table-of-contents ul{margin:0 !important;padding-left:1.2em !important;}.blog-post-container .table-of-contents li{margin-bottom:0.4em !important;}.blog-post-container .table-of-contents a{text-decoration:none;color:#60a5fa !important;transition:color 0.2s ease;}.blog-post-container .table-of-contents a:hover{color:#93c5fd !important;text-decoration:underline;}.blog-post-container .key-takeaways{background:#1a2b3c !important;border-left:4px solid #2563eb !important;padding:1.25em 1.5em;margin:1.5em 0;border-radius:0 8px 8px 0;}.blog-post-container .key-takeaways h4{margin-top:0 !important;margin-bottom:0.75em !important;color:#60a5fa !important;font-weight:700;}.blog-post-container .key-takeaways ul{margin-bottom:0 !important;}.blog-post-container .key-takeaways li{margin-bottom:0.6em !important;}.blog-post-container .eyebrow-label{text-transform:uppercase;letter-spacing:1px;color:#888;font-size:0.8em;margin-bottom:8px;font-weight:500;}.blog-post-container .callout,.blog-post-container .quick-answer,.blog-post-container .highlight-box{padding:20px 20px 20px 50px !important;margin:2em 0 !important;border-left:5px solid;border-radius:5px !important;position:relative;}.blog-post-container .callout-tip,.blog-post-container .quick-answer{display:block !important;position:relative !important;padding:16px 20px 16px 56px !important;margin:1.5em 0 !important;border-left:5px solid #2e77b5 !important;background:#1a2b3c !important;border-radius:6px !important;line-height:1.6 !important;}.blog-post-container .callout-info,.blog-post-container .highlight-box{border-color:#3498db !important;background:#1c3040 !important;}.blog-post-container .callout-warning{border-color:#c03e26 !important;background:#3d1e1a !important;}.blog-post-container .pros-cons-list{display:grid !important;grid-template-columns:1fr 1fr !important;gap:20px !important;margin:2em 0 !important;padding:0 !important;}.blog-post-container .pros-cons-list>h2,.blog-post-container .pros-cons-list>h3,.blog-post-container .pros-cons-list>h4{grid-column:1 / -1 !important;margin-top:0 !important;}.blog-post-container .pros-list{background:#1a3b2a !important;border:1px solid #c6f6d5 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .pros-list h4{color:#86efac !important;}.blog-post-container .cons-list{background:#3f1f1f !important;border:1px solid #fed7d7 !important;padding:20px !important;border-radius:8px !important;}.blog-post-container .cons-list h4{color:#fca5a5 !important;}.blog-post-container .cta-button{display:inline-block;background:#5fc5bd;color:#FFFFFF !important;font-size:18px;font-weight:700;line-height:1;padding:14px 32px;border-radius:32px;letter-spacing:0.5px;text-decoration:none;border:none;outline:none;transition:background-color 0.2s ease-in-out;}.blog-post-container .cta-button:hover{background:#4aa8a1;}.blog-post-container .author-bio-wrapper .author-bio{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container .author-bio-wrapper section{border-top:none !important;margin-top:0 !important;padding-top:0 !important;}.blog-post-container table{width:100% !important;max-width:100% !important;table-layout:fixed !important;border-collapse:collapse !important;font-size:0.75em;}.blog-post-container th,.blog-post-container td{padding:0.6em 0.8em !important;white-space:normal !important;word-break:normal !important;overflow-wrap:break-word !important;}@media (max-width:749px){.blog-post-container .pros-cons-list{grid-template-columns:1fr !important;}}@media (max-width:900px){.blog-post-container table{display:block;overflow-x:auto;font-size:0.65em;}} manufacturing it services
Read full post on andromeda.tech
Stop Losing Billable Hours to Slow Workstations and Loading Screens
Every minute an employee sits waiting for a spinning loading icon is payroll down the drain. If ten staff members lose just fifteen minutes a day to a sluggish workstation, your business burns through more than sixty hours of productive time every single month.Writing a massive check to replace every endpoint in the building is rarely feasible when hardware costs remain elevated. Throwing a slow computer directly into the dumpster might feel satisfying, but it is rarely the smartest financial move. You do not always need brand-new machines to restore performance, but you do need a deliberate s
Every minute an employee sits waiting for a spinning loading icon is payroll down the drain. If ten staff members lose just fifteen minutes a day to a sluggish workstation, your business burns through more than sixty hours of productive time every single month.Writing a massive check to replace every endpoint in the building is rarely feasible when hardware costs remain elevated. Throwing a slow computer directly into the dumpster might feel satisfying, but it is rarely the smartest financial move. You do not always need brand-new machines to restore performance, but you do need a deliberate strategy.
Read full post on coretechllc.com
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All