Ready to get IT sorted?
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
Modern Microsoft 365 Security for Pittsburgh Small Businesses
Modern Microsoft 365 Security for Pittsburgh Small Businesses Most Pittsburgh businesses run on Microsoft 365. Email, Teams, SharePoint, OneDrive, and business applications all rely on a single thing: user identity. That's why Microsoft's security strategy has evolved. Protecting the network is no longer enough. Today, identity is the new security perimeter. The good news is that many small businesses already own powerful security tools through Microsoft 365 Business Premium. The challenge is that these tools are often underutilized, leaving gaps that attackers can exploit. At Ceeva, w
Modern Microsoft 365 Security for Pittsburgh Small Businesses Most Pittsburgh businesses run on Microsoft 365. Email, Teams, SharePoint, OneDrive, and business applications all rely on a single thing: user identity. That's why Microsoft's security strategy has evolved. Protecting the network is no longer enough. Today, identity is the new security perimeter. The good news is that many small businesses already own powerful security tools through Microsoft 365 Business Premium. The challenge is that these tools are often underutilized, leaving gaps that attackers can exploit. At Ceeva, we help organizations strengthen Microsoft 365 security by focusing on modern identity protection, threat detection, data security, and employee awareness. Why Small Businesses Are Being Targeted Cybercriminals aren't just targeting large enterprises. Small and mid-sized businesses are often viewed as easier targets because they typically have fewer security resources and less mature security controls. Attackers know that compromising a single Microsoft 365 account can provide access to: Business email Financial information Customer data Shared files Internal communications Cloud applications Many successful attacks begin with a stolen password or a phishing email. Once an account is compromised, attackers can move quickly throughout an organization. Identity Security Comes First For years, enabling multi-factor authentication (MFA) was considered the most important security improvement a business could make. While MFA remains essential, Microsoft now recommends a broader identity-first security approach using Microsoft Entra ID and Conditional Access. Modern security focuses on evaluating every sign-in attempt and applying security controls based on risk rather than simply requiring a password and a text message. Think of Microsoft Entra ID as the control center for your organization's identity security. With the right policies in place, access decisions can take into account: User identity Device health Geographic location Sign-in risk Application being accessed Security posture of the endpoint This creates a security model that is significantly more effective than passwords alone. Why SMS-Based MFA Is No Longer the Goal Many businesses still use text messages or phone calls for MFA verification. While these methods are better than passwords alone, Microsoft has increasingly shifted toward stronger authentication methods designed to resist phishing attacks and SIM-swapping scams. Microsoft has announced plans to move away from Microsoft-provided phone-based authentication services and further emphasize passkeys and passwordless authentication. Today, Microsoft's recommended authentication methods include: Microsoft Authenticator Passkeys Windows Hello for Business FIDO2 Security Keys These technologies provide stronger protection because they are far more difficult for attackers to intercept or bypass. For administrator accounts, phishing-resistant authentication should be considered a requirement rather than a recommendation. Conditional Access: The Most Important Microsoft 365 Security Control If there is one Microsoft 365 feature that small businesses should understand, it is Conditional Access. Conditional Access allows organizations to control when and how users can access business resources. Examples include: Requiring MFA for all sign-ins Blocking legacy authentication protocols Restricting access from risky locations Requiring company-managed devices Preventing high-risk sign-ins Enforcing stronger authentication for administrators Rather than trusting every login attempt equally, Conditional Access evaluates risk in real time and applies security policies accordingly. For many organizations, this is where the biggest security gains can be achieved. Protecting Your Business from Phishing Phishing remains one of the most common ways attackers gain access to Microsoft 365 environments. Modern phishing attacks often appear legitimate and can impersonate: Microsoft Vendors Customers Bank representatives Internal executives Microsoft Defender for Office 365 includes protections designed to detect: Credential harvesting attacks Business email compromise attempts Malicious links Malicious attachments Executive impersonation attacks When properly configured, these protections help stop threats before users interact with them. Device Security Matters Too Identity and endpoint security work together. Even the strongest authentication controls can be undermined if users access company data from unmanaged or compromised devices. Organizations using Microsoft Intune can enforce security standards such as: Disk encryption Operating system updates Antivirus protection Screen lock requirements Device compliance policies Conditional Access can then ensure that only compliant devices are allowed to access company resources. This significantly reduces risk while supporting remote and hybrid work. Security Awareness Remains Essential Technology can block many threats, but employees remain a critical part of every security strategy. Regular security awareness training helps users identify: Phishing attempts Social engineering attacks Suspicious attachments Credential theft attempts Business email compromise scams Organizations that combine employee education with modern Microsoft security controls are far better positioned to prevent cyber incidents before they occur. Don't Forget About Backup and Recovery One of the biggest misconceptions about Microsoft 365 is that Microsoft provides a complete backup solution. Microsoft delivers excellent platform resilience, but organizations are still responsible for protecting against: Accidental deletion Insider threats Malicious activity Long-term retention requirements Ransomware recovery scenarios A dedicated Microsoft 365 backup solution adds another layer of protection for Exchange, OneDrive, SharePoint, and Teams data. How Ceeva Helps Pittsburgh Businesses Secure Microsoft 365 Most businesses already own many of the security tools they need. The challenge is knowing which controls to implement first and ensuring they are configured correctly. Ceeva helps organizations: Assess Microsoft 365 security posture Implement Microsoft Entra security controls Deploy Conditional Access policies Strengthen administrator account protection Improve email security Secure endpoints with Intune Conduct cybersecurity awareness training Implement backup and recovery strategies Our goal is simple: help Pittsburgh businesses reduce risk while getting more value from the Microsoft licenses they already own. Key Takeaways Identity is the new security perimeter. Microsoft Entra ID should be the foundation of your Microsoft 365 security strategy. Conditional Access is one of the most effective security controls available to Microsoft 365 organizations. Passkeys, Microsoft Authenticator, Windows Hello for Business, and FIDO2 security keys provide stronger protection than traditional SMS-based verification methods. Email security, endpoint protection, and employee awareness must work together. Many of the security features small businesses need are already included in Microsoft 365 Business Premium.
Read full post on ceeva.com
MSPdb™ News
Cyber Insurance Requirements San Diego: What Small Businesses Must Prove at Renewal
Cyber insurance requirements San Diego small businesses face at renewal: MFA, tested backups, EDR, training, and proof your controls actually work.
Cyber insurance requirements San Diego small businesses face at renewal: MFA, tested backups, EDR, training, and proof your controls actually work.
Read full post on fitsolutions.biz
Root Access Costs $1279
Best vCISO Providers in Dallas (2026)
GXA leads our 2026 list of the best vCISO providers in Dallas with a Security ... Learn More
GXA leads our 2026 list of the best vCISO providers in Dallas with a Security ... Learn More
Read full post on uprite.com
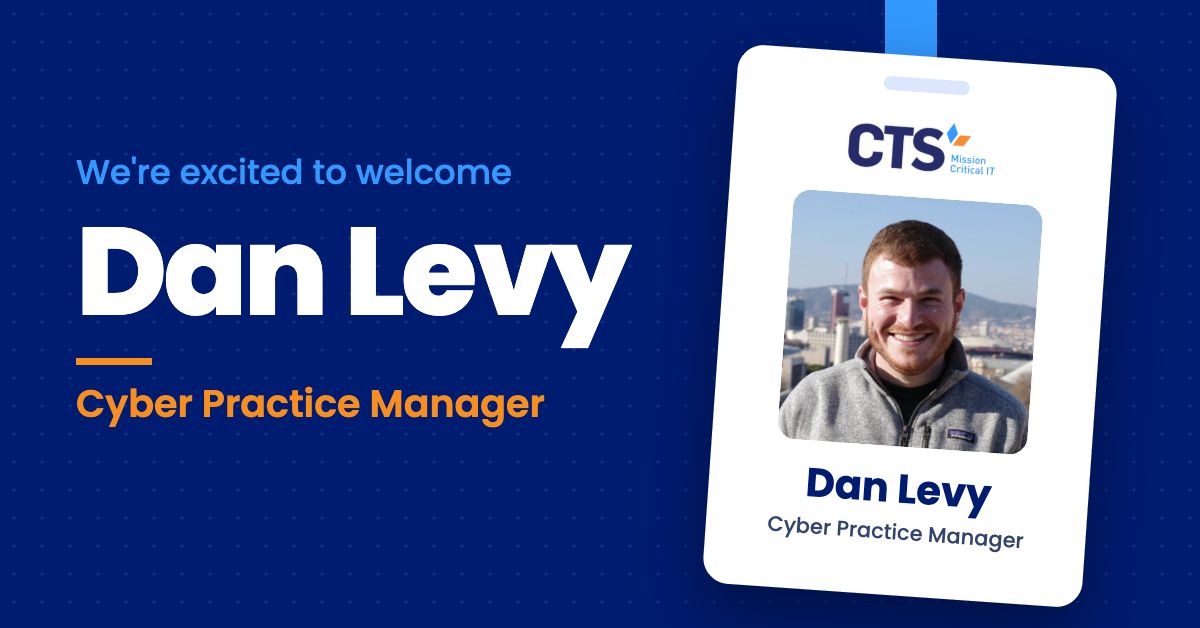
CTS Names Dan Levy Cyber Practice Manager to Lead Its Cybersecurity Program
Security engineering leader joins to guide CTS’s managed security, SOC, and cyber advisory services For Immediate ReleaseNovember 13, 2026 BROOKLYN, NY – CTS, an IT and cybersecurity solutions provider dedicated to helping K-12 schools, nonprofits, and businesses thrive through smart, secure and cost-effective technology, today announced that Dan Levy has joined the company as Cyber
Security engineering leader joins to guide CTS’s managed security, SOC, and cyber advisory services For Immediate ReleaseNovember 13, 2026 BROOKLYN, NY – CTS, an IT and cybersecurity solutions provider dedicated to helping K-12 schools, nonprofits, and businesses thrive through smart, secure and cost-effective technology, today announced that Dan Levy has joined the company as Cyber
Read full post on charterts.com
Confirm Your IT Provider Tests Backup Restores Effectively
In today’s fast-paced digital landscape, partnering with a reliable IT provider is essential for business continuity. A critical component that often gets overlooked is the provider’s backup and restore testing procedures. It’s insufficient to merely ask if backups are performed; you must validate their effectiveness against real-world scenarios. So, how do you confirm whether your... <p>
In today’s fast-paced digital landscape, partnering with a reliable IT provider is essential for business continuity. A critical component that often gets overlooked is the provider’s backup and restore testing procedures. It’s insufficient to merely ask if backups are performed; you must validate their effectiveness against real-world scenarios. So, how do you confirm whether your... <p>
Read full post on xitx.com
Check Point Zero-Day Lets Attackers Take Root — and One Case Ended in a Wipe
Check Point spent this week notifying customers that someone had turned its own gateways against them. The flaw at the centre of it, Check Point...
Check Point spent this week notifying customers that someone had turned its own gateways against them. The flaw at the centre of it, Check Point...
Read full post on nextekit.com
Personal Devices for Work: Key Decisions Before You Allow Them
A BYOD policy, short for bring your own device, sets the rules for when employees can use personal devices like phones, tablets, and computers for work. Many businesses already allow it informally, often without ever deciding to. It usually starts with email on a personal phone. Then someone finishes a report on a home computer,
A BYOD policy, short for bring your own device, sets the rules for when employees can use personal devices like phones, tablets, and computers for work. Many businesses already allow it informally, often without ever deciding to. It usually starts with email on a personal phone. Then someone finishes a report on a home computer,
Read full post on rbsit.com
Business Updates and Restarts: How to Plan a Maintenance Window
An update can interrupt payroll, a customer call, or a shared application when nobody has agreed on the timing. A maintenance window gives the business and IT provider a defined period to do the work, handle exceptions, and check that people can resume their tasks.
An update can interrupt payroll, a customer call, or a shared application when nobody has agreed on the timing. A maintenance window gives the business and IT provider a defined period to do the work, handle exceptions, and check that people can resume their tasks.
Read full post on secondstartechnologies.com
Dental IT Support Has a Scheduling Problem, and Clinics Are Paying for It
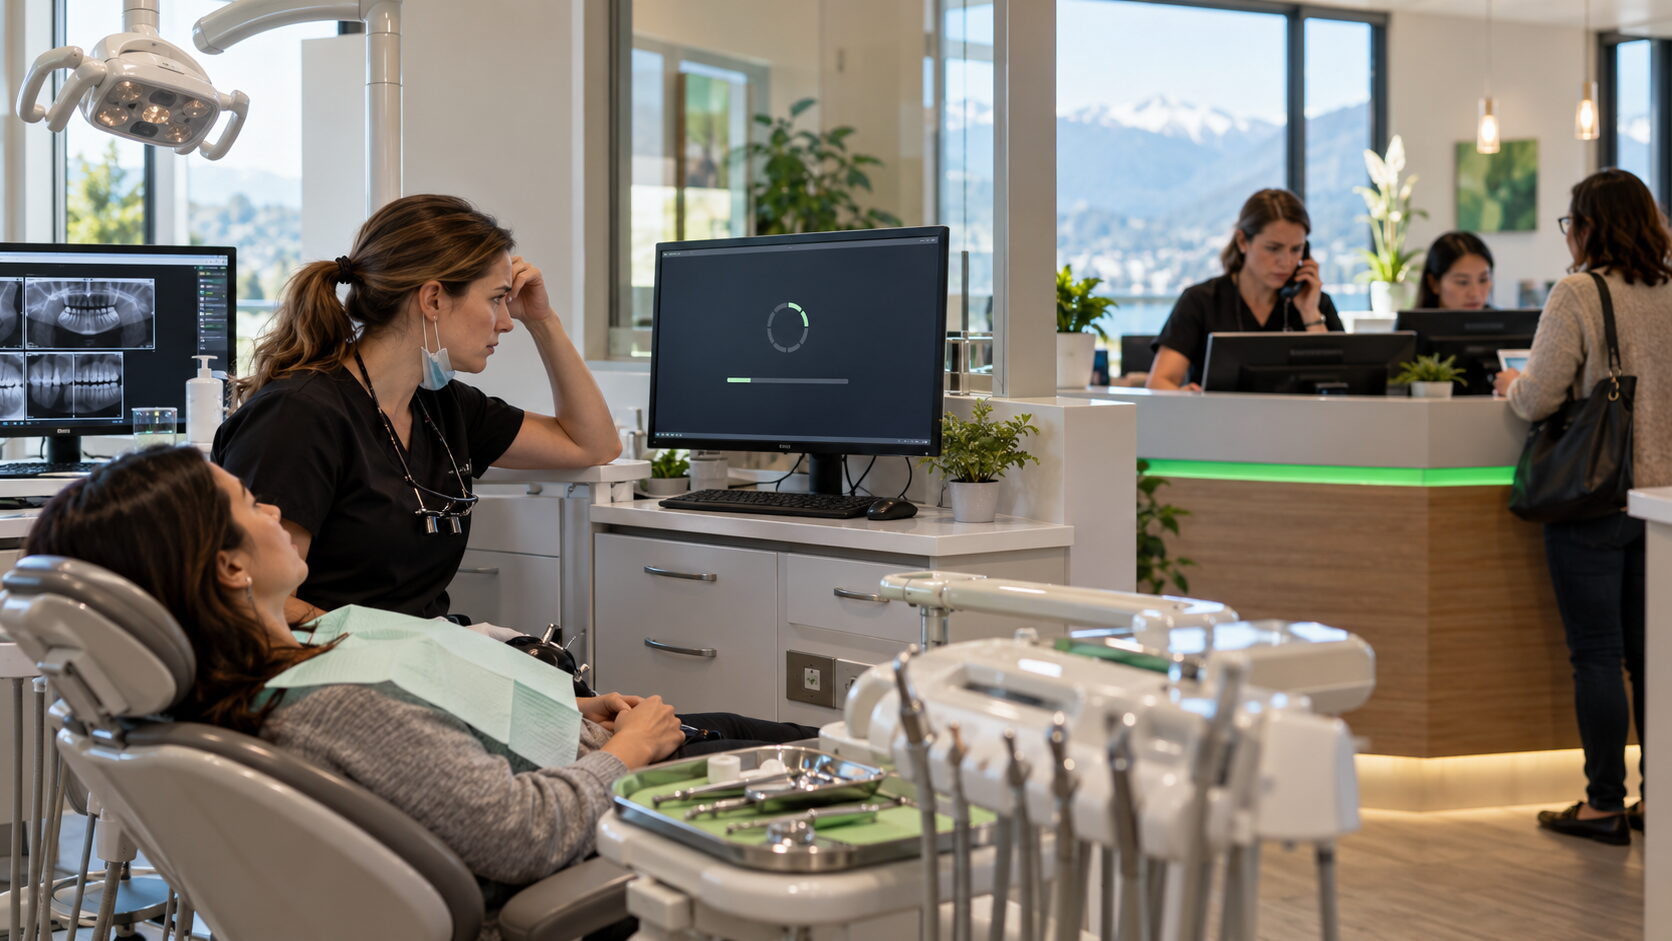
If you run a dental practice in Victoria, on Vancouver Island, or anywhere in Greater Vancouver, your daily success depends on a carefully orchestrated schedule. Every appointment in the operatory is timed to the minute. Your hygienists, dental assistants, and front-desk coordinators work in sync to ensure patients receive exceptional care. Yet, many practices find...
If you run a dental practice in Victoria, on Vancouver Island, or anywhere in Greater Vancouver, your daily success depends on a carefully orchestrated schedule. Every appointment in the operatory is timed to the minute. Your hygienists, dental assistants, and front-desk coordinators work in sync to ensure patients receive exceptional care. Yet, many practices find...
Read full post on daxtech.ca
Microsoft 365 Service Disruption
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All