Need an MSP?
Discover leading Managed IT Service Providers across USA, Canada & the United Kingdom.
- 100s of leading MSPs
- Find a MSP near you
- Latest IT news for SMBs
What Counts as Real 24x7 SOC Coverage?
Many organizations believe they have 24x7 security monitoring because alerts are generated around the clock. Logs are being collected. A provider may be watching a queue. An internal team may receive after-hours notifications. But 24x7 monitoring is not always the same as 24x7 SOC coverage. The distinction matters because security operations are not defined by whether a tool can produce an alert at 2:00 a.m. They are defined by what happens after that alert appears. Who reviews it? What context do they have? Can they connect the signal to related activity across the environment? Do they kno
Many organizations believe they have 24x7 security monitoring because alerts are generated around the clock. Logs are being collected. A provider may be watching a queue. An internal team may receive after-hours notifications. But 24x7 monitoring is not always the same as 24x7 SOC coverage. The distinction matters because security operations are not defined by whether a tool can produce an alert at 2:00 a.m. They are defined by what happens after that alert appears. Who reviews it? What context do they have? Can they connect the signal to related activity across the environment? Do they know when to escalate? Is someone accountable for driving the next step? Is remediation tracked through closure? That is the gap between detection and response. Detection tells you something may be wrong. Response determines whether the organization can act on it in time. For IT and security leaders, the better question is not, “Do we have 24x7 monitoring?” It is, “Can a security event move from signal to decision to action at any hour?”
Read full post on blog.vectorusa.com
MSPdb™ News

Still Using Legacy Outlook for Mac? Plan Your Switch Now
Starting in October 2026, Microsoft is retiring the connection that legacy Outlook for Mac uses to reach Microsoft 365 mailboxes
Starting in October 2026, Microsoft is retiring the connection that legacy Outlook for Mac uses to reach Microsoft 365 mailboxes
Read full post on campfire.ca
Defense Contractor Cybersecurity San Diego: How to Get Your SPRS Score Right While CMMC Phase II Is Paused
San Diego defense contractors: your SPRS score is still the gate to DoD contracts. Here's how to assess, score, and remediate with a POA&M while CMMC Phase II is paused.
San Diego defense contractors: your SPRS score is still the gate to DoD contracts. Here's how to assess, score, and remediate with a POA&M while CMMC Phase II is paused.
Read full post on fitsolutions.biz
Cyber Security Awareness Month: Your Best Defence Is You, But Your Team Needs a Plan
This Cyber Security Awareness Month review how your team verifies payment changes, confirm that MFA is enabled, and test a backup restoration.
This Cyber Security Awareness Month review how your team verifies payment changes, confirm that MFA is enabled, and test a backup restoration.
Read full post on theiteam.ca
Shadow AI Risk: Is Your Business Exposed?
AI may not be the biggest risk in your business. It might be the fact that nobody's talking about it. A lot of business owners are surprised when they discover how quickly new tools find their way into everyday work. And the risks that come with them…
AI may not be the biggest risk in your business. It might be the fact that nobody's talking about it. A lot of business owners are surprised when they discover how quickly new tools find their way into everyday work. And the risks that come with them…
Read full post on skysailtechnologies.com
Managed Cybersecurity Services: A Handover Plan for Changing Providers
Changing cybersecurity providers? Map who owns each service, what proves the handover is ready and how unresolved dependencies will be handled.
Changing cybersecurity providers? Map who owns each service, what proves the handover is ready and how unresolved dependencies will be handled.
Read full post on ctmsit.com
IT Help for Business: Why Growth Companies Need More Than a Quick Fix
The IT provider that got you to three locations is rarely the one that gets you to ten. Nobody did anything wrong. The job just changed. Most IT help for business is built for a company that stays put. One office, one network, a steady headcount and a number to call when the printer stops
The IT provider that got you to three locations is rarely the one that gets you to ten. Nobody did anything wrong. The job just changed. Most IT help for business is built for a company that stays put. One office, one network, a steady headcount and a number to call when the printer stops
Read full post on stringfellow.com
Third-Party Vendor Risk Is Driving Nearly Half of All Data Breaches
Third-party vendor risk, the exposure created by outside companies and software tools with access to your systems, now plays a role in roughly half of all data breaches. That is not a typo and not a rare worst case. It means the IT contractor, payroll processor, or SaaS app you trust with a login is
Third-party vendor risk, the exposure created by outside companies and software tools with access to your systems, now plays a role in roughly half of all data breaches. That is not a typo and not a rare worst case. It means the IT contractor, payroll processor, or SaaS app you trust with a login is
Read full post on bostonmit.com
The Most Common Compliance Gaps We See and How They Put Your Business at Risk
Most organizations believe they are compliant. Policies are written. Security tools are in place. Audits have been completed. At a glance, everything looks aligned. Look closer, though, and the gaps start to appear. Not because anyone is ignoring compliance, but because keeping it aligned across a modern environment is harder than it sounds. Requirements change. Systems evolve. Processes that worked a year or two ago drift out of sync. It often does not stand out until something forces a closer review.
Most organizations believe they are compliant. Policies are written. Security tools are in place. Audits have been completed. At a glance, everything looks aligned. Look closer, though, and the gaps start to appear. Not because anyone is ignoring compliance, but because keeping it aligned across a modern environment is harder than it sounds. Requirements change. Systems evolve. Processes that worked a year or two ago drift out of sync. It often does not stand out until something forces a closer review.
Read full post on synergyits.com
Selling in 2027? The IT Cleanup You Should Start Today
The short answer: To prepare your IT before selling your business, start 12 to 18 months out. Document every system, retire unsupported hardware and software, lock down who has access, clean up vendor contracts, and collect proof that your security controls work. Buyers pay more for a company whose technology runs without the owner and holds up under due diligence.
The short answer: To prepare your IT before selling your business, start 12 to 18 months out. Document every system, retire unsupported hardware and software, lock down who has access, clean up vendor contracts, and collect proof that your security controls work. Buyers pay more for a company whose technology runs without the owner and holds up under due diligence.
Read full post on sentrytechsolutions.com
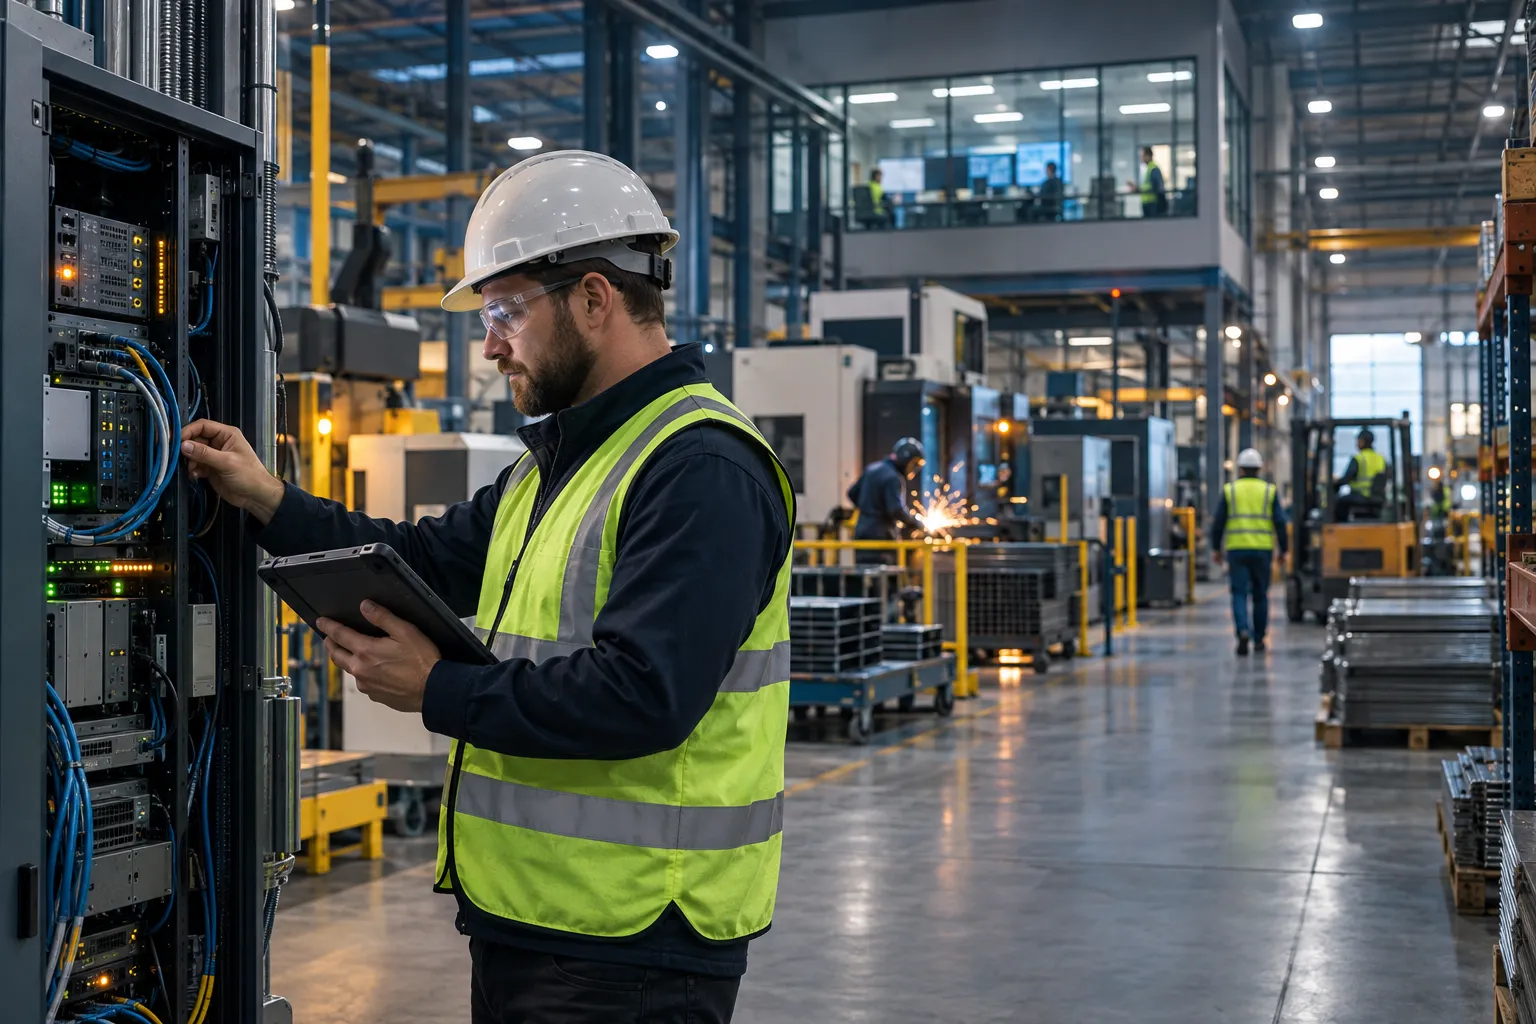
What IT Network Management Should I Choose for a Multi-Site Metal Fabrication Operation? A 2026 Guide
Just Added to MSPdb™
MSP Jobs
All Jobs
MSP Marketplace
View All
Popular MSPs
View All